
Vulnerability Scanning
1、Vulnerability scanning with Nmap Scripting Engine
the Nmap Script Engine provide a alrge number of script that can e used to perform a range of automated task to evaluate remote system .a windowsxp system with a vulnerable SMB service is used for this test .so first ,we must set up the windows xp system ,one of the most effective way is to referennce the script.db file that is located ninthe nmap script directory .
we use the command to look the scripts : cat /usr/share/nmap/scripts/script.db |more

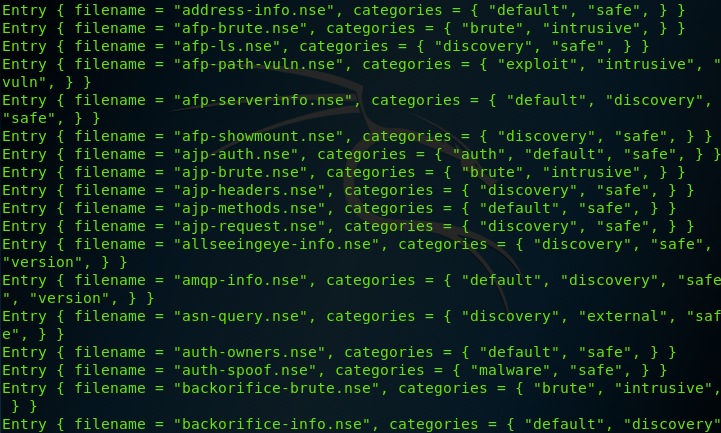
the category name for vulnerabliity scanning scripts is vuln, to identify all vunerability scripts , one would need to grep for the vuln and then extract the filename for each script with the cut command. this can be seen in hte folloeing truncated output:
grep vuln /usr/share/nmap/script/script.db |cut -d "\" -f 2
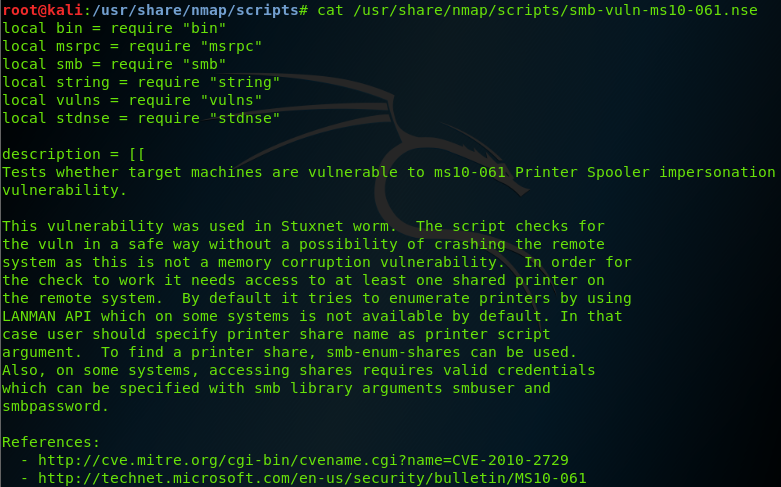

a vulnerability scan may be as simple as establishing a TCP connection with the remote service and identifying of probes and specially crafted requests may be sent to remote service in attempt to solicit responses that unique to services that vulnerable to a specific attack , in the example the NSE vulnerability script provided the vulnerability scan will actually try to exploit the vulnerability if the unsafe parameter activated.
2、 Vulnerability scanning with MSF auxiliary modules
Vulnerability Scanning的更多相关文章
- Vulnerability Scanning Tools
Category:Vulnerability Scanning Tools - OWASP https://www.owasp.org/index.php/Category:Vulnerability ...
- metasploit 学习笔记-VULNERABILITY SCANNING
使用漏洞扫描器会在网络上产生大量流量,因此如果你不希望被发现踪迹时,不要使用漏洞扫描器。 The Basic Vulnerability Scan 漏洞扫描器的质量很大程度上取决于它自带的漏洞特征库。 ...
- IIS安全工具UrlScan介绍 ASP.NET 两种超强SQL 注入免费解决方案( 基于IIS,使用免费工具) 批改或隐藏IIS7.5的Server头信息 移除X-Powered-By,MVC,ASP.NET_SessionId 的 HTTP头或者cookie名称
微软给了我们一个很好的工具用来使IIS安全的运行-------UrlScan,下面是它的配置文件介绍 [options]UseAllowVerbs=1 ; 若为1,则使用 ...
- Day 4 @ RSA Conference Asia Pacific & Japan 2016
09.00 – 09.45 hrs Advanced Malware and the Cloud: The New Concept of 'Attack Fan-out' Krishna Naraya ...
- nmap -- write a nmap script
漏洞扫描 --编写Nmap脚本 2006年12月份,Nmap4.21 ALPHA1版增加脚本引擎,并将其作为主线代码的一部分.NSE脚本库现在已经有400多个脚本.覆盖了各种不同的网络机制(从SMB漏 ...
- Magic Quadrant for Security Information and Event Management
https://www.gartner.com/doc/reprints?id=1-4LC8PAW&ct=171130&st=sb Summary Security and risk ...
- 微服务架构 - 基于Harbor构建本地镜像仓库
之前写过<搭建docker本地镜像仓库并提供权限校验及UI界面>文章,然后有同仁评论道这样做太复杂了,如果Harbor来搭建会更简单同时功能也更强大.于是抽时间研究了基于Harbor构建本 ...
- An overview of network penetration testing
1. an SQLi vulnerability will allow you to do the following query the database using select statem ...
- Docker容器学习梳理 - 基础知识(2)
之前已经总结了Docker容器学习梳理--基础知识(1),但是不够详细,下面再完整补充下Docker学习的一些基础. Docker是个什么东西 Docker是一个程序运行.测试.交付的开放平台,Doc ...
随机推荐
- Redhat6.4安装Oracle 11gr2 64位 注意事项
安装步骤略, 安装步骤参考:https://www.cnblogs.com/jhlong/p/5442459.html 注意的是,会出现找不到一些依赖库,我根据光盘已有的库安装了所有64位的依赖库,强 ...
- 允许外网连接到云服务器的mongodb服务器
通过 vi /etc/mongdb.conf 修改bind_ip 进行配置.
- 第二部分之AOF持久化(第十一章)
AOF持久化是通过保存Redis服务器所执行的写命令来记录数据库状态的.被写入AOF文件的所有命令都是以Redis的命令请求协议格式(纯文本)保存的. 一,AOF持久化的实现 1.命令追加 当AOF持 ...
- Linux(Ubuntu 16) 下Java开发环境的配置(一)------JDK的配置
前言: 本文介绍的是通用的安装方法,一般linux系统均可使用该方法安装.本文以Java8环境为例进行配置. 1.JDK的下载 进入java下载页(http://www.oracle.com/te ...
- 简单实现计算机上多个jdk环境切换
实现多个jdk环境切换,大致有两种方式 安装两个jdk,并配置相应的环境变量,在java的控制面板中修改设置 非主要的jdk仅仅是用来测试,并不常用,故只要让ide配置对应的jdk位置就可以了,属于懒 ...
- block,inline,inline-block区别
block:多個元素豎直排列,每個元素單獨占一行,寬高可以設置,padding.margin可以設置: inline:多個元素占一行,一行放不下了,才轉入下一行,寬高不能設置,水平的padding.m ...
- springmvc解决中文乱码问题
1 第一种情况(get接收参数): 最近在用solr做一个搜索服务,发布给手机和pc等客户端调用,调用方式为: http://www.ganbo.search/search?q="手机& ...
- vivado place30-378
AR# 60131 Vivado Placer - [Place 30-378] Input pin of input buffer has an illegal connection to a lo ...
- DesigningFormsinAccess2010
- Quartus13.1全编译出现引脚错误(神级bug)
BUG现象:分配完管脚后全编译出现如下错误. Error (171172):Detected confilicting assignments for the following nodes.Erro ...