
bWAPP----OS Command Injection
OS Command Injection
界面:

给一个域名,它帮你返回DNS
代码:
 1 <div id="main">

 2

 3     <h1>OS Command Injection</h1>

 4

 5     <form action="<?php echo($_SERVER["SCRIPT_NAME"]);?>" method="POST">

 6

 7         <p>

 8

 9         <label for="target">DNS lookup:</label>

10         <input type="text" id="target" name="target" value="www.nsa.gov">

11

12         <button type="submit" name="form" value="submit">Lookup</button>

13

14         </p>

15

16     </form>

17     <?php

18

19     if(isset($_POST["target"]))                                                      //获取域名,如果存在输入

20     {

21

22         $target = $_POST["target"];

23

24         if($target == "")                                                           //如果域名为空

25         {

26

27             echo "<font color=\"red\">Enter a domain name...</font>";              //请输入域名

28

29         }

30

31         else

32         {

33

34             echo "<p align=\"left\">" . shell_exec("nslookup  " . commandi($target)) . "</p>";

35

36         }

37

38     }

39

40     ?>

41

42 </div>
shell_exec — 通过 shell 环境执行命令,并且将完整的输出以字符串的方式返回。
防御部分
 1 function commandi($data)

 2 {

 3

 4     switch($_COOKIE["security_level"])

 5     {

 6

 7         case "0" :

 8

 9             $data = no_check($data);

10             break;

11

12         case "1" :

13

14             $data = commandi_check_1($data);

15             break;

16

17         case "2" :

18

19             $data = commandi_check_2($data);

20             break;

21

22         default :

23

24             $data = no_check($data);

25             break;

26

27     }

28

29     return $data;

30

31 }

32

33 ?>
1.low
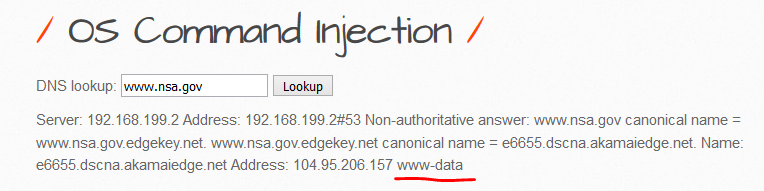
low级别没有过滤
加一个;就能实现恶意

2.medium
1 function commandi_check_1($data)

2 {

3

4     $input = str_replace("&", "", $data);

5     $input = str_replace(";", "", $input);

6

7     return $input;

8

9 }
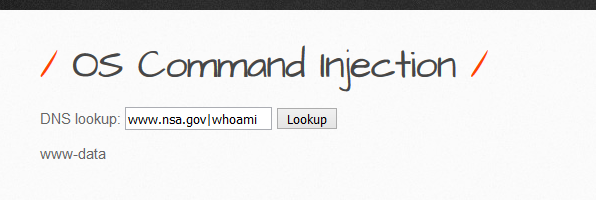
过滤了&和;将他们替换为空
用 | 可以绕过
3.high
1 function commandi_check_2($data)

2 {

3

4     return escapeshellcmd($data);

5

6 }
escapeshellcmd函数功能:
反斜线(\)会在以下字符之前插入: &#;`|*?~<>^()[]{}$\, \x0A 和 \xFF。 ' 和 " 仅在不配对儿的时候被转义。 在 Windows 平台上,所有这些字符以及 % 和 ! 字符都会被空格代替。
bWAPP----OS Command Injection的更多相关文章
- bWAPP----HTML OS Command Injection - Blind
OS Command Injection - Blind 先上代码,他判断了win还是linux然后进行了ping但是结果并没有返回. 1 <div id="main"> ...
- Portswigger web security academy:OS command injection
Portswigger web security academy:OS command injection 目录 Portswigger web security academy:OS command ...
- DVWA之命令注入(command injection)
Command injection就是指通过提交恶意构造的参数破坏命令语句结构,从而达到执行恶意命令的目的 LOW 无论是Windows还是Linux,都可以使用&&连接多个命令 执行 ...
- DVWA Command Injection 通关教程
Command Injection 介绍 命令注入(Command Injection),对一些函数的参数没有做过滤或过滤不严导致的,可以执行系统或者应用指令(CMD命令或者bash命令)的一种注入攻 ...
- DVWA Command Injection 解析
命令注入,即 Command Injection.是指通过提交恶意构造的参数破坏命令语句结构,从而达到执行恶意命令的目的. 在Web应用中,有时候会用到一些命令执行的函数,如php中system.ex ...
- DWVA-命令注入漏洞闯关(Command Injection)
前言 Vulnerability: Command Injection LOW级别 代码: <?php if( isset( $_POST[ 'Submit' ] ) ) { // 几首一个变量 ...
- DVWA之Command Injection
Command Injection Command Injection,即命令注入,是指通过提交恶意构造的参数破坏命令语句结构,从而达到执行恶意命令的目的.PHP命令注入攻击漏洞是PHP应用程序中常见 ...
- DVWA(四):Command Injection 全等级命令注入
Command Injection : 命令注入(Command Injection),对一些函数的参数没有做好过滤而导致用户可以控制输入的参数,使其恶意执行系统命令或这cmd.bash指令的一种注入 ...
- DVWA靶场之Command Injection(命令行注入)通关
Command Injection Low: <?php if( isset( $_POST[ 'Submit' ] ) ) { // Get input $target = $_REQUES ...
随机推荐
- codevs1298, hdu1392 (凸包模板)
题意: 求凸包周长. 总结: 测试模板. 代码: #include <iostream> #include <cstdio> #include <cstring> ...
- 【Azure Developer】使用.Net Core解析JSON的笔记
在C#中解析JSON的一些历史代码记录,分别记录针对各种情况的解析方式. DLL的引用 using Newtonsoft.Json; using Newtonsoft.Json.Linq; 需要使用的 ...
- pycharm调试bug Process finished with exit code -1073740791 (0xC0000409)
我经常py代码出错 控制台只提示这个 Process finished with exit code -1073740791 (0xC0000409) 但是根本没有报错原因 首先我们应该改一下pych ...
- this.getResolve is not a function VUE中使用sass
1. 安装以下依赖 npm install node-sass --save-dev //安装node-sass npm install sass-loader --save-dev //安装sass ...
- Java面试题集(二)list与Map相关知识(1.2)
前言: 在平常的写java程序中,常用除了8种常用数据类型,String对象外,还有集合类,例如ArrayList,HashMap等,这些最常用. 一.List接口 List接口为Collection ...
- 数据结构(C++)——顺序栈
顺序栈结构 #include<iostream> #define MaxSize 50 using namespace std; typedef int ElemType; typedef ...
- 使用Guava RateLimiter限流入门到深入
前言 在开发高并发系统时有三把利器用来保护系统:缓存.降级和限流 缓存: 缓存的目的是提升系统访问速度和增大系统处理容量 降级: 降级是当服务出现问题或者影响到核心流程时,需要暂时屏蔽掉,待高峰或者问 ...
- 云服务器部署scrapyd爬虫
Scrapyd部署爬虫项目 GitHub:https://github.com/scrapy/scrapyd API 文档:http://scrapyd.readthedocs.io/en/stabl ...
- 【QT】 QThread部分源码浅析
本文章挑出QThread源码中部分重点代码来说明QThread启动到结束的过程是怎么调度的.其次因为到了Qt4.4版本,Qt的多线程就有所变化,所以本章会以Qt4.0.1和Qt5.6.2版本的源码来进 ...
- 读书笔记:《数据结构与算法分析Java语言描述》
目录 第 3 章 表.栈和队列 3.2 表 ADT 3.2.1 表的简单数组实现 3.2.2 简单链表 3.3 Java Collections API 中的表 3.3.1 Collection 接口 ...