
SOAP Only Authentication Using C#
Monday, February 9, 2015
SOAP Only Authentication Using C#
Obviously authentication is the first major problem that needs to be solved before you can get into the meat of your application. If you browse through the CRM SDK under the "Write mobile and modern apps" topic you'll notice that using OAuth is the recommended approach to authentication. Which is fine but in order to do so you'll need to register your application ahead of time with Active Directory (Online or On Premise) which isn't always desirable or possible.
An alternative approach is to communicate with CRM using raw SOAP requests. Using this approach we can authenticate to CRM Online or On Premise IFD organizations with a user's same credentials and return back the correct security tokens that need to accompany any future requests. Obviously working directly with the SOAP XML isn't that pretty but it can be done. This should provide a starting point for converting to other languages. I'll be posting examples in the near future for PHP, Java, JavaScript (mobile application), and VBA.
I've put together a couple of sample applications, the first is a C# console application that can authenticate to CRM using SOAP requests and then returns back the name of the logged in user.
https://github.com/jlattimer/CRMSoapAuthCSharp
The second is a mobile application using the Xamarin platform. If you aren't familiar with Xamarin it allows you to develop native iOS, Android, and Windows mobile applications using C# and Visual Studio. Unfortunately for us CRM developers the SDK assemblies have dependencies on other .NET assemblies that are not supported by Xamarin which makes the standard versions of the CRM SDK assemblies not viable (mobile versions here + other mobile samples). Full disclosure: Xamarin supports the developer community by giving Microsoft MVPs complimentary licenses - which I appreciate greatly!
The second sample does the same thing except it is in the form of a Xamarin iOS (requires Xamarin to run) application.
https://github.com/jlattimer/CRMSoapAuthXamarin
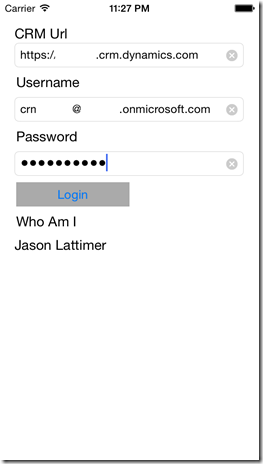
The heavy lifting for generating the SOAP headers looks like this:
| using System; | |
| using System.IO; | |
| using System.Net; | |
| using System.Security.Cryptography; | |
| using System.Text; | |
| using System.Xml; | |
| namespace CRMSoapAuthCSharp | |
| { | |
| class CrmAuth | |
| { | |
| /// <summary> | |
| /// Gets a CRM Online SOAP header & expiration. | |
| /// </summary> | |
| /// <param name="username">Username of a valid CRM user.</param> | |
| /// <param name="password">Password of a valid CRM user.</param> | |
| /// <param name="url">The Url of the CRM Online organization (https://org.crm.dynamics.com).</param> | |
| /// <returns>An object containing the SOAP header and expiration date/time of the header.</returns> | |
| public CrmAuthenticationHeader GetHeaderOnline(string username, string password, string url) | |
| { | |
| if (!url.EndsWith("/")) | |
| url += "/"; | |
| string urnAddress = GetUrnOnline(url); | |
| DateTime now = DateTime.Now; | |
| StringBuilder xml = new StringBuilder(); | |
| xml.Append("<s:Envelope xmlns:s=\"http://www.w3.org/2003/05/soap-envelope\" xmlns:a=\"http://www.w3.org/2005/08/addressing\" xmlns:u=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-utility-1.0.xsd\">"); | |
| xml.Append("<s:Header>"); | |
| xml.Append("<a:Action s:mustUnderstand=\"1\">http://schemas.xmlsoap.org/ws/2005/02/trust/RST/Issue</a:Action>"); | |
| xml.Append("<a:MessageID>urn:uuid:" + Guid.NewGuid() + "</a:MessageID>"); | |
| xml.Append("<a:ReplyTo>"); | |
| xml.Append("<a:Address>http://www.w3.org/2005/08/addressing/anonymous</a:Address>"); | |
| xml.Append("</a:ReplyTo>"); | |
| xml.Append("<a:To s:mustUnderstand=\"1\">https://login.microsoftonline.com/RST2.srf</a:To>"); | |
| xml.Append("<o:Security s:mustUnderstand=\"1\" xmlns:o=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-secext-1.0.xsd\">"); | |
| xml.Append("<u:Timestamp u:Id=\"_0\">"); | |
| xml.Append("<u:Created>" + now.ToUniversalTime().ToString("o") + "</u:Created>"); | |
| xml.Append("<u:Expires>" + now.AddMinutes(60).ToUniversalTime().ToString("o") + "</u:Expires>"); | |
| xml.Append("</u:Timestamp>"); | |
| xml.Append("<o:UsernameToken u:Id=\"uuid-" + Guid.NewGuid() + "-1\">"); | |
| xml.Append("<o:Username>" + username + "</o:Username>"); | |
| xml.Append("<o:Password>" + password + "</o:Password>"); | |
| xml.Append("</o:UsernameToken>"); | |
| xml.Append("</o:Security>"); | |
| xml.Append("</s:Header>"); | |
| xml.Append("<s:Body>"); | |
| xml.Append("<trust:RequestSecurityToken xmlns:trust=\"http://schemas.xmlsoap.org/ws/2005/02/trust\">"); | |
| xml.Append("<wsp:AppliesTo xmlns:wsp=\"http://schemas.xmlsoap.org/ws/2004/09/policy\">"); | |
| xml.Append("<a:EndpointReference>"); | |
| xml.Append("<a:Address>urn:" + urnAddress + "</a:Address>"); | |
| xml.Append("</a:EndpointReference>"); | |
| xml.Append("</wsp:AppliesTo>"); | |
| xml.Append("<trust:RequestType>http://schemas.xmlsoap.org/ws/2005/02/trust/Issue</trust:RequestType>"); | |
| xml.Append("</trust:RequestSecurityToken>"); | |
| xml.Append("</s:Body>"); | |
| xml.Append("</s:Envelope>"); | |
| HttpWebRequest request = (HttpWebRequest)WebRequest.Create("https://login.microsoftonline.com/RST2.srf"); | |
| ASCIIEncoding encoding = new ASCIIEncoding(); | |
| byte[] bytesToWrite = encoding.GetBytes(xml.ToString()); | |
| request.Method = "POST"; | |
| request.ContentLength = bytesToWrite.Length; | |
| request.ContentType = "application/soap+xml; charset=UTF-8"; | |
| Stream newStream = request.GetRequestStream(); | |
| newStream.Write(bytesToWrite, 0, bytesToWrite.Length); | |
| newStream.Close(); | |
| HttpWebResponse response = (HttpWebResponse)request.GetResponse(); | |
| Stream dataStream = response.GetResponseStream(); | |
| if (dataStream == null) | |
| return null; | |
| StreamReader reader = new StreamReader(dataStream); | |
| XmlDocument x = new XmlDocument(); | |
| x.Load(reader); | |
| XmlNodeList cipherElements = x.GetElementsByTagName("CipherValue"); | |
| string token1 = cipherElements[0].InnerText; | |
| string token2 = cipherElements[1].InnerText; | |
| XmlNodeList keyIdentiferElements = x.GetElementsByTagName("wsse:KeyIdentifier"); | |
| string keyIdentifer = keyIdentiferElements[0].InnerText; | |
| XmlNodeList tokenExpiresElements = x.GetElementsByTagName("wsu:Expires"); | |
| string tokenExpires = tokenExpiresElements[0].InnerText; | |
| CrmAuthenticationHeader authHeader = new CrmAuthenticationHeader | |
| { | |
| Header = CreateSoapHeaderOnline(url, keyIdentifer, token1, token2), | |
| Expires = DateTimeOffset.Parse(tokenExpires).UtcDateTime | |
| }; | |
| return authHeader; | |
| } | |
| /// <summary> | |
| /// Gets a CRM Online SOAP header. | |
| /// </summary> | |
| /// <param name="url">The Url of the CRM Online organization (https://org.crm.dynamics.com).</param> | |
| /// <param name="keyIdentifer">The KeyIdentifier from the initial request.</param> | |
| /// <param name="token1">The first token from the initial request.</param> | |
| /// <param name="token2">The second token from the initial request.</param> | |
| /// <returns>The XML SOAP header to be used in future requests.</returns> | |
| private static string CreateSoapHeaderOnline(string url, string keyIdentifer, string token1, string token2) | |
| { | |
| StringBuilder xml = new StringBuilder(); | |
| xml.Append("<s:Header>"); | |
| xml.Append("<a:Action s:mustUnderstand=\"1\">http://schemas.microsoft.com/xrm/2011/Contracts/Services/IOrganizationService/Execute</a:Action>"); | |
| xml.Append("<Security xmlns=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-secext-1.0.xsd\">"); | |
| xml.Append("<EncryptedData Id=\"Assertion0\" Type=\"http://www.w3.org/2001/04/xmlenc#Element\" xmlns=\"http://www.w3.org/2001/04/xmlenc#\">"); | |
| xml.Append("<EncryptionMethod Algorithm=\"http://www.w3.org/2001/04/xmlenc#tripledes-cbc\"/>"); | |
| xml.Append("<ds:KeyInfo xmlns:ds=\"http://www.w3.org/2000/09/xmldsig#\">"); | |
| xml.Append("<EncryptedKey>"); | |
| xml.Append("<EncryptionMethod Algorithm=\"http://www.w3.org/2001/04/xmlenc#rsa-oaep-mgf1p\"/>"); | |
| xml.Append("<ds:KeyInfo Id=\"keyinfo\">"); | |
| xml.Append("<wsse:SecurityTokenReference xmlns:wsse=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-secext-1.0.xsd\">"); | |
| xml.Append("<wsse:KeyIdentifier EncodingType=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-soap-message-security-1.0#Base64Binary\" ValueType=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-x509-token-profile-1.0#X509SubjectKeyIdentifier\">" + keyIdentifer + "</wsse:KeyIdentifier>"); | |
| xml.Append("</wsse:SecurityTokenReference>"); | |
| xml.Append("</ds:KeyInfo>"); | |
| xml.Append("<CipherData>"); | |
| xml.Append("<CipherValue>" + token1 + "</CipherValue>"); | |
| xml.Append("</CipherData>"); | |
| xml.Append("</EncryptedKey>"); | |
| xml.Append("</ds:KeyInfo>"); | |
| xml.Append("<CipherData>"); | |
| xml.Append("<CipherValue>" + token2 + "</CipherValue>"); | |
| xml.Append("</CipherData>"); | |
| xml.Append("</EncryptedData>"); | |
| xml.Append("</Security>"); | |
| xml.Append("<a:MessageID>urn:uuid:" + Guid.NewGuid() + "</a:MessageID>"); | |
| xml.Append("<a:ReplyTo>"); | |
| xml.Append("<a:Address>http://www.w3.org/2005/08/addressing/anonymous</a:Address>"); | |
| xml.Append("</a:ReplyTo>"); | |
| xml.Append("<a:To s:mustUnderstand=\"1\">" + url + "XRMServices/2011/Organization.svc</a:To>"); | |
| xml.Append("</s:Header>"); | |
| return xml.ToString(); | |
| } | |
| /// <summary> | |
| /// Gets the correct URN Address based on the Online region. | |
| /// </summary> | |
| /// <param name="url">The Url of the CRM Online organization (https://org.crm.dynamics.com).</param> | |
| /// <returns>URN Address.</returns> | |
| private static string GetUrnOnline(string url) | |
| { | |
| if (url.ToUpper().Contains("CRM2.DYNAMICS.COM")) | |
| return "crmsam:dynamics.com"; | |
| if (url.ToUpper().Contains("CRM4.DYNAMICS.COM")) | |
| return "crmemea:dynamics.com"; | |
| if (url.ToUpper().Contains("CRM5.DYNAMICS.COM")) | |
| return "crmapac:dynamics.com"; | |
| return "crmna:dynamics.com"; | |
| } | |
| /// <summary> | |
| /// Gets a CRM On Premise SOAP header & expiration. | |
| /// </summary> | |
| /// <param name="username">Username of a valid CRM user.</param> | |
| /// <param name="password">Password of a valid CRM user.</param> | |
| /// <param name="url">The Url of the CRM On Premise (IFD) organization (https://org.domain.com).</param> | |
| /// <returns>An object containing the SOAP header and expiration date/time of the header.</returns> | |
| public CrmAuthenticationHeader GetHeaderOnPremise(string username, string password, string url) | |
| { | |
| if (!url.EndsWith("/")) | |
| url += "/"; | |
| string adfsUrl = GetAdfs(url); | |
| if (adfsUrl == null) | |
| return null; | |
| DateTime now = DateTime.Now; | |
| string urnAddress = url + "XRMServices/2011/Organization.svc"; | |
| string usernamemixed = adfsUrl + "/13/usernamemixed"; | |
| StringBuilder xml = new StringBuilder(); | |
| xml.Append("<s:Envelope xmlns:s=\"http://www.w3.org/2003/05/soap-envelope\" xmlns:a=\"http://www.w3.org/2005/08/addressing\">"); | |
| xml.Append("<s:Header>"); | |
| xml.Append("<a:Action s:mustUnderstand=\"1\">http://docs.oasis-open.org/ws-sx/ws-trust/200512/RST/Issue</a:Action>"); | |
| xml.Append("<a:MessageID>urn:uuid:" + Guid.NewGuid() + "</a:MessageID>"); | |
| xml.Append("<a:ReplyTo>"); | |
| xml.Append("<a:Address>http://www.w3.org/2005/08/addressing/anonymous</a:Address>"); | |
| xml.Append("</a:ReplyTo>"); | |
| xml.Append("<Security s:mustUnderstand=\"1\" xmlns:u=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-utility-1.0.xsd\" xmlns=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-secext-1.0.xsd\">"); | |
| xml.Append("<u:Timestamp u:Id=\"" + Guid.NewGuid() + "\">"); | |
| xml.Append("<u:Created>" + now.ToUniversalTime().ToString("o") + "</u:Created>"); | |
| xml.Append("<u:Expires>" + now.AddMinutes(60).ToUniversalTime().ToString("o") + "</u:Expires>"); | |
| xml.Append("</u:Timestamp>"); | |
| xml.Append("<UsernameToken u:Id=\"" + Guid.NewGuid() + "\">"); | |
| xml.Append("<Username>" + username + "</Username>"); | |
| xml.Append("<Password Type=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-username-token-profile-1.0#PasswordText\">" + password + "</Password>"); | |
| xml.Append("</UsernameToken>"); | |
| xml.Append("</Security>"); | |
| xml.Append("<a:To s:mustUnderstand=\"1\">" + usernamemixed + "</a:To>"); | |
| xml.Append("</s:Header>"); | |
| xml.Append("<s:Body>"); | |
| xml.Append("<trust:RequestSecurityToken xmlns:trust=\"http://docs.oasis-open.org/ws-sx/ws-trust/200512\">"); | |
| xml.Append("<wsp:AppliesTo xmlns:wsp=\"http://schemas.xmlsoap.org/ws/2004/09/policy\">"); | |
| xml.Append("<a:EndpointReference>"); | |
| xml.Append("<a:Address>" + urnAddress + "</a:Address>"); | |
| xml.Append("</a:EndpointReference>"); | |
| xml.Append("</wsp:AppliesTo>"); | |
| xml.Append("<trust:RequestType>http://docs.oasis-open.org/ws-sx/ws-trust/200512/Issue</trust:RequestType>"); | |
| xml.Append("</trust:RequestSecurityToken>"); | |
| xml.Append("</s:Body>"); | |
| xml.Append("</s:Envelope>"); | |
| HttpWebRequest request = (HttpWebRequest)WebRequest.Create(usernamemixed); | |
| ASCIIEncoding encoding = new ASCIIEncoding(); | |
| byte[] bytesToWrite = encoding.GetBytes(xml.ToString()); | |
| request.Method = "POST"; | |
| request.ContentLength = bytesToWrite.Length; | |
| request.ContentType = "application/soap+xml; charset=UTF-8"; | |
| Stream newStream = request.GetRequestStream(); | |
| newStream.Write(bytesToWrite, 0, bytesToWrite.Length); | |
| newStream.Close(); | |
| HttpWebResponse response = (HttpWebResponse)request.GetResponse(); | |
| Stream dataStream = response.GetResponseStream(); | |
| if (dataStream == null) | |
| return null; | |
| StreamReader reader = new StreamReader(dataStream); | |
| XmlDocument x = new XmlDocument(); | |
| x.Load(reader); | |
| XmlNodeList cipherValue1 = x.GetElementsByTagName("e:CipherValue"); | |
| string token1 = cipherValue1[0].InnerText; | |
| XmlNodeList cipherValue2 = x.GetElementsByTagName("xenc:CipherValue"); | |
| string token2 = cipherValue2[0].InnerText; | |
| XmlNodeList keyIdentiferElements = x.GetElementsByTagName("o:KeyIdentifier"); | |
| string keyIdentifer = keyIdentiferElements[0].InnerText; | |
| XmlNodeList x509IssuerNameElements = x.GetElementsByTagName("X509IssuerName"); | |
| string x509IssuerName = x509IssuerNameElements[0].InnerText; | |
| XmlNodeList x509SerialNumberElements = x.GetElementsByTagName("X509SerialNumber"); | |
| string x509SerialNumber = x509SerialNumberElements[0].InnerText; | |
| XmlNodeList binarySecretElements = x.GetElementsByTagName("trust:BinarySecret"); | |
| string binarySecret = binarySecretElements[0].InnerText; | |
| string created = now.AddMinutes(-1).ToUniversalTime().ToString("o"); | |
| string expires = now.AddMinutes(60).ToUniversalTime().ToString("o"); | |
| string timestamp = "<u:Timestamp xmlns:u=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-utility-1.0.xsd\" u:Id=\"_0\"><u:Created>" + created + "</u:Created><u:Expires>" + expires + "</u:Expires></u:Timestamp>"; | |
| SHA1CryptoServiceProvider sha1Hasher = new SHA1CryptoServiceProvider(); | |
| byte[] hashedDataBytes = sha1Hasher.ComputeHash(Encoding.UTF8.GetBytes(timestamp)); | |
| string digestValue = Convert.ToBase64String(hashedDataBytes); | |
| string signedInfo = "<SignedInfo xmlns=\"http://www.w3.org/2000/09/xmldsig#\"><CanonicalizationMethod Algorithm=\"http://www.w3.org/2001/10/xml-exc-c14n#\"></CanonicalizationMethod><SignatureMethod Algorithm=\"http://www.w3.org/2000/09/xmldsig#hmac-sha1\"></SignatureMethod><Reference URI=\"#_0\"><Transforms><Transform Algorithm=\"http://www.w3.org/2001/10/xml-exc-c14n#\"></Transform></Transforms><DigestMethod Algorithm=\"http://www.w3.org/2000/09/xmldsig#sha1\"></DigestMethod><DigestValue>" + digestValue + "</DigestValue></Reference></SignedInfo>"; | |
| byte[] signedInfoBytes = Encoding.UTF8.GetBytes(signedInfo); | |
| HMACSHA1 hmac = new HMACSHA1(); | |
| byte[] binarySecretBytes = Convert.FromBase64String(binarySecret); | |
| hmac.Key = binarySecretBytes; | |
| byte[] hmacHash = hmac.ComputeHash(signedInfoBytes); | |
| string signatureValue = Convert.ToBase64String(hmacHash); | |
| XmlNodeList tokenExpiresElements = x.GetElementsByTagName("wsu:Expires"); | |
| CrmAuthenticationHeader authHeader = new CrmAuthenticationHeader | |
| { | |
| Expires = | |
| DateTime.ParseExact(tokenExpiresElements[0].InnerText, "yyyy-MM-ddTHH:mm:ss.fffK", null) | |
| .ToUniversalTime(), | |
| Header = CreateSoapHeaderOnPremise(url, keyIdentifer, token1, token2, x509IssuerName, | |
| x509SerialNumber, signatureValue, digestValue, created, expires) | |
| }; | |
| return authHeader; | |
| } | |
| /// <summary> | |
| /// Gets a CRM On Premise (IFD) SOAP header. | |
| /// </summary> | |
| /// <param name="url">The CRM On Premise URL ("https://org.domain.com/").</param> | |
| /// <param name="keyIdentifer">The KeyIdentifier from the initial request.</param> | |
| /// <param name="token1">The first token from the initial request.</param> | |
| /// <param name="token2">The second token from the initial request.</param> | |
| /// <param name="issuerNameX509">The certificate issuer.</param> | |
| /// <param name="serialNumberX509">The certificate serial number.</param> | |
| /// <param name="signatureValue">The hashsed value of the header signature.</param> | |
| /// <param name="digestValue">The hashed value of the header timestamp.</param> | |
| /// <param name="created">The header created date/time.</param> | |
| /// <param name="expires">The header expiration date/tim.</param> | |
| /// <returns>SOAP Header XML.</returns> | |
| private static string CreateSoapHeaderOnPremise(string url, string keyIdentifer, string token1, string token2, string issuerNameX509, string serialNumberX509, string signatureValue, string digestValue, string created, string expires) | |
| { | |
| StringBuilder xml = new StringBuilder(); | |
| xml.Append("<s:Header>"); | |
| xml.Append("<a:Action s:mustUnderstand=\"1\">http://schemas.microsoft.com/xrm/2011/Contracts/Services/IOrganizationService/Execute</a:Action>"); | |
| xml.Append("<a:MessageID>urn:uuid:" + Guid.NewGuid() + "</a:MessageID>"); | |
| xml.Append("<a:ReplyTo>"); | |
| xml.Append("<a:Address>http://www.w3.org/2005/08/addressing/anonymous</a:Address>"); | |
| xml.Append("</a:ReplyTo>"); | |
| xml.Append("<a:To s:mustUnderstand=\"1\">" + url + "XRMServices/2011/Organization.svc</a:To>"); | |
| xml.Append("<o:Security xmlns:o=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-secext-1.0.xsd\">"); | |
| xml.Append("<u:Timestamp xmlns:u=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-utility-1.0.xsd\" u:Id=\"_0\">"); | |
| xml.Append("<u:Created>" + created + "</u:Created>"); | |
| xml.Append("<u:Expires>" + expires + "</u:Expires>"); | |
| xml.Append("</u:Timestamp>"); | |
| xml.Append("<xenc:EncryptedData Type=\"http://www.w3.org/2001/04/xmlenc#Element\" xmlns:xenc=\"http://www.w3.org/2001/04/xmlenc#\">"); | |
| xml.Append("<xenc:EncryptionMethod Algorithm=\"http://www.w3.org/2001/04/xmlenc#aes256-cbc\"/>"); | |
| xml.Append("<KeyInfo xmlns=\"http://www.w3.org/2000/09/xmldsig#\">"); | |
| xml.Append("<e:EncryptedKey xmlns:e=\"http://www.w3.org/2001/04/xmlenc#\">"); | |
| xml.Append("<e:EncryptionMethod Algorithm=\"http://www.w3.org/2001/04/xmlenc#rsa-oaep-mgf1p\">"); | |
| xml.Append("<DigestMethod Algorithm=\"http://www.w3.org/2000/09/xmldsig#sha1\"/>"); | |
| xml.Append("</e:EncryptionMethod>"); | |
| xml.Append("<KeyInfo>"); | |
| xml.Append("<o:SecurityTokenReference xmlns:o=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-secext-1.0.xsd\">"); | |
| xml.Append("<X509Data>"); | |
| xml.Append("<X509IssuerSerial>"); | |
| xml.Append("<X509IssuerName>" + issuerNameX509 + "</X509IssuerName>"); | |
| xml.Append("<X509SerialNumber>" + serialNumberX509 + "</X509SerialNumber>"); | |
| xml.Append("</X509IssuerSerial>"); | |
| xml.Append("</X509Data>"); | |
| xml.Append("</o:SecurityTokenReference>"); | |
| xml.Append("</KeyInfo>"); | |
| xml.Append("<e:CipherData>"); | |
| xml.Append("<e:CipherValue>" + token1 + "</e:CipherValue>"); | |
| xml.Append("</e:CipherData>"); | |
| xml.Append("</e:EncryptedKey>"); | |
| xml.Append("</KeyInfo>"); | |
| xml.Append("<xenc:CipherData>"); | |
| xml.Append("<xenc:CipherValue>" + token2 + "</xenc:CipherValue>"); | |
| xml.Append("</xenc:CipherData>"); | |
| xml.Append("</xenc:EncryptedData>"); | |
| xml.Append("<Signature xmlns=\"http://www.w3.org/2000/09/xmldsig#\">"); | |
| xml.Append("<SignedInfo>"); | |
| xml.Append("<CanonicalizationMethod Algorithm=\"http://www.w3.org/2001/10/xml-exc-c14n#\"/>"); | |
| xml.Append("<SignatureMethod Algorithm=\"http://www.w3.org/2000/09/xmldsig#hmac-sha1\"/>"); | |
| xml.Append("<Reference URI=\"#_0\">"); | |
| xml.Append("<Transforms>"); | |
| xml.Append("<Transform Algorithm=\"http://www.w3.org/2001/10/xml-exc-c14n#\"/>"); | |
| xml.Append("</Transforms>"); | |
| xml.Append("<DigestMethod Algorithm=\"http://www.w3.org/2000/09/xmldsig#sha1\"/>"); | |
| xml.Append("<DigestValue>" + digestValue + "</DigestValue>"); | |
| xml.Append("</Reference>"); | |
| xml.Append("</SignedInfo>"); | |
| xml.Append("<SignatureValue>" + signatureValue + "</SignatureValue>"); | |
| xml.Append("<KeyInfo>"); | |
| xml.Append("<o:SecurityTokenReference xmlns:o=\"http://docs.oasis-open.org/wss/2004/01/oasis-200401-wss-wssecurity-secext-1.0.xsd\">"); | |
| xml.Append("<o:KeyIdentifier ValueType=\"http://docs.oasis-open.org/wss/oasis-wss-saml-token-profile-1.0#SAMLAssertionID\">" + keyIdentifer + "</o:KeyIdentifier>"); | |
| xml.Append("</o:SecurityTokenReference>"); | |
| xml.Append("</KeyInfo>"); | |
| xml.Append("</Signature>"); | |
| xml.Append("</o:Security>"); | |
| xml.Append("</s:Header>"); | |
| return xml.ToString(); | |
| } | |
| /// <summary> | |
| /// Gets the name of the ADFS server CRM uses for authentication. | |
| /// </summary> | |
| /// <param name="url">The Url of the CRM On Premise (IFD) organization (https://org.domain.com).</param> | |
| /// <returns>The AD FS server url.</returns> | |
| private static string GetAdfs(string url) | |
| { | |
| HttpWebRequest request = (HttpWebRequest)WebRequest.Create(url + "/XrmServices/2011/Organization.svc?wsdl=wsdl0"); | |
| request.Method = "GET"; | |
| HttpWebResponse response = (HttpWebResponse)request.GetResponse(); | |
| Stream dataStream = response.GetResponseStream(); | |
| if (dataStream == null) | |
| return null; | |
| StreamReader reader = new StreamReader(dataStream); | |
| XmlDocument x = new XmlDocument(); | |
| x.Load(reader); | |
| XmlNodeList nodes = x.GetElementsByTagName("ms-xrm:Identifier"); | |
| foreach (XmlNode node in nodes) | |
| { | |
| return node.FirstChild.InnerText.Replace("http://", "https://"); | |
| } | |
| return null; | |
| } | |
| } | |
| } |
SOAP Only Authentication Using C#的更多相关文章
- (转)Java实现Web Service过程中处理SOAP Header的问题
网上有篇文章,大致这么说的(如下文),最后我采用的wsimport -XadditionalHeaders的方式. StrikeIron offers two authentication meth ...
- authentication与网站安全验证
1.Forms 身份验证提供程序 通过 Forms 身份验证,可以使用所创建的登录窗体验证用户的用户名和密码.未经过身份验证的请求被重定向到登录页,用户在该页上提供凭据和提交窗体.如果应用程序对请求进 ...
- [转]Web Service Authentication
本文转自:http://www.codeproject.com/Articles/9348/Web-Service-Authentication Download source files - 45. ...
- wsse:InvalidSecurity Error When Testing FND_PROFILE Web Service in Oracle Applications R 12.1.2 from SOAP UI (Doc ID 1314946.1)
wsse:InvalidSecurity Error When Testing FND_PROFILE Web Service in Oracle Applications R 12.1.2 from ...
- 网络负载均衡环境下wsHttpBinding+Message Security+Windows Authentication的常见异常
提高Windows Communication Foundation (WCF) 应用程序负载能力的方法之一就是通过把它们部署到负载均衡的服务器场中. 其中可以使用标准的负载均衡技术, Windows ...
- Nginx集群之WCF分布式身份验证(支持Soap)
目录 1 大概思路... 1 2 Nginx集群之WCF分布式身份验证... 1 3 BasicHttpBinding.ws2007HttpBinding. 2 4 ...
- 一个HTTP Basic Authentication引发的异常
这几天在做一个功能,其实很简单.就是调用几个外部的API,返回数据后进行组装然后成为新的接口.其中一个API是一个很奇葩的API,虽然是基于HTTP的,但既没有基于SOAP规范,也不是Restful风 ...
- C#,SOAP1.1与1.2的发布与禁用(SOAP 1.2 in .NET Framework 2.0)
来源:https://www.codeproject.com/Articles/11878/SOAP-in-NET-Framework SOAP 1.2 in .NET Framework 2.0 ...
- Error in WCF client consuming Axis 2 web service with WS-Security UsernameToken PasswordDigest authentication scheme
13down votefavorite 6 I have a WCF client connecting to a Java based Axis2 web service (outside my c ...
随机推荐
- Toast问题记录:This Toast was not created with Toast.makeText()
最近使用自己封装的Toast时,遇到一个问题 java.lang.RuntimeException: This Toast was not created with Toast.makeText() ...
- cmd 命令提示符常用操作
切换盘符: d: 进入子目录: cd web 返回上级目录: cd .. 查询子目录下所有文件:dir
- debian6之eclipse和jdk安装
安装JDK 目前最新的JDK版本是:Java SE Development Kit 7u5 下载地址:http://www.oracle.com/technetwork/java/javase/dow ...
- Go -- LRU算法(缓存淘汰算法)(转)
1. LRU1.1. 原理 LRU(Least recently used,最近最少使用)算法根据数据的历史访问记录来进行淘汰数据,其核心思想是“如果数据最近被访问过,那么将来被访问的几率也更高”. ...
- 表现层 JSP 页面实现
一.实验介绍 1.1 实验内容 本节课程主要利用 easyUI 实现系统的前端页面. 1.2 实验知识点 easyUI JavaScript html 1.3 实验环境 JDK1.8 Eclipse ...
- [C++设计模式] proxy 代理模式
代理模式:为其它对象提供一种代理以控制对这个对象的訪问. Proxy: 保存一个引用使得代理能够訪问实体.若RealSubject和Subject的接口同样,Proxy会引用Subject,就相当于在 ...
- 【KMP】hdu1867(A + B for you again) 杭电java a题真坑
点击打开链接 Problem Description Generally speaking, there are a lot of problems about strings processing. ...
- sparkSQL1.1入门之十:总结
回想一下,在前面几章中,就sparkSQL1.1.0基本概念.执行架构.基本操作和有用工具做了基本介绍. 基本概念: SchemaRDD Rule Tree LogicPlan Parser Anal ...
- css hack(部分)
一.去掉图片间隙:hack1.img{ display:block: }hack2.将<div></div>与<img>写在同一行 二.ie6双倍浮向(双倍边距)出 ...
- 笔记03 wpf 在MVVM模式下怎样在Viewmodel里面获得view的控件对象
转自http://blog.csdn.net/qing2005/article/details/6601199http://blog.csdn.net/qing2005/article/detail ...