
Python Ethical Hacking - VULNERABILITY SCANNER(7)
VULNERABILITY_SCANNER
How to discover a vulnerability in a web application?
1. Go into every possible page.
2. Look for ways to send data to the web application(URL + Forms).
3. Send payloads to discover vulnerabilities.
4. Analyze the response to check of the website is vulnerable.
->General steps are the same regardless of the vulnerability.
Login the metasploitable VM and modify the security of DVWA from high to medium.(dvwaPage.inc.php in /var/www/dvwa/dvwa/includes)

Submit the following script on the Reflected Cross Site Scripting(XSS)
<sCript>alert('test')</scriPt>
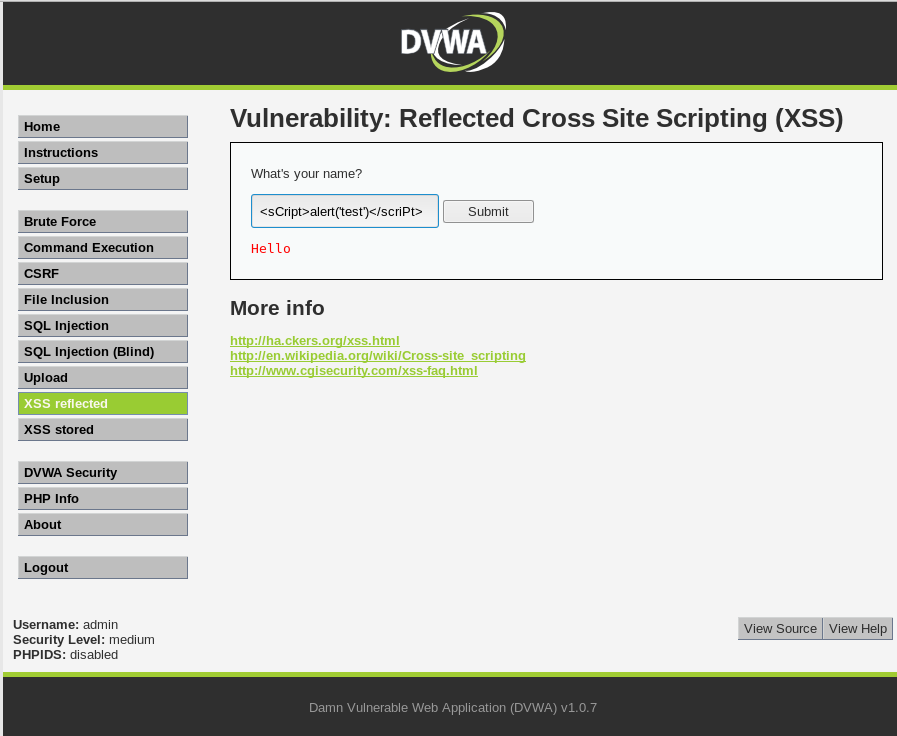
You can find the script in the source code.
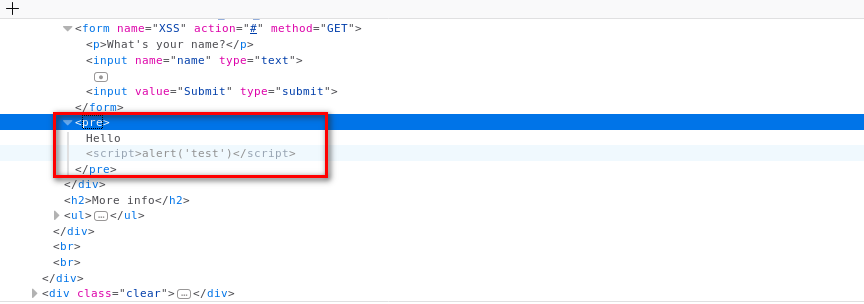
Add the new feature - test_xss_in_form in Scanner class.
#!/usr/bin/env python

import requests

import re

from bs4 import BeautifulSoup

from urllib.parse import urljoin

class Scanner:

    def __init__(self, url, ignore_links):

        self.session = requests.Session()

        self.target_url = url

        self.target_links = []

        self.links_to_ignore = ignore_links

    def extract_links_from(self, url):

        response = self.session.get(url)

        return re.findall('(?:href=")(.*?)"', response.content.decode(errors='ignore'))

    def crawl(self, url=None):

        if url == None:

            url = self.target_url

        href_links = self.extract_links_from(url)

        for link in href_links:

            link = urljoin(url, link)

            if "#" in link:

                link = link.split("#")[0]

            if self.target_url in link and link not in self.target_links and link not in self.links_to_ignore:

                self.target_links.append(link)

                print(link)

                self.crawl(link)

    def extract_forms(self, url):

        response = self.session.get(url)

        parsed_html = BeautifulSoup(response.content.decode(), features="lxml")

        return parsed_html.findAll("form")

    def submit_form(self, form, value, url):

        action = form.get("action")

        post_url = urljoin(url, action)

        method = form.get("method")

        inputs_list = form.findAll("input")

        post_data = {}

        for input in inputs_list:

            input_name = input.get("name")

            input_type = input.get("type")

            input_value = input.get("value")

            if input_type == "text":

                input_value = value

            post_data[input_name] = input_value

        if method == "post":

            return requests.post(post_url, data=post_data)

        return self.session.get(post_url, params=post_data)

    def run_scanner(self):

        for link in self.target_links:

            forms = self.extract_forms(link)

            for form in forms:

                print("[+] Testing form in " + link)

            if "=" in link:

                print("[+] Testing " + link)

    def test_xss_in_form(self, form, url):

        xss_test_script = "<sCript>alert('test')</scriPt>"

        response = self.submit_form(form, xss_test_script, url)

        if xss_test_script in response.content.decode():

            return True
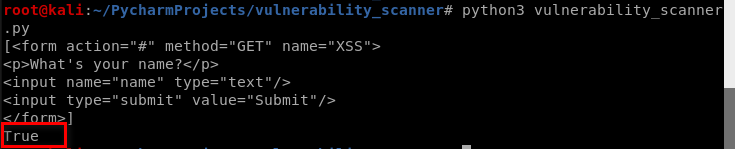
Modify the vulnerability scanner code and test it.
#!/usr/bin/env python

import scanner

target_url = "http://10.0.0.45/dvwa/"

links_to_ignore = "http://10.0.0.45/dvwa/logout.php"

data_dict = {"username": "admin", "password": "password", "Login": "submit"}

vuln_scanner = scanner.Scanner(target_url, links_to_ignore)

vuln_scanner.session.post("http://10.0.0.45/dvwa/login.php", data=data_dict)

# vuln_scanner.crawl()

forms = vuln_scanner.extract_forms("http://10.0.0.45/dvwa/vulnerabilities/xss_r/")

print(forms)

response = vuln_scanner.test_xss_in_form(forms[0], "http://10.0.0.45/dvwa/vulnerabilities/xss_r/")

print(response)
Aha! We find customized vulnerability.
Python Ethical Hacking - VULNERABILITY SCANNER(7)的更多相关文章
- Python Ethical Hacking - VULNERABILITY SCANNER(9)
Automatically Discovering Vulnerabilities Using the Vulnerability Scanner 1. Modify the run_scanner ...
- Python Ethical Hacking - VULNERABILITY SCANNER(4)
Extracting & Submitting Forms Automatically Target website:http://10.0.0.45/dvwa/vulnerabilities ...
- Python Ethical Hacking - VULNERABILITY SCANNER(2)
VULNERABILITY_SCANNER How to discover a vulnerability in a web application? 1. Go into every possibl ...
- Python Ethical Hacking - VULNERABILITY SCANNER(8)
Implementing Code To Discover XSS in Parameters 1. Watch the URL of the XSS reflected page carefully ...
- Python Ethical Hacking - VULNERABILITY SCANNER(3)
Polish the Python code using sending requests in a session Class Scanner. #!/usr/bin/env python impo ...
- Python Ethical Hacking - VULNERABILITY SCANNER(1)
HTTP REQUESTS BASIC INFORMATION FLOW The user clicks on a link. HTML website generates a request(cli ...
- Python Ethical Hacking - VULNERABILITY SCANNER(6)
EXPLOITATION - XSS VULNS EXPLOITING XSS Run any javascript code. Beef framework can be used to hook ...
- Python Ethical Hacking - VULNERABILITY SCANNER(5)
EXPLOITATION - XSS VULNS XSS - CROSS SITE SCRIPTING VULNS Allow an attacker to inject javascript cod ...
- Python Ethical Hacking - BACKDOORS(8)
Cross-platform hacking All programs we wrote are pure python programs They do not rely on OS-specifi ...
随机推荐
- C++ 进阶 模板和STL
C++提高编程 本阶段主要针对C++泛型编程和STL技术做详细讲解,探讨C++更深层的使用 1 模板 1.1 模板的概念 模板就是建立通用的模具,大大提高复用性 模板的特点: 模板不可以直接使用,它只 ...
- debug PostgreSQL 9.6.18 using Eclipse IDE on CentOS7
目录 debug PostgreSQL 9.6.18 using Eclipse IDE on CentOS7 1.概览 2.建立用户 3.编译postgre 4.启动Eclipse 5.设置环境变量 ...
- JAVA设计模式 2【创建型】原型模式的理解与使用
在本节中,我们将学习和使用原型模式:这一节学习的原型模式也是创建型 模式的其中之一.再次复习一下:创建型 模式就是描述如何去更好的创建一个对象. 我们都知道,在JAVA 语言中.使用new 关键字创建 ...
- opencv C++矩阵操作
int main(){ cv::Mat src1=(cv::Mat_<float>(2,3)<<1,2,3,4,5,6); cv::Mat src2=(cv::Mat_< ...
- 警告Establishing SSL connection without server's identity verification is not recommended
[本文版权归微信公众号"代码艺术"(ID:onblog)所有,若是转载请务必保留本段原创声明,违者必究.若是文章有不足之处,欢迎关注微信公众号私信与我进行交流!] SpringBo ...
- 03.基于测试开发讲解和Cobertura框架介绍
首先我们先 CREATE TABLE `t_user` ( `id` int(11) NOT NULL AUTO_INCREMENT, `username` varchar(200) DEFAULT ...
- CSS定位(Positioning)
CSS 定位和浮动 CSS 为定位和浮动提供了一些属性,利用这些属性,可以建立列式布局,将布局的一部分与另一部分重叠,还可以完成多年来通常需要使用多个表格才能完成的任务. 一切皆为框 div.h1 或 ...
- Redis 的基本数据类型 和 基础应用场景
Redis 的基础应用场景 获取中奖用户ID,随机弹出之后集合中就不存在了[set] 存储活动中中奖的用户ID,保证同一个用户不会中奖两次[set] 存储粉丝列表,value 为粉丝的用户ID,sco ...
- 栈的顺序存储和链式存储c语言实现
一. 栈 栈的定义:栈是只允许在一端进行插入或删除操作的线性表. 1.栈的顺序存储 栈顶指针:S.top,初始设为-1 栈顶元素:S.data[S.top] 进栈操作:栈不满时,栈顶指针先加1,再到栈 ...
- SQL注入原理及代码分析(一)
前言 我们都知道,学安全,懂SQL注入是重中之重,因为即使是现在SQL注入漏洞依然存在,只是相对于之前现在挖SQL注入变的困难了.而且知识点比较多,所以在这里总结一下.通过构造有缺陷的代码,来理解常见 ...