
Python Ethical Hacking - VULNERABILITY SCANNER(8)
Implementing Code To Discover XSS in Parameters
1. Watch the URL of the XSS reflected page carefully.
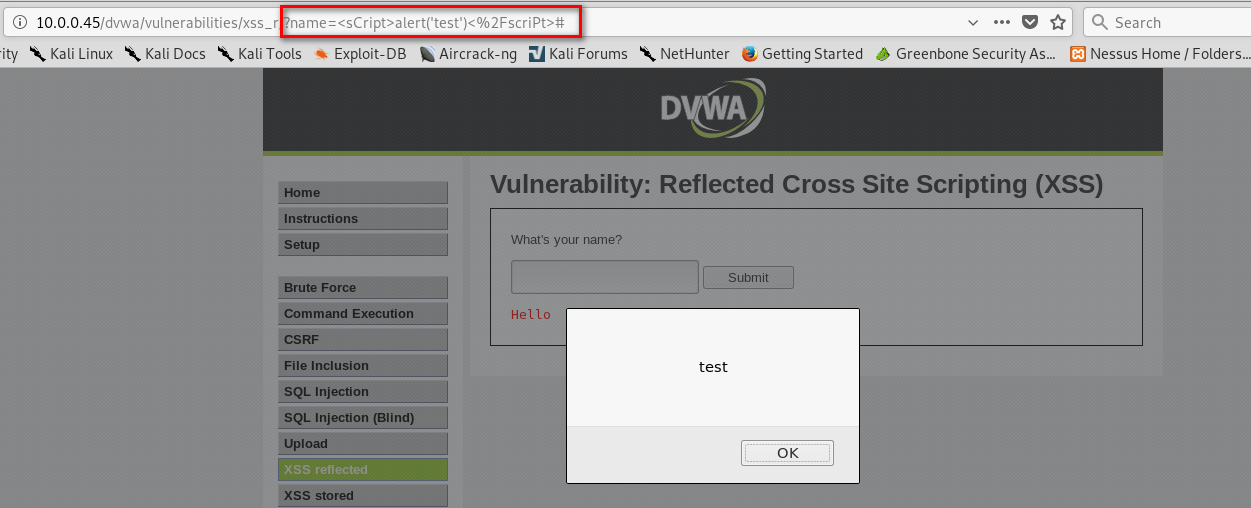
2. Add the test_xss_in_link method in the Scanner class.
#!/usr/bin/env python

import requests

import re

from bs4 import BeautifulSoup

from urllib.parse import urljoin

class Scanner:

    def __init__(self, url, ignore_links):

        self.session = requests.Session()

        self.target_url = url

        self.target_links = []

        self.links_to_ignore = ignore_links

    def extract_links_from(self, url):

        response = self.session.get(url)

        return re.findall('(?:href=")(.*?)"', response.content.decode(errors='ignore'))

    def crawl(self, url=None):

        if url == None:

            url = self.target_url

        href_links = self.extract_links_from(url)

        for link in href_links:

            link = urljoin(url, link)

            if "#" in link:

                link = link.split("#")[0]

            if self.target_url in link and link not in self.target_links and link not in self.links_to_ignore:

                self.target_links.append(link)

                print(link)

                self.crawl(link)

    def extract_forms(self, url):

        response = self.session.get(url)

        parsed_html = BeautifulSoup(response.content.decode(), features="lxml")

        return parsed_html.findAll("form")

    def submit_form(self, form, value, url):

        action = form.get("action")

        post_url = urljoin(url, action)

        method = form.get("method")

        inputs_list = form.findAll("input")

        post_data = {}

        for input in inputs_list:

            input_name = input.get("name")

            input_type = input.get("type")

            input_value = input.get("value")

            if input_type == "text":

                input_value = value

            post_data[input_name] = input_value

        if method == "post":

            return requests.post(post_url, data=post_data)

        return self.session.get(post_url, params=post_data)

    def run_scanner(self):

        for link in self.target_links:

            forms = self.extract_forms(link)

            for form in forms:

                print("[+] Testing form in " + link)

            if "=" in link:

                print("[+] Testing " + link)

    def test_xss_in_link(self, url):

        xss_test_script = "<sCript>alert('test')</scriPt>"

        url = url.replace("=", "=" + xss_test_script)

        response = self.session.get(url)

        return xss_test_script in response.content.decode()

    def test_xss_in_form(self, form, url):

        xss_test_script = "<sCript>alert('test')</scriPt>"

        response = self.submit_form(form, xss_test_script, url)

        return xss_test_script in response.content.decode()
3. Test this scanner.
#!/usr/bin/env python

import scanner

target_url = "http://10.0.0.45/dvwa/"

links_to_ignore = "http://10.0.0.45/dvwa/logout.php"

data_dict = {"username": "admin", "password": "password", "Login": "submit"}

vuln_scanner = scanner.Scanner(target_url, links_to_ignore)

vuln_scanner.session.post("http://10.0.0.45/dvwa/login.php", data=data_dict)

# vuln_scanner.crawl()

forms = vuln_scanner.extract_forms("http://10.0.0.45/dvwa/vulnerabilities/xss_r/")

print(forms)

response = vuln_scanner.test_xss_in_link("http://10.0.0.45/dvwa/vulnerabilities/xss_r/?name=test")

print(response)
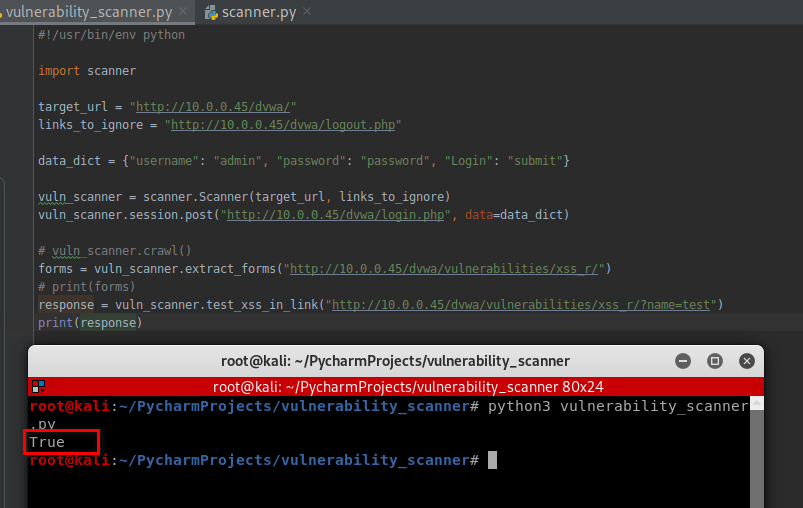
Test the web page - http://10.0.0.45/dvwa/vulnerabilities/xss_r/?name=test:
vuln_scanner.test_xss_in_link("http://10.0.0.45/dvwa/vulnerabilities/xss_r/?name=test")
It is vulnerable on XSS.
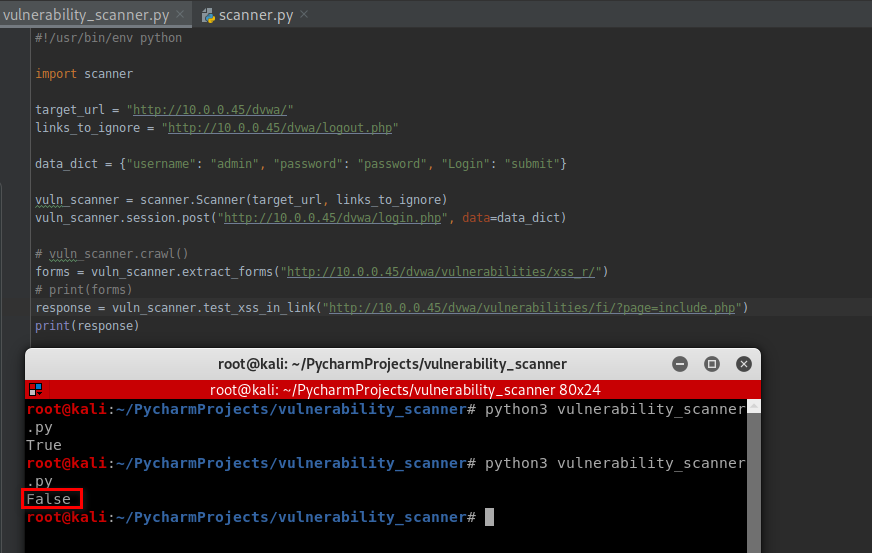
Test the web page - http://10.0.0.45/dvwa/vulnerabilities/fi/?page=include.php:
vuln_scanner.test_xss_in_link("http://10.0.0.45/dvwa/vulnerabilities/fi/?page=include.php")
It is not vulnerable on XSS.
Python Ethical Hacking - VULNERABILITY SCANNER(8)的更多相关文章
- Python Ethical Hacking - VULNERABILITY SCANNER(9)
Automatically Discovering Vulnerabilities Using the Vulnerability Scanner 1. Modify the run_scanner ...
- Python Ethical Hacking - VULNERABILITY SCANNER(7)
VULNERABILITY_SCANNER How to discover a vulnerability in a web application? 1. Go into every possibl ...
- Python Ethical Hacking - VULNERABILITY SCANNER(4)
Extracting & Submitting Forms Automatically Target website:http://10.0.0.45/dvwa/vulnerabilities ...
- Python Ethical Hacking - VULNERABILITY SCANNER(2)
VULNERABILITY_SCANNER How to discover a vulnerability in a web application? 1. Go into every possibl ...
- Python Ethical Hacking - VULNERABILITY SCANNER(3)
Polish the Python code using sending requests in a session Class Scanner. #!/usr/bin/env python impo ...
- Python Ethical Hacking - VULNERABILITY SCANNER(1)
HTTP REQUESTS BASIC INFORMATION FLOW The user clicks on a link. HTML website generates a request(cli ...
- Python Ethical Hacking - VULNERABILITY SCANNER(6)
EXPLOITATION - XSS VULNS EXPLOITING XSS Run any javascript code. Beef framework can be used to hook ...
- Python Ethical Hacking - VULNERABILITY SCANNER(5)
EXPLOITATION - XSS VULNS XSS - CROSS SITE SCRIPTING VULNS Allow an attacker to inject javascript cod ...
- Python Ethical Hacking - BACKDOORS(8)
Cross-platform hacking All programs we wrote are pure python programs They do not rely on OS-specifi ...
随机推荐
- MFC时间简单比较方法
MFC//时间简单比较方法 void CMFCsaveListTofileDlg::OnBnClickedButton6()//时间简单比较方法 { // TODO: 在此添加控件通知处理程序代码 C ...
- ThinkPHP5使用阿里云OSS图片上传
1.下载OSS文件放在网站根目录下(OSS文件下载地址:https://gitee.com/jth1234/oss_files.git) 2.在入口文件中加载OSS 3.config文件配置oss信息 ...
- CSS定位(Positioning)
CSS 定位和浮动 CSS 为定位和浮动提供了一些属性,利用这些属性,可以建立列式布局,将布局的一部分与另一部分重叠,还可以完成多年来通常需要使用多个表格才能完成的任务. 一切皆为框 div.h1 或 ...
- 1166 - Unknown error 1166[mysql 错误
错误码 1166 原因 字段名因为是复制过来的, 末尾存在了一个空格换行
- Hexo快速构建个人小站-Fulid主题下添加Valine评论系统(三)
Hexo目录: Hexo快速构建个人小站-Hexo初始化和将项目托管在Github(一) Hexo快速构建个人小站-自定义域名和自定义主题(二) 背景交代: 前面两章完成了Hexo的初始化和部分自定义 ...
- Oracle 11gR2 待定的统计信息(Pending Statistic)
Oracle 11gR2 待定的统计信息(Pending Statistic) 官档最权威: 发布优化器统计信息的用户界面 管理已发布和待处理的统计信息 实验先拖着.
- web图片前端裁剪功能实现_利用html5 canvas技术实现图片裁剪
用户上传头像然后截图的需求很常见,很多做法是把图像发送到后端,把裁剪后的结果发送给浏览器,这种方式会增加处理时延.最近正好学习了HTML5里的canvas,发现它的图片处理功能比较强大,就打算用can ...
- HTML5全局属性汇总
局部属性和全局属性 局部属性:有些元素能规定自己的属性,这种属性称为局部属性.比如link元素,它具有的局部属性有href. rel. hreflang. media. type. sizes这六个. ...
- elasticsearch 单节点搭建与爬坑记录
elasticsearch 单节点搭建与爬坑记录 prepare 虚拟机或者云服务器(这里用的是阿里云ECS) linux---centos7 安装完毕的jdk 相应的安装包(在https:/ ...
- 【线型DP】洛谷P2066 机器分配
[线型DP]洛谷P2066 机器分配 标签(空格分隔): 线型DP [题目] 题目描述 总公司拥有高效设备M台,准备分给下属的N个分公司.各分公司若获得这些设备,可以为国家提供一定的盈利.问:如何分配 ...