
Ethical Hacking - Web Penetration Testing(8)
SQL INJECTION
WHAT IS SQL?
- Most websites use a database to store data.
- Most data stored in it(usernames, passwords ..etc.)
- Web application reads, updates and inserts data in the database.
- Interaction with DB done using SQL.
WHY ARE THEY SO DANGEROUS
1. They are everywhere.
2. Give access to the database –> sensitive data.
3. Can be used to read local files outside www root.
4. Can be used to log in as admin and further exploit the system.
5. Can be used to upload files.
DISCOVERING SQLi in POST
- Try to break the page.
- Using ‘and’, ‘order by’ or “’”.
- Testing text boxes and URL parameters on the form.
http://target.com/page.php?something=something
Pre-Configure about Metasplitable2:

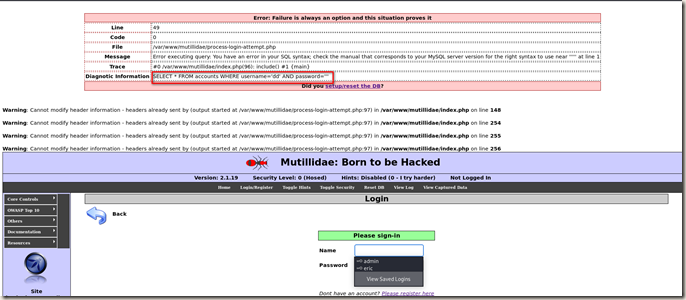
Following is a very useful error message.
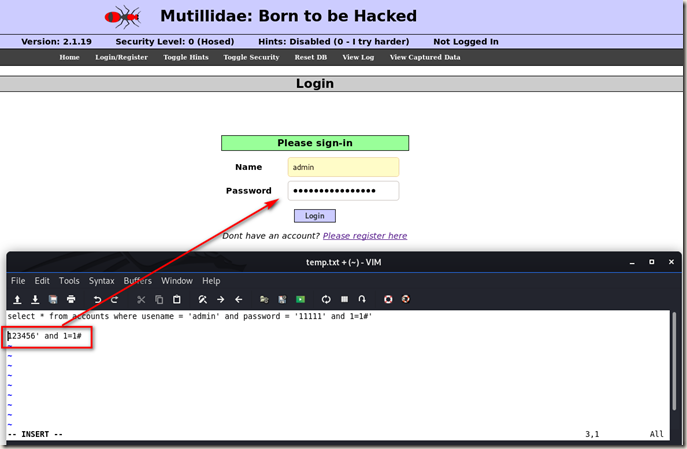
So let’s modify the input on password box. We can login with a wrong password now.
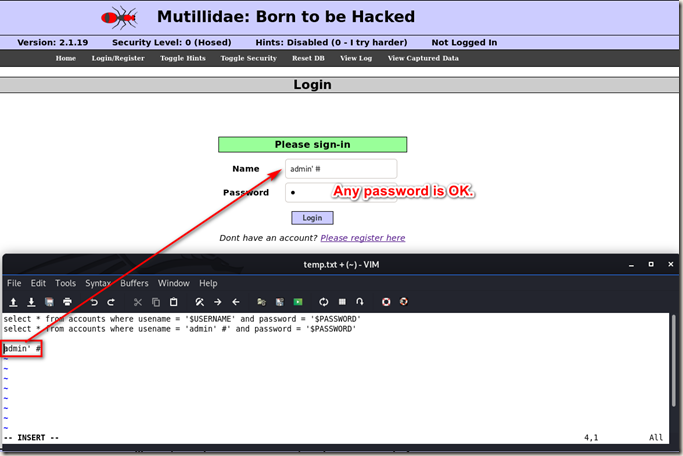
Bypassing Authentication.
Ethical Hacking - Web Penetration Testing(8)的更多相关文章
- Ethical Hacking - Web Penetration Testing(13)
OWASP ZAP(ZED ATTACK PROXY) Automatically find vulnerabilities in web applications. Free and easy to ...
- Ethical Hacking - Web Penetration Testing(10)
SQL INJECTION SQLMAP Tool designed to exploit SQL injections. Works with many DB types, MySQL, MSSQL ...
- Ethical Hacking - Web Penetration Testing(6)
REMOTE FILE INCLUSION Similar to local file inclusion. But allows an attacker to read ANY file from ...
- Ethical Hacking - Web Penetration Testing(1)
How to hack a website? An application installed on a computer. ->web application pen-testing A co ...
- Python Ethical Hacking - WEB PENETRATION TESTING(1)
WHAT IS A WEBSITE Computer with OS and some servers. Apache, MySQL ...etc. Cotains web application. ...
- Python Ethical Hacking - WEB PENETRATION TESTING(2)
CRAWING DIRECTORIES Directories/folders inside the web root. Can contain files or other directories ...
- Ethical Hacking - Web Penetration Testing(12)
XSS VULNS XSS - CROSS SITE SCRIPTING VULNS Allow an attacker to inject javascript code into the page ...
- Ethical Hacking - Web Penetration Testing(11)
SQL INJECTION Preventing SQLi Filters can be bypassed. Use a blacklist of commands? Still can be byp ...
- Ethical Hacking - Web Penetration Testing(9)
SQL INJECTION Discovering SQLi in GET Inject by browser URL. Selecting Data From Database Change the ...
随机推荐
- rust 九九乘法表
fn main(){ for i in 1..10 { for j in 1..i+1 { print!("{}*{}={:<2} ",j,i,i*j); } print!( ...
- cb07a_c++_迭代器和迭代器的范围
cb07a_c++_迭代器和迭代器的范围c++primer第4版https://www.cnblogs.com/txwtech/p/12309989.html--每一种容器都有自己的迭代器--所有的迭 ...
- Linux 之Mycat搭建报错 java.net.MalformedURLException: Local host name unknown: java.net.UnknownHostException
搭建MyCat环境时出现 错误: 代理抛出异常错误: java.net.MalformedURLException: Local host name unknown: java.net.Unknown ...
- Python的多继承问题-MRO和C3算法
大部分内容转载自C3 线性化算法与 MRO 理解Python中的多继承 Python 中的方法解析顺序(Method Resolution Order, MRO)定义了多继承存在时 Python 解释 ...
- 关于idea的一些快捷键
最近在用idea写代码,熟悉一些快捷键的使用能够让写代码的速度提高,以下快捷键是默认idea的快捷键,当然我们可以自己修改的: 自动补全代码快捷键:CTRL+alt+V 自动格式化代码:CTRL+al ...
- Digix2019华为算法精英挑战赛代码
Digix2019华为算法精英挑战赛代码 最终成绩: 决赛第九 问题 根据手机型号,颜色,用户偏好,手机APP等信息预测用户年龄. https://developer.huawei.com/consu ...
- 超简单集成HMS Scan Kit扫码SDK,轻松实现扫码购
前言 在前面的文章中,我们向大家介绍了HMS Scan Kit 的快速集成方法以及HMS Scan Kit和其他开源扫码工具的竞争力对比分析,如果没有看到也没关系,文章下方的往期链接中有文章入口. ...
- Python进阶之浅谈内置方法(补充)
目录 列表类型的内置方法 元组类型的内置方法 字典类型的内置方法 集合类型的内置方法 列表类型的内置方法 1.作用:描述名字,说的话等 2.定义方式 s=['tim','age'] s=str('ti ...
- STL标准函数库学习小总结
浅谈STL(未完)前言:(1)学习资料——<算法笔记>第六章.<常用基础数据结构>文档 (2)测试平台——Codeup新家(<算法笔记>对应OJ).洛谷.YCOJ ...
- GAN网络从入门教程(二)之GAN原理
在一篇博客GAN网络从入门教程(一)之GAN网络介绍中,简单的对GAN网络进行了一些介绍,介绍了其是什么,然后大概的流程是什么. 在这篇博客中,主要是介绍其数学公式,以及其算法流程.当然数学公式只是简 ...