
Python Ethical Hacking - WEB PENETRATION TESTING(1)
WHAT IS A WEBSITE
- Computer with OS and some servers.
- Apache, MySQL ...etc.
- Cotains web application.
- PHP, Python ...etc.
- Web application is executed here and not on the client's machine.
How to hack a website?
- An application installed on a computer.
- ->web application pentesting
- Computer uses an OS + other applications.
- ->server side attacks.
- Managed by humans.
- ->client side attacks.
INFORMATION GATHERING
- IP address.
- Domain name info.
- Technologies used.
- Other websites on the same server.
- DNS records.
- Files, sub-domains, directories.
CRAWLING SUBDOMAINS
- Domains before the actual domain name.
- Part of the main domain.
Ex:
- subdomain.target.com
- mail.google.com
- plus.google.com
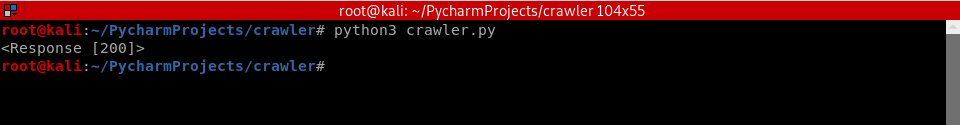
#!/usr/bin/env python

import requests

url = "baidu.com"

try:

    get_response = requests.get("http://" + url)

    print(get_response)

except requests.exceptions.ConnectionError:

    pass
Polished Python Code:
#!/usr/bin/env python

import requests

def request(url):

    try:

        return requests.get("http://" + url)

    except requests.exceptions.ConnectionError:

        pass

target_url = "baidu.com"

with open("subdomains.list", "r") as wordlist_file:

    for line in wordlist_file:

        word = line.strip()

        test_url = word + "." + target_url

        response = request(test_url)

        if response:

            print("[+] Discovered subdomain --> " + test_url)

Python Ethical Hacking - WEB PENETRATION TESTING(1)的更多相关文章
- Python Ethical Hacking - WEB PENETRATION TESTING(2)
CRAWING DIRECTORIES Directories/folders inside the web root. Can contain files or other directories ...
- Python Ethical Hacking - WEB PENETRATION TESTING(5)
Guessing Login Information on Login Pages Our target website: http://10.0.0.45/dvwa/login.php #!/usr ...
- Python Ethical Hacking - WEB PENETRATION TESTING(4)
CRAWING SPIDER Goal -> Recursively list all links starting from a base URL. 1. Read page HTML. 2. ...
- Python Ethical Hacking - WEB PENETRATION TESTING(3)
CRAWLING SUMMARY Our crawler so far can guess: Subdomains. Directories. Files. Advantages: ->Disc ...
- Ethical Hacking - Web Penetration Testing(13)
OWASP ZAP(ZED ATTACK PROXY) Automatically find vulnerabilities in web applications. Free and easy to ...
- Ethical Hacking - Web Penetration Testing(8)
SQL INJECTION WHAT IS SQL? Most websites use a database to store data. Most data stored in it(userna ...
- Ethical Hacking - Web Penetration Testing(10)
SQL INJECTION SQLMAP Tool designed to exploit SQL injections. Works with many DB types, MySQL, MSSQL ...
- Ethical Hacking - Web Penetration Testing(6)
REMOTE FILE INCLUSION Similar to local file inclusion. But allows an attacker to read ANY file from ...
- Ethical Hacking - Web Penetration Testing(4)
CODE EXECUTION VULNS Allows an attacker to execute OS commands. Windows or Linux commands. Can be us ...
随机推荐
- Happens-Before原则
Java内存模型是通过各种操作来定义的,包括对变量的读/写操作,监视器的加锁和释放操作,以及线程的启动和合并操作.JMM为程序中所有的操作定义了一个偏序关系,称之为Happens-Before.要想保 ...
- cb45a_c++_STL_算法_删除_(3)_unique(唯一的意思)删除连续性的重复的数据
cb45a_c++_STL_算法_删除_(3)_unique(唯一的意思)删除连续性的重复的数据unique(b,e),删除连续性的,删除重复的数据,比如如果有两个连续的5,5,则留下一个.uniqu ...
- MFC基于CAsyncSocket套接字客户端代码示范
MFC基于CAsyncSocket套接字客户端代码示范 https://blog.csdn.net/txwtech/article/details/93016190
- WeChair项目Beta冲刺(7/10)
团队项目进行情况 1.昨日进展 Beta冲刺第七天 昨日进展: 前后端并行开发,项目按照计划有条不絮进行 2.今日安排 前端:扫码占座功能和预约功能并行开发 后端:扫码占座后端逻辑开发,编码预约 ...
- Java基础:变量、常量、作用域
JAVA基础:变量.常量.作用域 变量:可以变化的量.Java是强类型语言,每个变量都必须声明类型. Java变量是程序中最基本的存储单元,要素包括变量名,类型和作用域. //类变量 static s ...
- unable to load script from assets 'index.android bundle'
在Android手机上运行React-native项目时 报错:unable to load script from assets 'index.android bundle' ,make sure ...
- 如何判断一个String字符串不为空或这不为空字符串
如何判断一个String字符串不为空或这不为空字符串 转载兵哥LOVE坤 最后发布于2018-07-27 00:00:05 阅读数 5144 收藏 展开 1.校验不为空: String str ...
- codeforce 796C - Bank Hacking(无根树+思维)
题目 Although Inzane successfully found his beloved bone, Zane, his owner, has yet to return. To searc ...
- Zookeeper 序列化
读完这篇文章你将会收获到 在 Zookeeper 源码项目中新建模块,使用 Jute 进行序列化和反序列化 修改 Jute 中的 buffer size 来序列化/反序列化大对象 序言 从 前面的文章 ...
- 前端丨如何使用 tcb-js-sdk 实现图片上传功能
前言 tcb-js-sdk 让开发者可以在网页端使用 JavaScript 代码服务访问云开发的服务,以轻松构建自己的公众号页面或者独立的网站等 Web 服务.本文将以实现图片上传功能为例,介绍 tc ...