
Python Ethical Hacking - TROJANS Analysis(3)
BYPASSING ANTI-VIRUS PROGRAMS
AV programs detect viruses based on:
1. Code - compare files to huge databases of signatures.
->Use own code, obfuscation, useless operations, encode, pack ...etc
2. Behaviour - run a file in a sandbox and analyze it.
-> Run trusted operations before evil code.
->Delay execution of evil code.
Scan the file on the following website:
NoDistribute - Online Virus Scanner Without Result Distribution
Using UPX to Package the executable program.
Download the file from https://github.com/upx/upx/releases/download/v3.95/upx-3.95-amd64_linux.tar.xz.
And extract to the /opt folder.
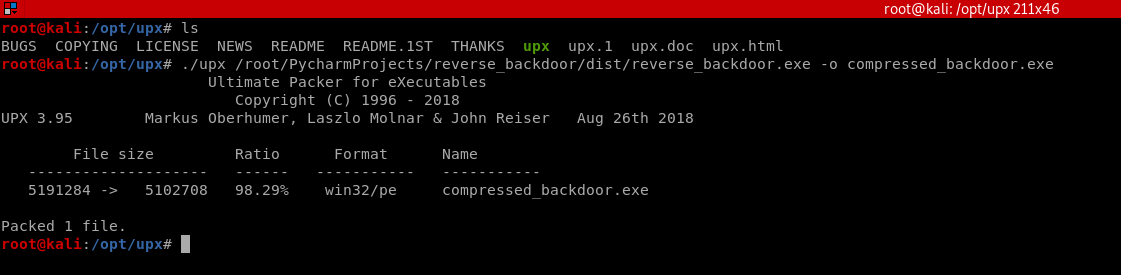
Compress the evil file through UPX.
./upx /root/PycharmProjects/reverse_backdoor/dist/reverse_backdoor.exe -o compressed_backdoor.exe
Scan the compressed_backdoor.exe file, the result is a little better.
Take your file Unique and delay to execute the evil code to let the AV program think your program is harmless.
Python Ethical Hacking - TROJANS Analysis(3)的更多相关文章
- Python Ethical Hacking - TROJANS Analysis(2)
DOWNLOAD & EXECUTE PAYLOAD A generic executable that downloads & executes files. Disadvantag ...
- Python Ethical Hacking - TROJANS Analysis(1)
TROJANS A trojan is a file that looks and functions as a normal file(image, pdf, song ..etc). When e ...
- Python Ethical Hacking - TROJANS Analysis(4)
Adding Icons to Generated Executables Prepare a proper icon file. https://www.iconfinder.com/ Conver ...
- Python Ethical Hacking - TROJANS Analysis(5)
Spoofing File Extention - A trick. Use the Kali Linux Program - Characters 1. Open the program. 2. F ...
- Python Ethical Hacking - Malware Analysis(1)
WRITING MALWARE Download file. Execute Code. Send Report. Download & Execute. Execute & Repo ...
- Python Ethical Hacking - Malware Analysis(4)
DOWNLOAD_FILE Download files on a system. Once packaged properly will work on all operating systems. ...
- Python Ethical Hacking - Malware Analysis(3)
Stealing WiFi Password Saved on a Computer #!/usr/bin/env python import smtplib import subprocess im ...
- Python Ethical Hacking - Malware Analysis(2)
Filtering Command Output using Regex #!/usr/bin/env python import smtplib import subprocess import r ...
- Python Ethical Hacking - BACKDOORS(8)
Cross-platform hacking All programs we wrote are pure python programs They do not rely on OS-specifi ...
随机推荐
- tensorflow-TFRecord 文件详解
TFRecord 是 tensorflow 内置的文件格式,它是一种二进制文件,具有以下优点: 1. 统一各种输入文件的操作 2. 更好的利用内存,方便复制和移动 3. 将二进制数据和标签(label ...
- cc28c_demo.cpp,派生类的构造函数和析构函数-代码示范3
cc28c_demo.cpp,派生类的构造函数和析构函数-代码示范3 //派生类的构造函数和析构函数//派生类的构造函数(执行步骤)//--执行基类的构造函数//--执行成员对象的构造函数//--执行 ...
- C#数据结构与算法系列(十二):递归(Recursion)
1.介绍 简单的说:递归就是方法自己调用自己,每次调用时传入不同的变量,递归有助于编程者解决复杂的问题,同时也让代码变得整洁 2.规则 执行一个方法时,就创建一个新的受保护的独立空间(栈空间) 方法的 ...
- mybatis缓存之一级缓存(一)
对于mybatis框架.仿佛工作中一直是在copy着使用.对于mybatis缓存.并没有一个准确的认知.趁着假期.学习下mybatis的缓存.这篇主要学习mybatis的一级缓存. 为什么使用缓存 其 ...
- springboot使用多个@RestControllerAdvice时的拦截顺序
我们的项目中经常会使用到别人的模块,例如我的项目demo,要依赖别人的A模块,以及基础的核心core模块,此时core模块有一个使用了@RestControllerAdvice的类,负责拦截所有的co ...
- Python干货整理之数据结构篇
1 stack的实现 实现接口: init() 用于初始化stack,数据类型为list size() 用于获得stack的大小 push() 用于往栈中添加元素,添加的元素类型可以是int或者lis ...
- vue基础入门(3)
3.组件基础 3.1.什么是组件? 3.1.1.理解组件 前端组件化开发是目前非常流行的方式,什么是前端组件化开发呢?就是将页面的某一部分独立出来,将这一部分的数据.视图.以及一些控制逻辑封装到一个组 ...
- Java使用IO流读取TXT文件
通过BufferedReader读取TXT文件window系统默认的编码是GBK,而IDE的编码多数为UTF-8,如果没有规定new InputStreamReader(new FileInputSt ...
- 循环&&数组&&方法&&面向对象
day03 数值的默认值 类型 初始化的值 byte,short,int,long 0 float,double 0.0 char 空格 boolean false 引用类型 null JVM的内存 ...
- mysql根据一张表更新另一张表数据
UPDATE channelcountry, appywproducts SET channelcountry.ChannelName = appywproducts.YWNameCN WHERE c ...