
Ethical Hacking - NETWORK PENETRATION TESTING(6)
Creating a fake access point (honeypot)
Fake access points can be handy in many scenarios, one example is creating an open AP, this will attract a lot of clients, many of which will automatically connect to it. Then we can sniff all the traffic created by the clients that connect to it, and since its open, the traffic will not be encrypted!
In order to do this, we need two cards:
1. One connected to the Internet.
2. WiFi card to broadcast as an access point.
Clients now send requests to the hacker's wifi card, the hacker sets up his machine so that every request coming from the wifi card is forwarded to the 2nd card that's connected to the Internet.
The response comes back from the 2nd card, through the hacker's machine to the wifi card which forwards it to the client that requested it.
Tool: Mana-Toolkit
Mana-Toolkit makes the whole progress very simple, it automatically creates a new AP and starts sslstrip/firelamp and even attempts to bypass HSTS which is used by Gmail and Facebook.
Mana has 3 main start scripts:
1. Start-noupstream: starts an AP with NO internet connection.
2.Start-nat-simple: this starts a regular AP using Internet connection in the upstream interface.
3.start-nat-full: starts AP with an Internet connection, it also starts sslstrip, sslsplit, firelamp and attempts to bypass HSTS.
apt-get install mana-toolkit

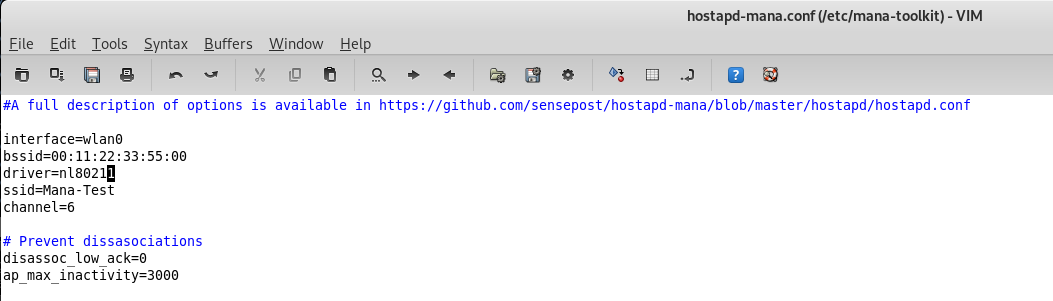
gvim /etc/mana-toolkit/hostapd-mana.conf

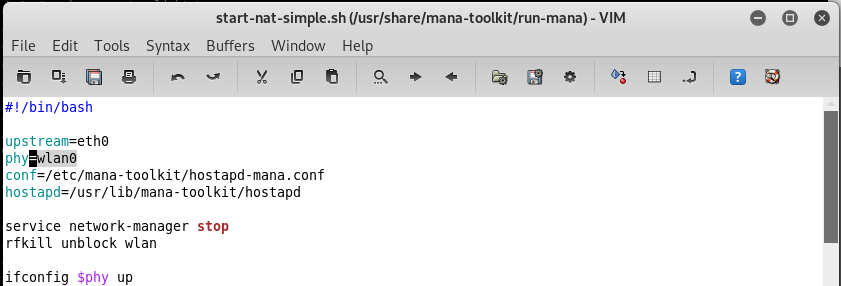
gvim /usr/share/mana-toolkit/run-mana/start-nat-simple.sh

bash /usr/share/mana-toolkit/run-mana/start-nat-simple.sh
The first ethernet card connects to the Internet.
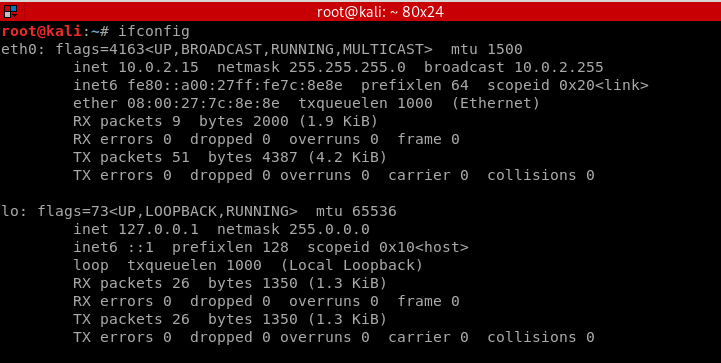
The second wifi card is ready for use.

Download and install Mana from https://github.com/sensepost/mana.
Modify the start-nat-simple.sh file.
Modify the hostpad-mana.conf file.
Run mana script successfully.
bash start-nat-simple.sh
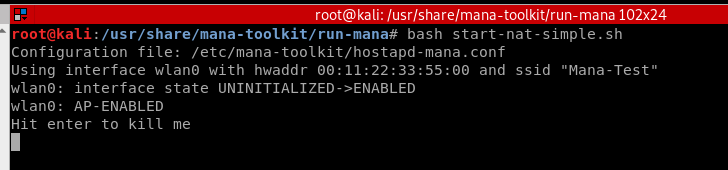
But it doesn't work well. Please see the detailed information:
https://www.slideshare.net/sensepost/improvement-in-rogue-access-points-sensepost-defcon-22
More information about hostpad setting:
https://github.com/sensepost/hostapd-mana/blob/master/hostapd/hostapd.conf
I will try Berate_ap or BetterCap later.
https://github.com/sensepost/berate_ap
https://www.bettercap.org/intro/
Ethical Hacking - NETWORK PENETRATION TESTING(6)的更多相关文章
- Ethical Hacking - NETWORK PENETRATION TESTING(15)
ARP Poisoning - arpspoof Arpspoof is a tool part of a suit called dsniff, which contains a number of ...
- Ethical Hacking - NETWORK PENETRATION TESTING(22)
MITM - Wireshark WIreshark is a network protocol analyser that is designed to help network administa ...
- Ethical Hacking - NETWORK PENETRATION TESTING(14)
MITM - ARP Poisoning Theory Man In The Middle Attacks - ARP Poisoning This is one of the most danger ...
- Ethical Hacking - NETWORK PENETRATION TESTING(13)
Nmap Nmap is a network discovery tool that can be used to gather detailed information about any clie ...
- Ethical Hacking - NETWORK PENETRATION TESTING(12)
Post Connection Attacks Sophisticated attacks that can be used after connecting to the target AP. Ga ...
- Ethical Hacking - NETWORK PENETRATION TESTING(11)
Securing your Network From the Above Attacks. Now that we know how to test the security of all known ...
- Ethical Hacking - NETWORK PENETRATION TESTING(10)
WPA Craking WPA was designed to address the issues in WEP and provide better encryption. The main is ...
- Ethical Hacking - NETWORK PENETRATION TESTING(8)
WEP Cracking Basic case Run airdump-ng to log all traffic from the target network. airodump-ng --cha ...
- Ethical Hacking - NETWORK PENETRATION TESTING(7)
Gaining Access to encrypted networks Three main encryption types: 1. WEP 2.WPA 3.WPA2 WEP Cracking W ...
- Ethical Hacking - NETWORK PENETRATION TESTING(5)
Deauthentication Attacks Theory This attack is used to disconnect any device from any network within ...
随机推荐
- 浅谈typeof 和instanceof
typeof vs instanceof 涉及面试题:typeof 是否能正确判断类型?instanceof 能正确判断对象的原理是什么? typeof 对于原始类型来说,除了 null 都可以显示正 ...
- Flutter学习笔记(35)--通知Notification
如需转载,请注明出处:Flutter学习笔记(35)--通知Notification 通知的NotificationListener和我们之前写的事件的Listener一样,都是功能性的组件,而且也都 ...
- selenium(1)-详细解读元素定位的八种方式
安装selenium和下载webdriver 安装selenium pip install selenium pip install selenium -U (判断是否有最新版本) 下载drive ...
- 能被 K 整除的最大连续子串长度
[来源]网上流传的2017美团秋招笔试题 [问题描述] 两个测试样例输出都是5 [算法思路] 暴力解法时间会超限,使用一种很巧妙的数学方法.用在读取数组arr时用数组sum记录其前 i 项的和,即 s ...
- selenium3.0-selenium发展史
- eclipse .project文件 .classpath文件的作用
.classpath文件的作用 可以参考.classpath文件的作用 .project文件的作用 确保你自己的eclipse能创建Java项目,并且正确编译运行helloworld,给eclipse ...
- java scoket Blocking 阻塞IO socket通信四
记住NIO在jdk1.7版本之前是同步非阻塞的,以前的inputsream是同步阻塞的,上面学习完成了Buffer现在我们来学习channel channel书双向的,以前阻塞的io的inputstr ...
- Python3-datetime模块-日期与时间
官方文档 http://python.usyiyi.cn/translate/python_352/library/datetime.html 代码示例 from datetime import da ...
- js基础练习题(1)
1.字符串 视频教程地址: js基础练习题 1.如何连接两个或者两个以上字符串? var cssname = 'box' var num = 1 var html = '<div class=& ...
- python读取文件路径
不同系统对文件路径的分割符不同: 在Windows系统下的分隔符是:\ (反斜杠). 在Linux系统下的分隔符是:/(斜杠). 绝对路径和相对路径 绝对路径就是文件的真正存在的路径,是指从硬盘的根目 ...