
Ethical Hacking - Web Penetration Testing(2)
INFORMATION GATHERING
- IP address.
- Domain name Info.
- Technologies used.
- Other websites on the same server.
- DNS records.
- Unlisted files, sub-domains, directories.
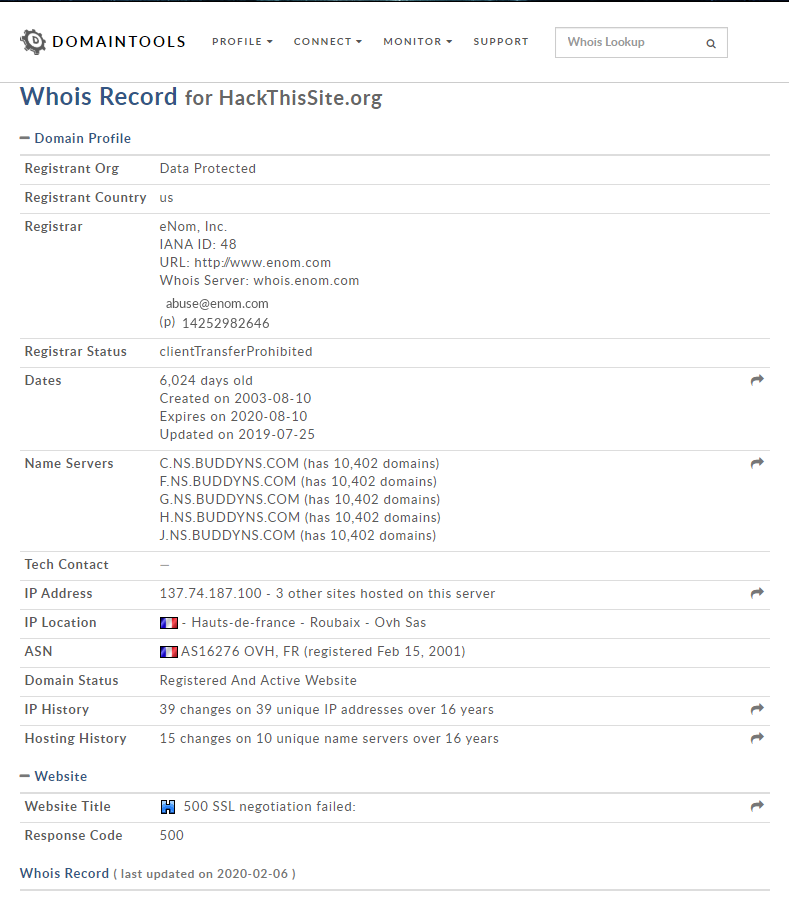
1. Whois Lookup - Find info about the owner of the target. ()
-> http://whois.domaintools.com/ https://www.whois.net/ etc.
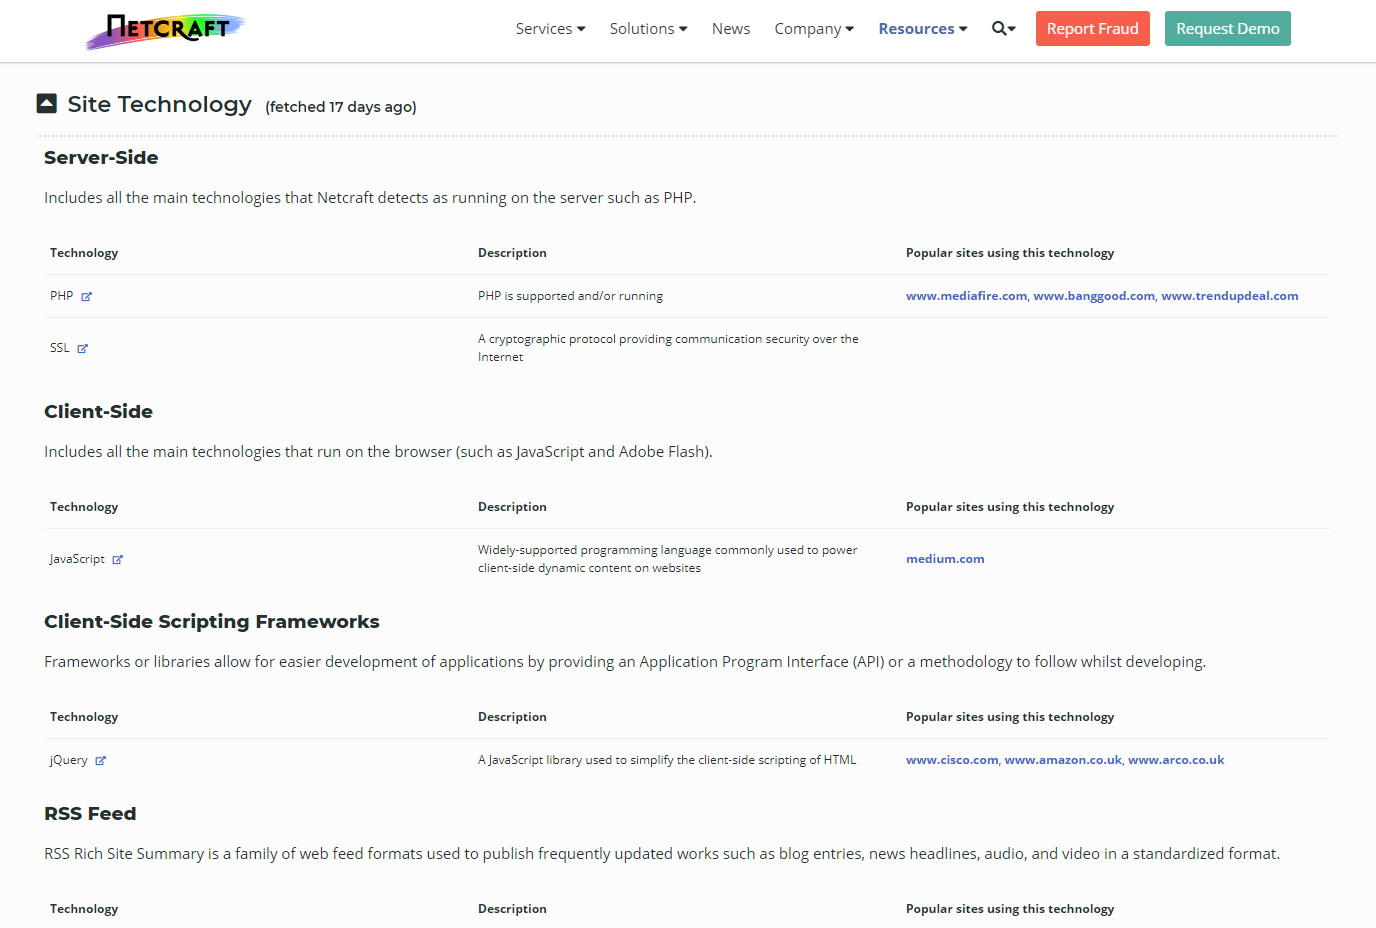
2. Netcraft Site Report - Shows technologies used on the target.
-> http://toolbar.netcraft.com/site_report
Such as :https://sitereport.netcraft.com/?url=https%3A%2F%2Fwww.hackthissite.org%2F
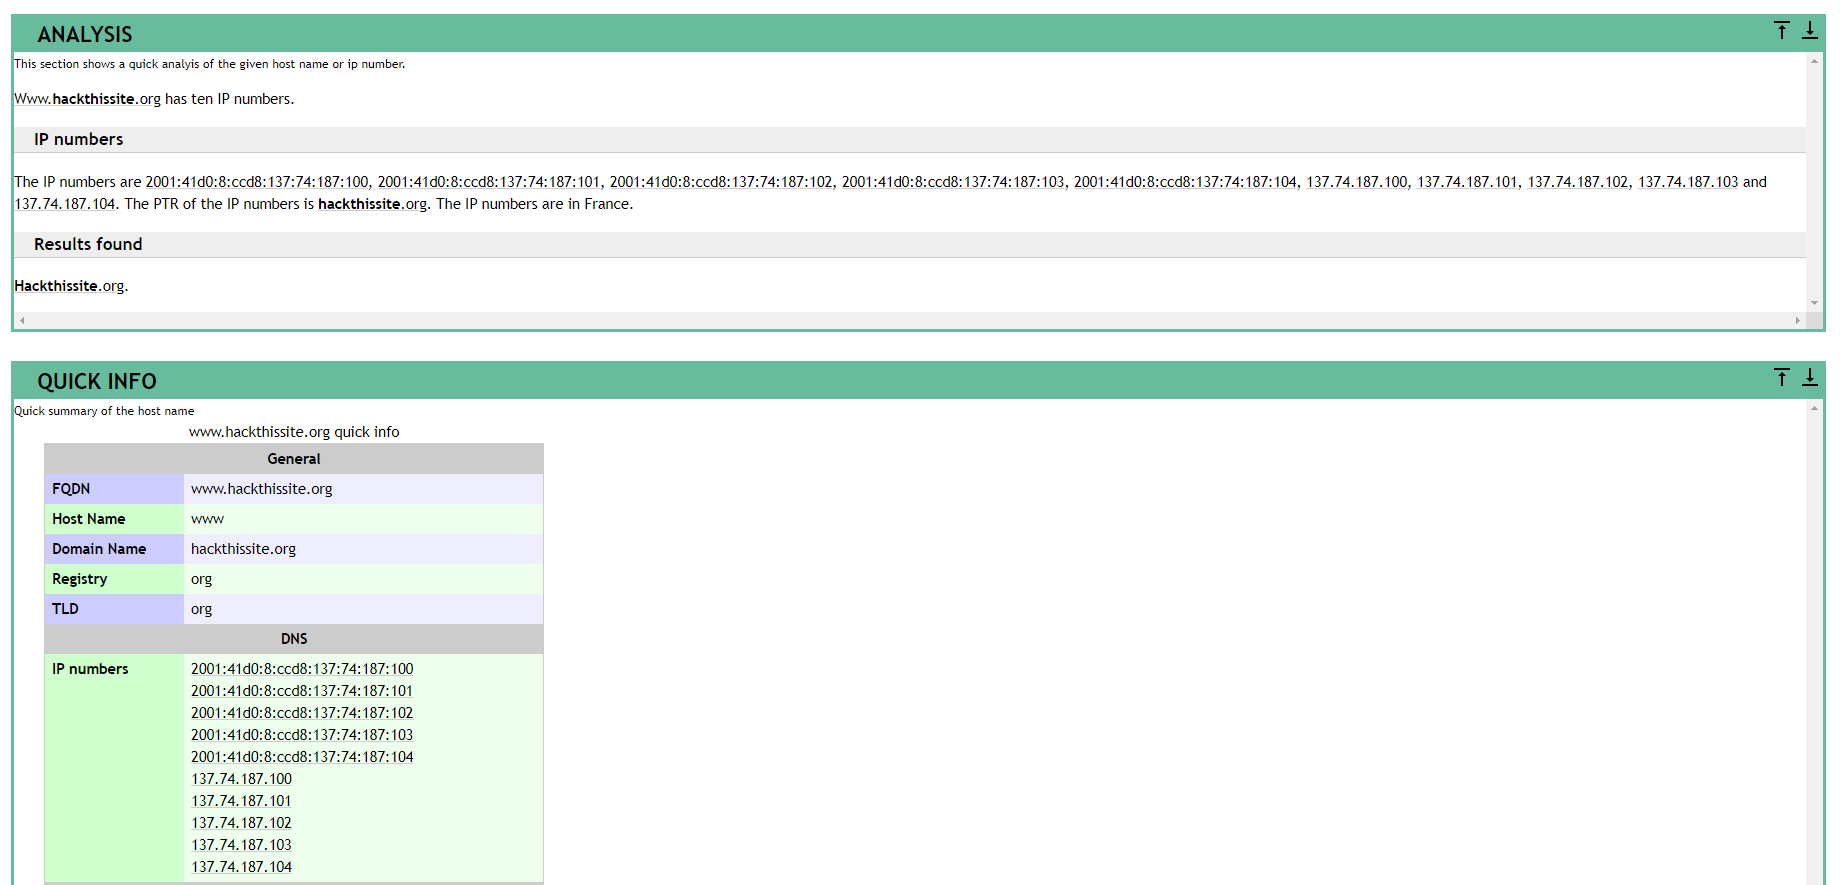
3. Robtex DNS lookup - Shows comprehensive info about the target website.
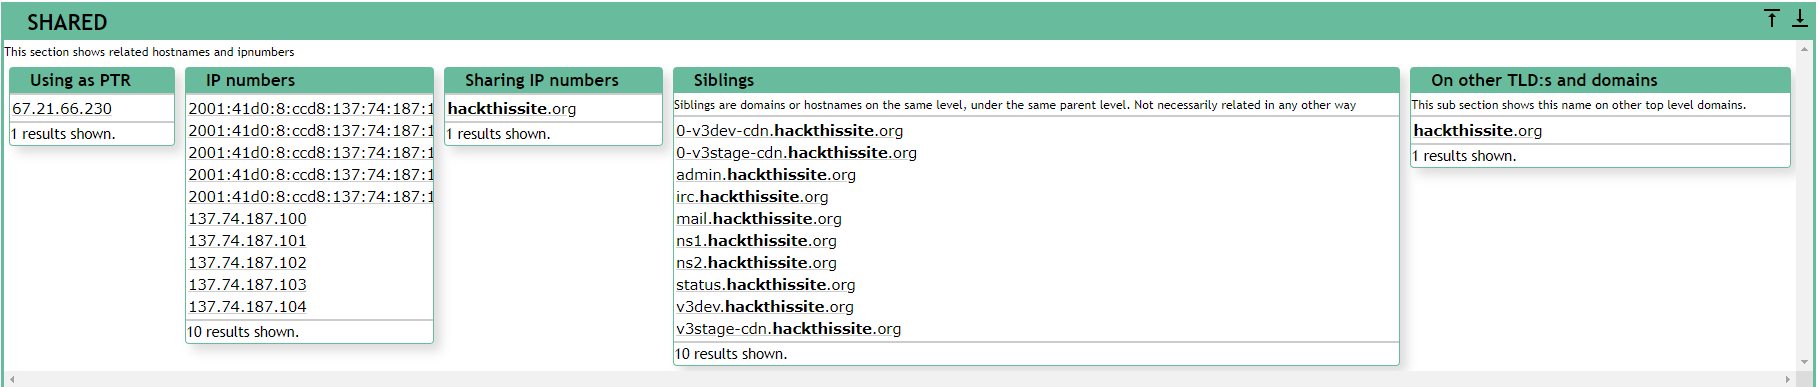
4. Discovering Websites On the Same Server
- One server can serve a number of websites.
- Gaining access to one can help gaining access to others.
To find websites on the same server:
(1) Use Robtex DNS lookup under"names pointing to same IP".
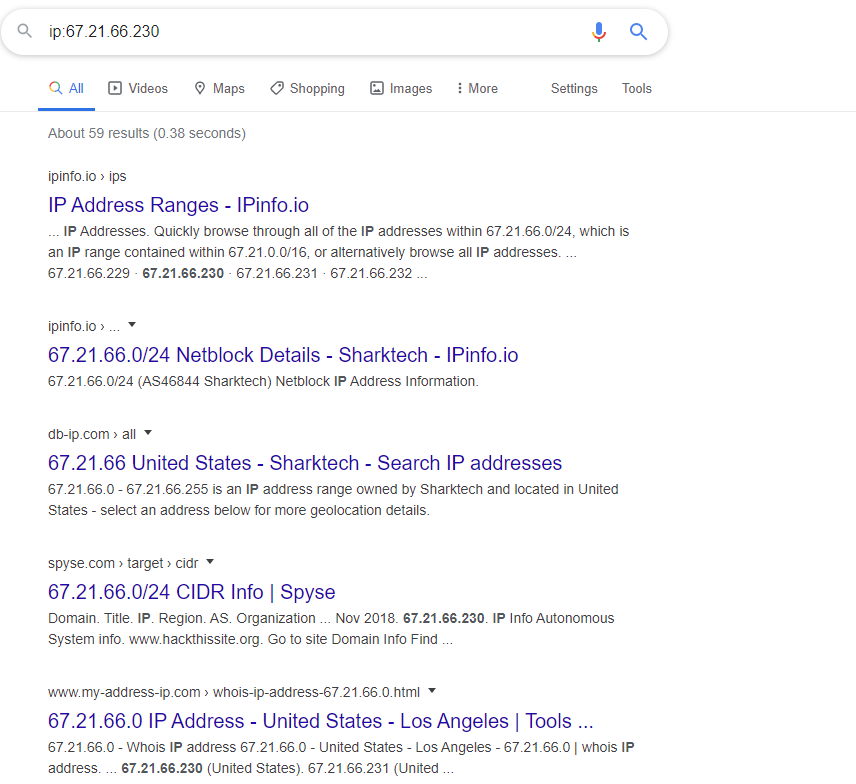
(2) Using bing.com, search for ip:[target ip]
5. Discovering subdomains
- Subdomain.target.com
- Ex:https://www.hackthissite.org/
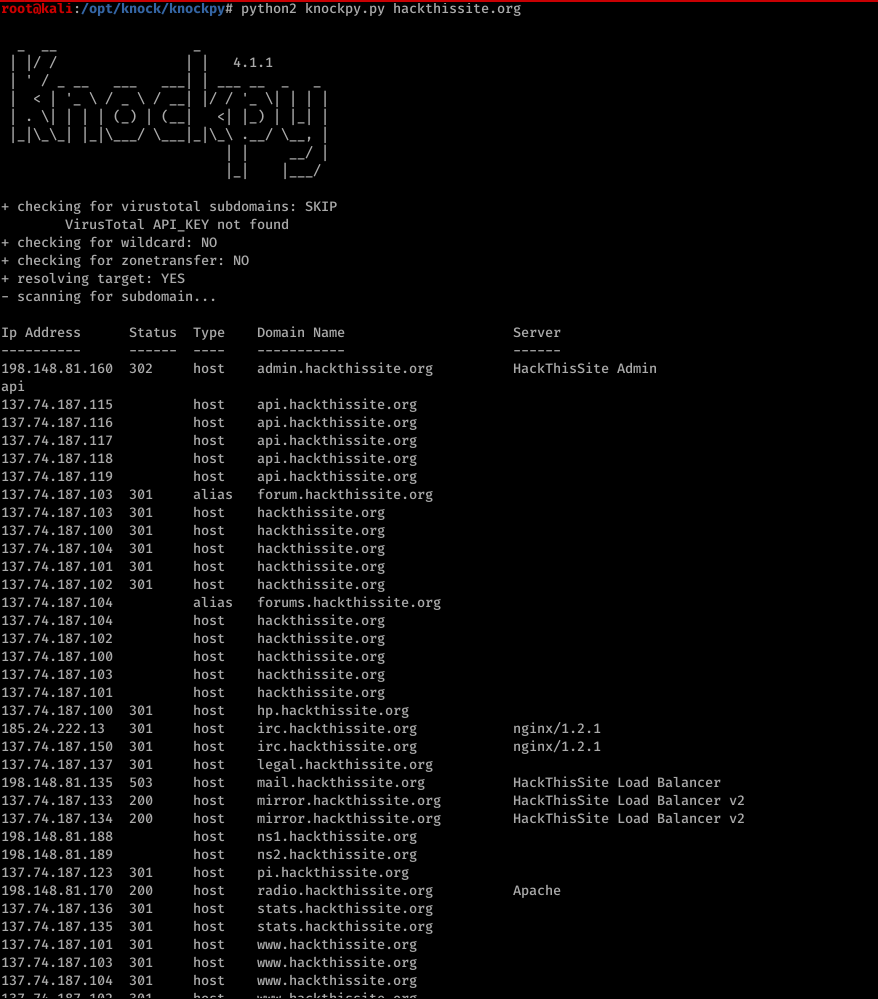
Knock can be used to find subdomainings of target.
(1)Download > git clone https://github.com/guelfoweb/knock.git
(2)Navigate to knock.py >cd knock/knock.py
(3)Run it > python knock.py [target]
6. Discovering Sensitive Files
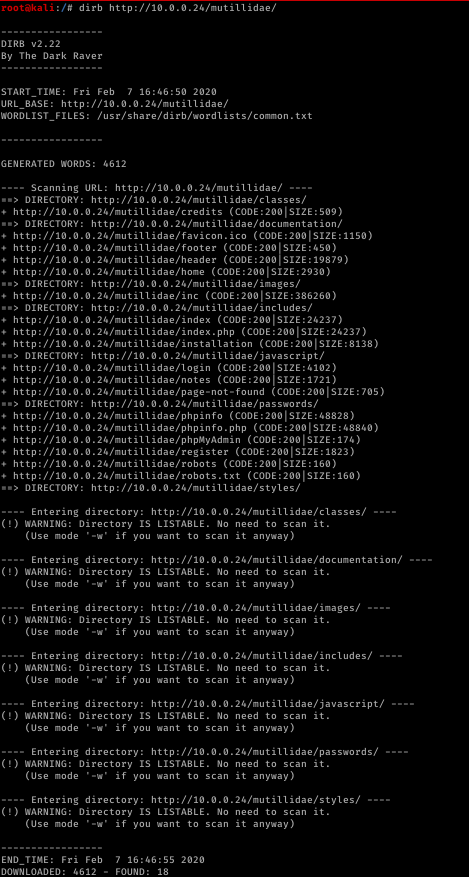
Find files&directories in target website
Tool: drib
dirb [target] [worlist] [options]
For more info run > man dirb
Analysing Discovered Files
---- Scanning URL: http://10.0.0.24/mutillidae/ ----

==> DIRECTORY: http://10.0.0.24/mutillidae/classes/

+ http://10.0.0.24/mutillidae/credits (CODE:200|SIZE:509)

==> DIRECTORY: http://10.0.0.24/mutillidae/documentation/

+ http://10.0.0.24/mutillidae/favicon.ico (CODE:200|SIZE:1150)

+ http://10.0.0.24/mutillidae/footer (CODE:200|SIZE:450)

+ http://10.0.0.24/mutillidae/header (CODE:200|SIZE:19879)

+ http://10.0.0.24/mutillidae/home (CODE:200|SIZE:2930)

==> DIRECTORY: http://10.0.0.24/mutillidae/images/

+ http://10.0.0.24/mutillidae/inc (CODE:200|SIZE:386260)

==> DIRECTORY: http://10.0.0.24/mutillidae/includes/

+ http://10.0.0.24/mutillidae/index (CODE:200|SIZE:24237)

+ http://10.0.0.24/mutillidae/index.php (CODE:200|SIZE:24237)

+ http://10.0.0.24/mutillidae/installation (CODE:200|SIZE:8138)

==> DIRECTORY: http://10.0.0.24/mutillidae/javascript/

+ http://10.0.0.24/mutillidae/login (CODE:200|SIZE:4102)

+ http://10.0.0.24/mutillidae/notes (CODE:200|SIZE:1721)

+ http://10.0.0.24/mutillidae/page-not-found (CODE:200|SIZE:705)

==> DIRECTORY: http://10.0.0.24/mutillidae/passwords/

+ http://10.0.0.24/mutillidae/phpinfo (CODE:200|SIZE:48828)

+ http://10.0.0.24/mutillidae/phpinfo.php (CODE:200|SIZE:48840)

+ http://10.0.0.24/mutillidae/phpMyAdmin (CODE:200|SIZE:174)

+ http://10.0.0.24/mutillidae/register (CODE:200|SIZE:1823)

+ http://10.0.0.24/mutillidae/robots (CODE:200|SIZE:160)

+ http://10.0.0.24/mutillidae/robots.txt (CODE:200|SIZE:160)

==> DIRECTORY: http://10.0.0.24/mutillidae/styles/

---- Entering directory: http://10.0.0.24/mutillidae/classes/ ----

(!) WARNING: Directory IS LISTABLE. No need to scan it.

    (Use mode '-w' if you want to scan it anyway)

---- Entering directory: http://10.0.0.24/mutillidae/documentation/ ----

(!) WARNING: Directory IS LISTABLE. No need to scan it.

    (Use mode '-w' if you want to scan it anyway)

---- Entering directory: http://10.0.0.24/mutillidae/images/ ----

(!) WARNING: Directory IS LISTABLE. No need to scan it.

    (Use mode '-w' if you want to scan it anyway)

---- Entering directory: http://10.0.0.24/mutillidae/includes/ ----

(!) WARNING: Directory IS LISTABLE. No need to scan it.

    (Use mode '-w' if you want to scan it anyway)

---- Entering directory: http://10.0.0.24/mutillidae/javascript/ ----

(!) WARNING: Directory IS LISTABLE. No need to scan it.

    (Use mode '-w' if you want to scan it anyway)

---- Entering directory: http://10.0.0.24/mutillidae/passwords/ ----

(!) WARNING: Directory IS LISTABLE. No need to scan it.

    (Use mode '-w' if you want to scan it anyway)

---- Entering directory: http://10.0.0.24/mutillidae/styles/ ----

(!) WARNING: Directory IS LISTABLE. No need to scan it.

    (Use mode '-w' if you want to scan it anyway)

-----------------

END_TIME: Fri Feb  7 16:46:55 2020

DOWNLOADED: 4612 - FOUND: 18
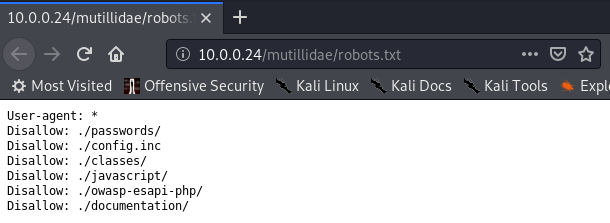
The URL in Red is useful to discove.
For example:
Gethering information is important, while it is harder to get useful information than before.
Ethical Hacking - Web Penetration Testing(2)的更多相关文章
- Ethical Hacking - Web Penetration Testing(13)
OWASP ZAP(ZED ATTACK PROXY) Automatically find vulnerabilities in web applications. Free and easy to ...
- Ethical Hacking - Web Penetration Testing(8)
SQL INJECTION WHAT IS SQL? Most websites use a database to store data. Most data stored in it(userna ...
- Ethical Hacking - Web Penetration Testing(10)
SQL INJECTION SQLMAP Tool designed to exploit SQL injections. Works with many DB types, MySQL, MSSQL ...
- Ethical Hacking - Web Penetration Testing(6)
REMOTE FILE INCLUSION Similar to local file inclusion. But allows an attacker to read ANY file from ...
- Ethical Hacking - Web Penetration Testing(1)
How to hack a website? An application installed on a computer. ->web application pen-testing A co ...
- Python Ethical Hacking - WEB PENETRATION TESTING(1)
WHAT IS A WEBSITE Computer with OS and some servers. Apache, MySQL ...etc. Cotains web application. ...
- Python Ethical Hacking - WEB PENETRATION TESTING(2)
CRAWING DIRECTORIES Directories/folders inside the web root. Can contain files or other directories ...
- Ethical Hacking - Web Penetration Testing(12)
XSS VULNS XSS - CROSS SITE SCRIPTING VULNS Allow an attacker to inject javascript code into the page ...
- Ethical Hacking - Web Penetration Testing(11)
SQL INJECTION Preventing SQLi Filters can be bypassed. Use a blacklist of commands? Still can be byp ...
- Ethical Hacking - Web Penetration Testing(9)
SQL INJECTION Discovering SQLi in GET Inject by browser URL. Selecting Data From Database Change the ...
随机推荐
- vulstack红队评估(二)
一.环境搭建: 1.根据作者公开的靶机信息整理: 靶场统一登录密码:1qaz@WSX 2.网络环境配置: ①Win2008双网卡模拟内外网: 外网:192.168.1.80,桥接模式与物理机相 ...
- docker安装,基本使用,实战
[docker概念作用术语] [使用docker的步骤] [docker安装及配置] [环境要求] docker要求centos7 必须要64位,内核3.1及以上 https://docs.docke ...
- nuget 包是如何还原包的
nuget 是如何还原包的 Intro 一直以来从来都是用 nuget 包,最近想折腾一个东西,需要自己搞一个 nuget 包的解析,用户指定 nuget 包的名称和版本,然后去解析对应的 nuget ...
- gatewayworker 安装 pcntl 扩展
安装其它扩展也是如此. 第一步,查看php版本: /phpstudy/server/php/bin/php -v 第二步,下载扩展文件: http://php.net/releases/ 这里面寻找 ...
- Dubbo想要个网关怎么办?试试整合Spring Cloud Gateway
一.背景 在微服务架构中 API网关 非常重要,网关作为全局流量入口并不单单是一个反向路由,更多的是把各个边缘服务(Web层)的各种共性需求抽取出来放在一个公共的"服务"(网关)中 ...
- git配置用户和邮箱
1. 查看git用户配置 git config user.name 2. 查看git邮箱配置 git config user.email 3. 配置git用户 git config --global ...
- 机器学习之KNN算法(分类)
KNN算法是解决分类问题的最简单的算法.同时也是最常用的算法.KNN算法也可以称作k近邻算法,是指K个最近的数据集,属于监督学习算法. 开发流程: 1.加载数据,加载成特征矩阵X与目标向量Y. 2.给 ...
- 鹅厂车联网探索:5G下边缘云计算的车路协同实践
5G网络下,多接入边缘计算(MEC)应运而生.结合TKEStack强大的集群管理能力和异构计算资源管理能力,腾讯打造了一个功能完备的边缘计算PaaS平台TMEC,提供了高精确度定位.视频处理.无线网络 ...
- 作为架构师必须知道的Netty原理和使用
本文首发于微信公众号[猿灯塔],转载引用请说明出处 今天呢!灯塔君跟大家讲: Netty应用 一.Netty简介 1.Netty下载 官网:https://netty.io/downloads.htm ...
- 03-springboot整合elasticsearch-源码初识
前面两个小节已经知道了spring boot怎么整合es,以及es的简单使用,但是springboot中是怎么和es服务器交互的.我们可以简单了解一下.要看一下源码 在看源码的同时,先要对sp ...