
Practical Web Penettation Testing (the first one Mutillidae 大黄蜂)
1、now we looke at this book . I decide to make a brief review
the book covers as follows (I straight-forward copy here):
Chapter 1, Building a Vulnerable Web Application Lab, will help us to get and
install the vulnerable application Mutillidae using Windows and Linux. Also, we
will have a quick tour of how to use this vulnerable web application.
Chapter 2, Kali Linux Installation, will explain how to download, install, and
configure Kali Linux
Chapter 3, Delving Deep into the Usage of Kali Linux, will teach more about how
to deal with Kali Linux from the Terminal window, and will help you to become
a ninja in bash scripting as well.
Chapter 4, All About Using Burp Suite, covers what you need to know about
Metasploit to fulfil the role of a web application security expert.
Chapter 5, Understanding Web Application Vulnerabilities, explains the attacks
that can happen on a web application, and after finishing the chapter, you will be
able to use these skills to manipulate your findings during pentests.
Chapter 6, Application Security Pre-Engagement, will explain how to sign all the
necessary contracts before starting the tests. Also, you will learn how to
estimate, scope, and schedule your tests before they start.
Chapter 7, Application Threat Modeling, will explains that ATM is a security
architecture document that allows you to identify future threats and to pinpoint
the different pentest activities that need to be executed in the future deployment
of the web application project.
Chapter 8, Source Code Review, covers how to deal with the source code review
process. The source code is the heart or engine of a web application, and it must
be properly constructed from a security perspective.
Chapter 9, Network Penetration Testing, explains how to use Metasploit, Nmap,
and OpenVAS together to conduct a network infrastructure vulnerability
assessment.
Chapter 10, Web Intrusion Tests, will show how to look for web application based
vulnerabilities (SQLi, XSS, and CSRF) using Burp. Also, the readers will learn
how to take advantage of, get a remote shell, and probably elevate their
privileges on the victim web server.
Chapter 11, Pentest Automation Using Python, explains how to automate
everything that we have learned using the Python language for a more
performant result.
Appendix A, Nmap Cheat Sheet, a list of the most common Nmap options.
Appendix B, Metasploit Cheat Sheet, provides a quick reference to the Metasploit
framework.
Appendix C, Netcat Cheat Sheet, provides Netcat commands and a few popular
practical examples.
Appendix D, Networking Reference Section, provides important information about
networking, such as network subnets, port number, and its services.
Appendix E, Python Quick Reference, provides a quick overview of the amazing
programming language—Python.
2、now we looke at the first paragraph
how install vulnerable web application on wondows or linux or Ubuntu the application nmae's is Mutillidae in chinese(大黄蜂)
at present how to download ,the address url : www.packtpub.com
another resource in GitHub the address url: https://github.com/PacktPublishing/Practical-web-Penetration-Testing
how to building like this :
step1 download Mutiliidae url: https:/sourceforge.net
3、install the simulation application XAMPP
the XAMPP have Apache Mysql and php functions
the download url : https://www.apachefriends.org/download.html
4、before install the XAMPP close allover antivirus,for me I have been installed another Trigger problems

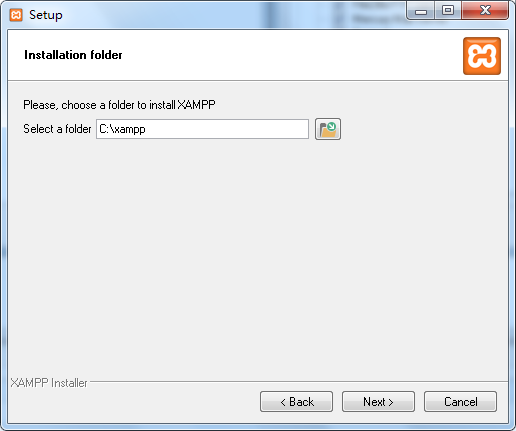
install procedur as follows : in this here I use the default path C


我的电脑启动apacheL的时候 出现异常,因为之前安装过一个类似的application DVWA。也有可能是其他软件占用了固定的端口 ,修改配置文件如下
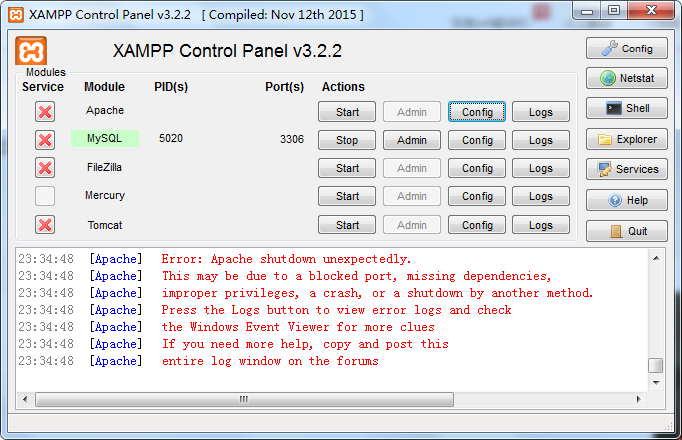
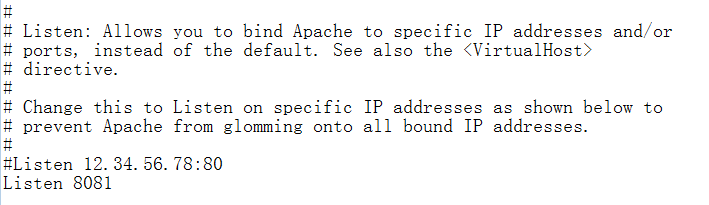
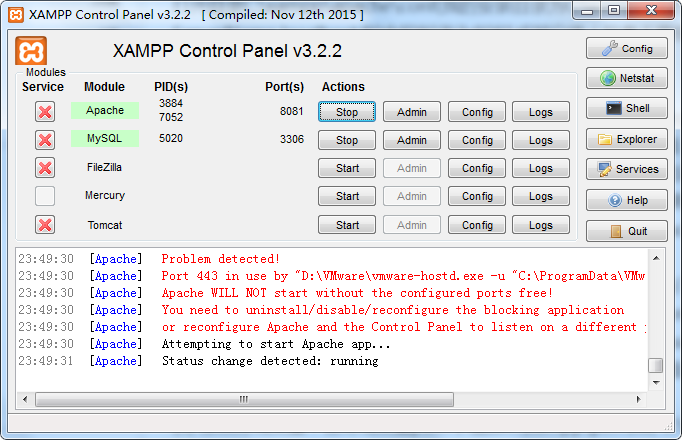
修改配置的端口后 启动成功。总结 修改一共两个端口 the one 服务端口 80 修改成8081 the second 监听端口 443 直接注释掉或者修改成1023以上的端口
5、how to install mutillidae
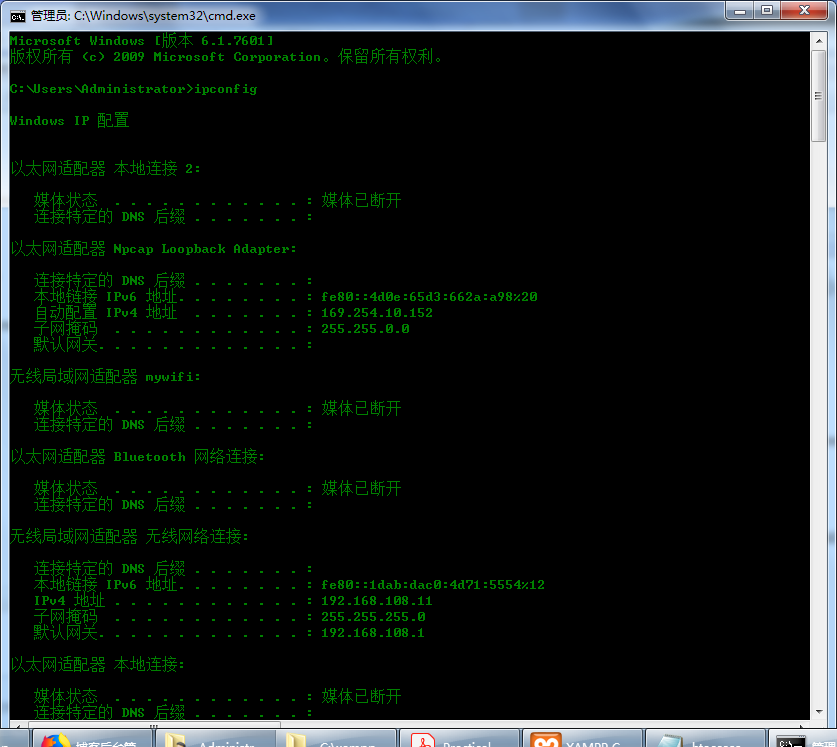
search your ip

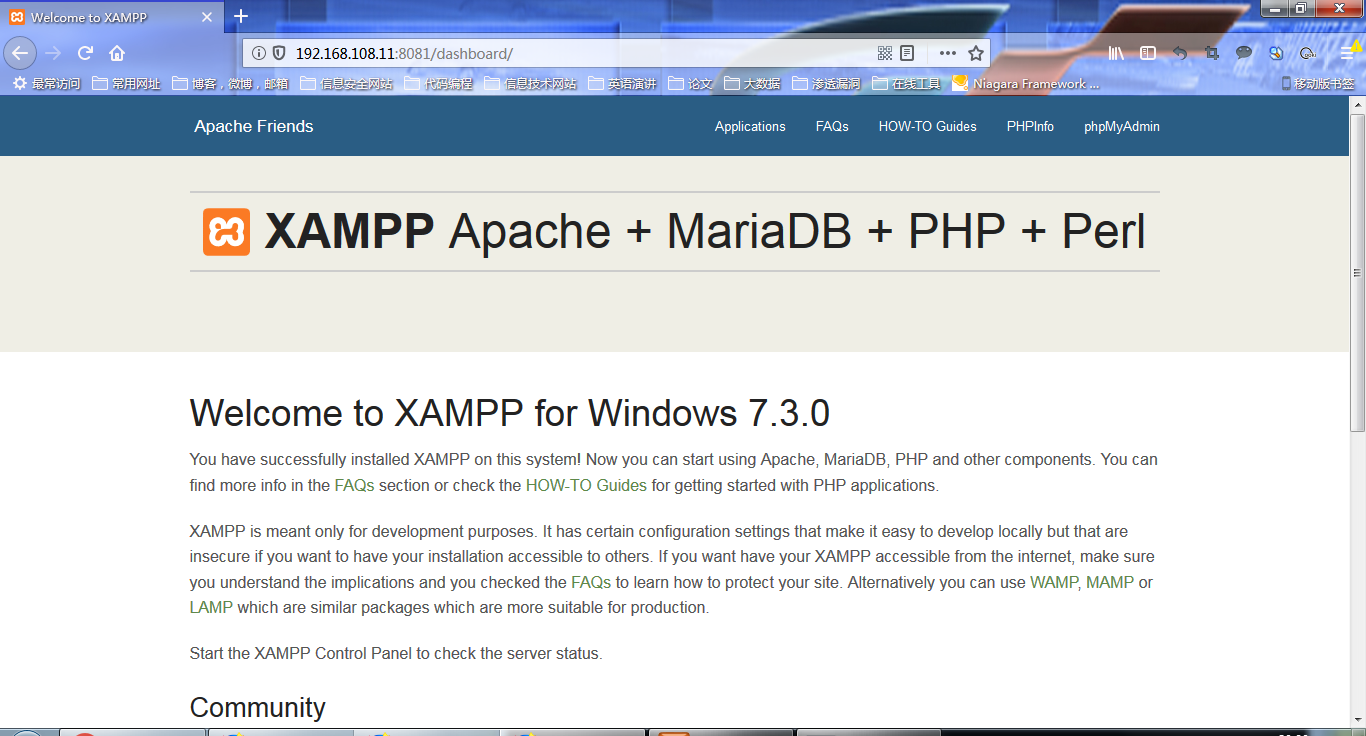
成功启动Mutillidae之后 如下
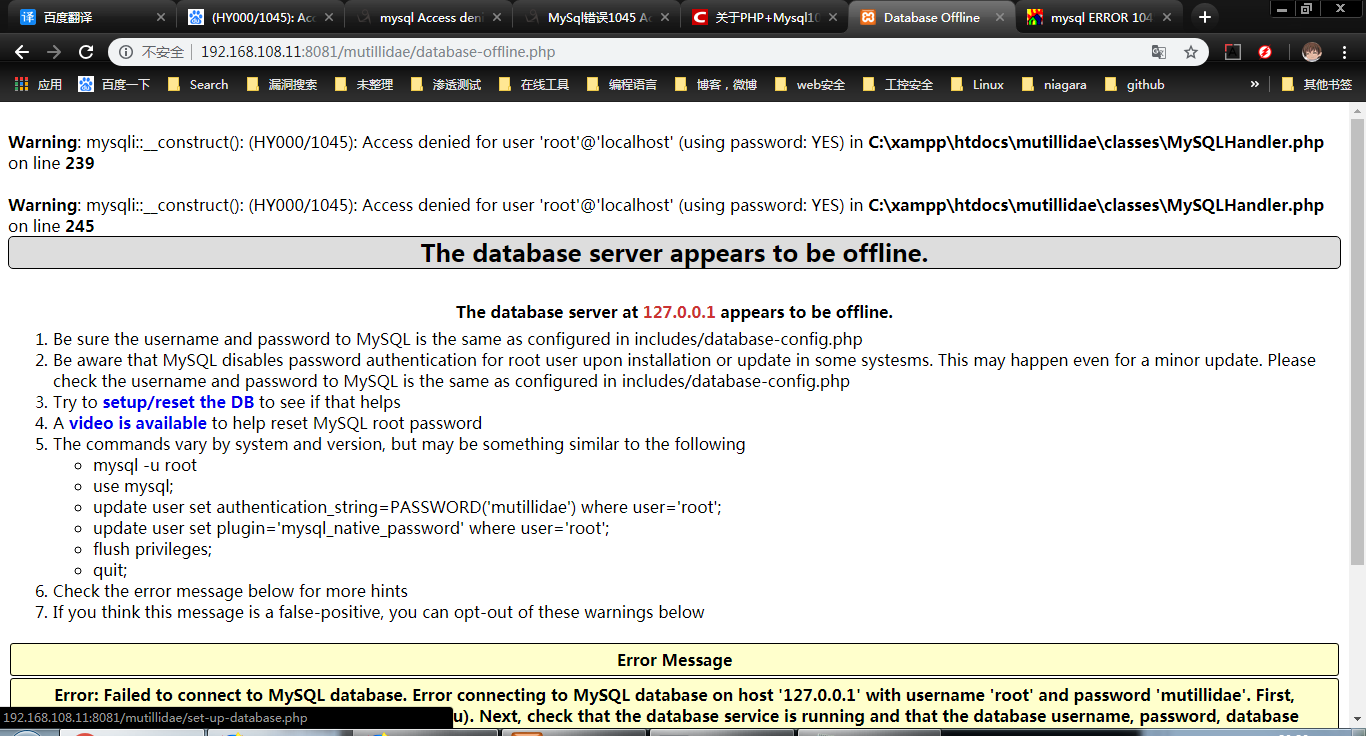
但是有时候提示出现 错误代码 1045
Access denied for user 'root'@'localhost' (using password:YES)

Practical Web Penettation Testing (the first one Mutillidae 大黄蜂)的更多相关文章
- Practical Web Penettation Testing (the first one Mutillidae 大黄蜂 之二)
1.how to use dpkg cmmand first it can be used for list all software , dpkg -l (由于kali linux 没有启动所以 ...
- 转:15 Best Responsive Web Design Testing Tools
Responsive Web Design is regarded as being the approach which suggests that web design and developme ...
- Ethical Hacking - Web Penetration Testing(13)
OWASP ZAP(ZED ATTACK PROXY) Automatically find vulnerabilities in web applications. Free and easy to ...
- Ethical Hacking - Web Penetration Testing(10)
SQL INJECTION SQLMAP Tool designed to exploit SQL injections. Works with many DB types, MySQL, MSSQL ...
- Ethical Hacking - Web Penetration Testing(8)
SQL INJECTION WHAT IS SQL? Most websites use a database to store data. Most data stored in it(userna ...
- Python Ethical Hacking - WEB PENETRATION TESTING(2)
CRAWING DIRECTORIES Directories/folders inside the web root. Can contain files or other directories ...
- Web Penetration Testing
1.国外使用的一款在线工具,对web的信息收集很有帮助 地址http://archive.org , WayBack Machine 主界面如下:对百度存档的历史信息进行查询. 2.IP地址归属信息 ...
- Ethical Hacking - Web Penetration Testing(6)
REMOTE FILE INCLUSION Similar to local file inclusion. But allows an attacker to read ANY file from ...
- Ethical Hacking - Web Penetration Testing(2)
INFORMATION GATHERING IP address. Domain name Info. Technologies used. Other websites on the same se ...
随机推荐
- Luogu P2490「JSOI2016」黑白棋
我博弈基础好差.. Luogu P2490 题意 有一个长度为$ n$的棋盘,黑白相间的放$ k$个棋子,保证$ k$是偶数且最左边为白子 每次小$ A$可以移动不超过$ d$个白子,然后小$ B$可 ...
- mysql 案例 ~ insert插入慢的场景
一简介: insert出现慢日志中,应该怎么检测呢 二 理解:事务提交延迟,一般出现在写日志延迟的情况下,会有几种可能 场景: 1 RR模式下,insert等待gap lock锁导致的 ...
- CF1110D Jongmah
题目地址:CF1110D Jongmah 约定:称形如 \([a-1,a,a+1]\) 这样的三元组为关于 \(a\) 的顺子,形如 \([a,a,a]\) 这样的三元组为关于 \(a\) 的对子. ...
- 华为QUIDWAY系列路由器的负载均衡配置
作者:邓聪聪 华为系列路由器的负载均衡NQA联动侦测配置案例: 需求:该局域网,IP地址(末位奇数)走联通,IP地址(末位偶数)走电信当某个运营商不可达时,自动切换.通过NQA来确定运营商是否可达., ...
- 【转】判断处理器是Big_endian的还是Little_endian的
首先说明一下Little_endian和Big_endian是怎么回事. Little_endian模式的CPU对操作数的存放方式是从低字节到高字节,而Big_endian模式则是从高字节到低字节,比 ...
- Codeforces 914D - Bash and a Tough Math Puzzle 线段树,区间GCD
题意: 两个操作, 单点修改 询问一段区间是否能在至多一次修改后,使得区间$GCD$等于$X$ 题解: 正确思路; 线段树维护区间$GCD$,查询$GCD$的时候记录一共访问了多少个$GCD$不被X整 ...
- Spring MVC的核心控制器DispatcherServlet的作用
关于Spring MVC的核心控制器DispatcherServlet的作用,以下说法错误的是( )? 它负责接收HTTP请求 加载配置文件 实现业务操作 初始化上下应用对象ApplicationC ...
- object oriented programming : class application
class Thread_Sync; class Critical; class Info; class Info{Info(std::string str):m_info(str){} privat ...
- C#如何使用SqlCacheDependency
1.数据库依赖类SqlCacheDependency 数据库缓存依赖主要解决的是当数据库的内容发生改变时,如何及时通知缓存,并更新缓存中的数据的问题. 语法定义: SqlCacheDependency ...
- [Linux]关于字节序的解析
剥鸡蛋的故事 <格列佛游记>中记载了两个征战的强国,你不会想到的是,他们打仗竟然和剥鸡蛋的姿势有关. 很多人认为,剥鸡蛋时应该打破鸡蛋较大的一端,这群人被称作“大端(Big endian) ...